What Is Consent Management? How It Works (and Fails) in 2026
Osman Husain
Consent management is the process of asking people for permission to collect and use their personal data, recording each answer, and making every tool on a website or app respect it until the person changes their mind.
Under the GDPR, most tracking needs opt-in consent first. California's CCPA requires an easy way to opt out.
A cookie banner is only the visible step of consent management, and most of the work happens after the click.
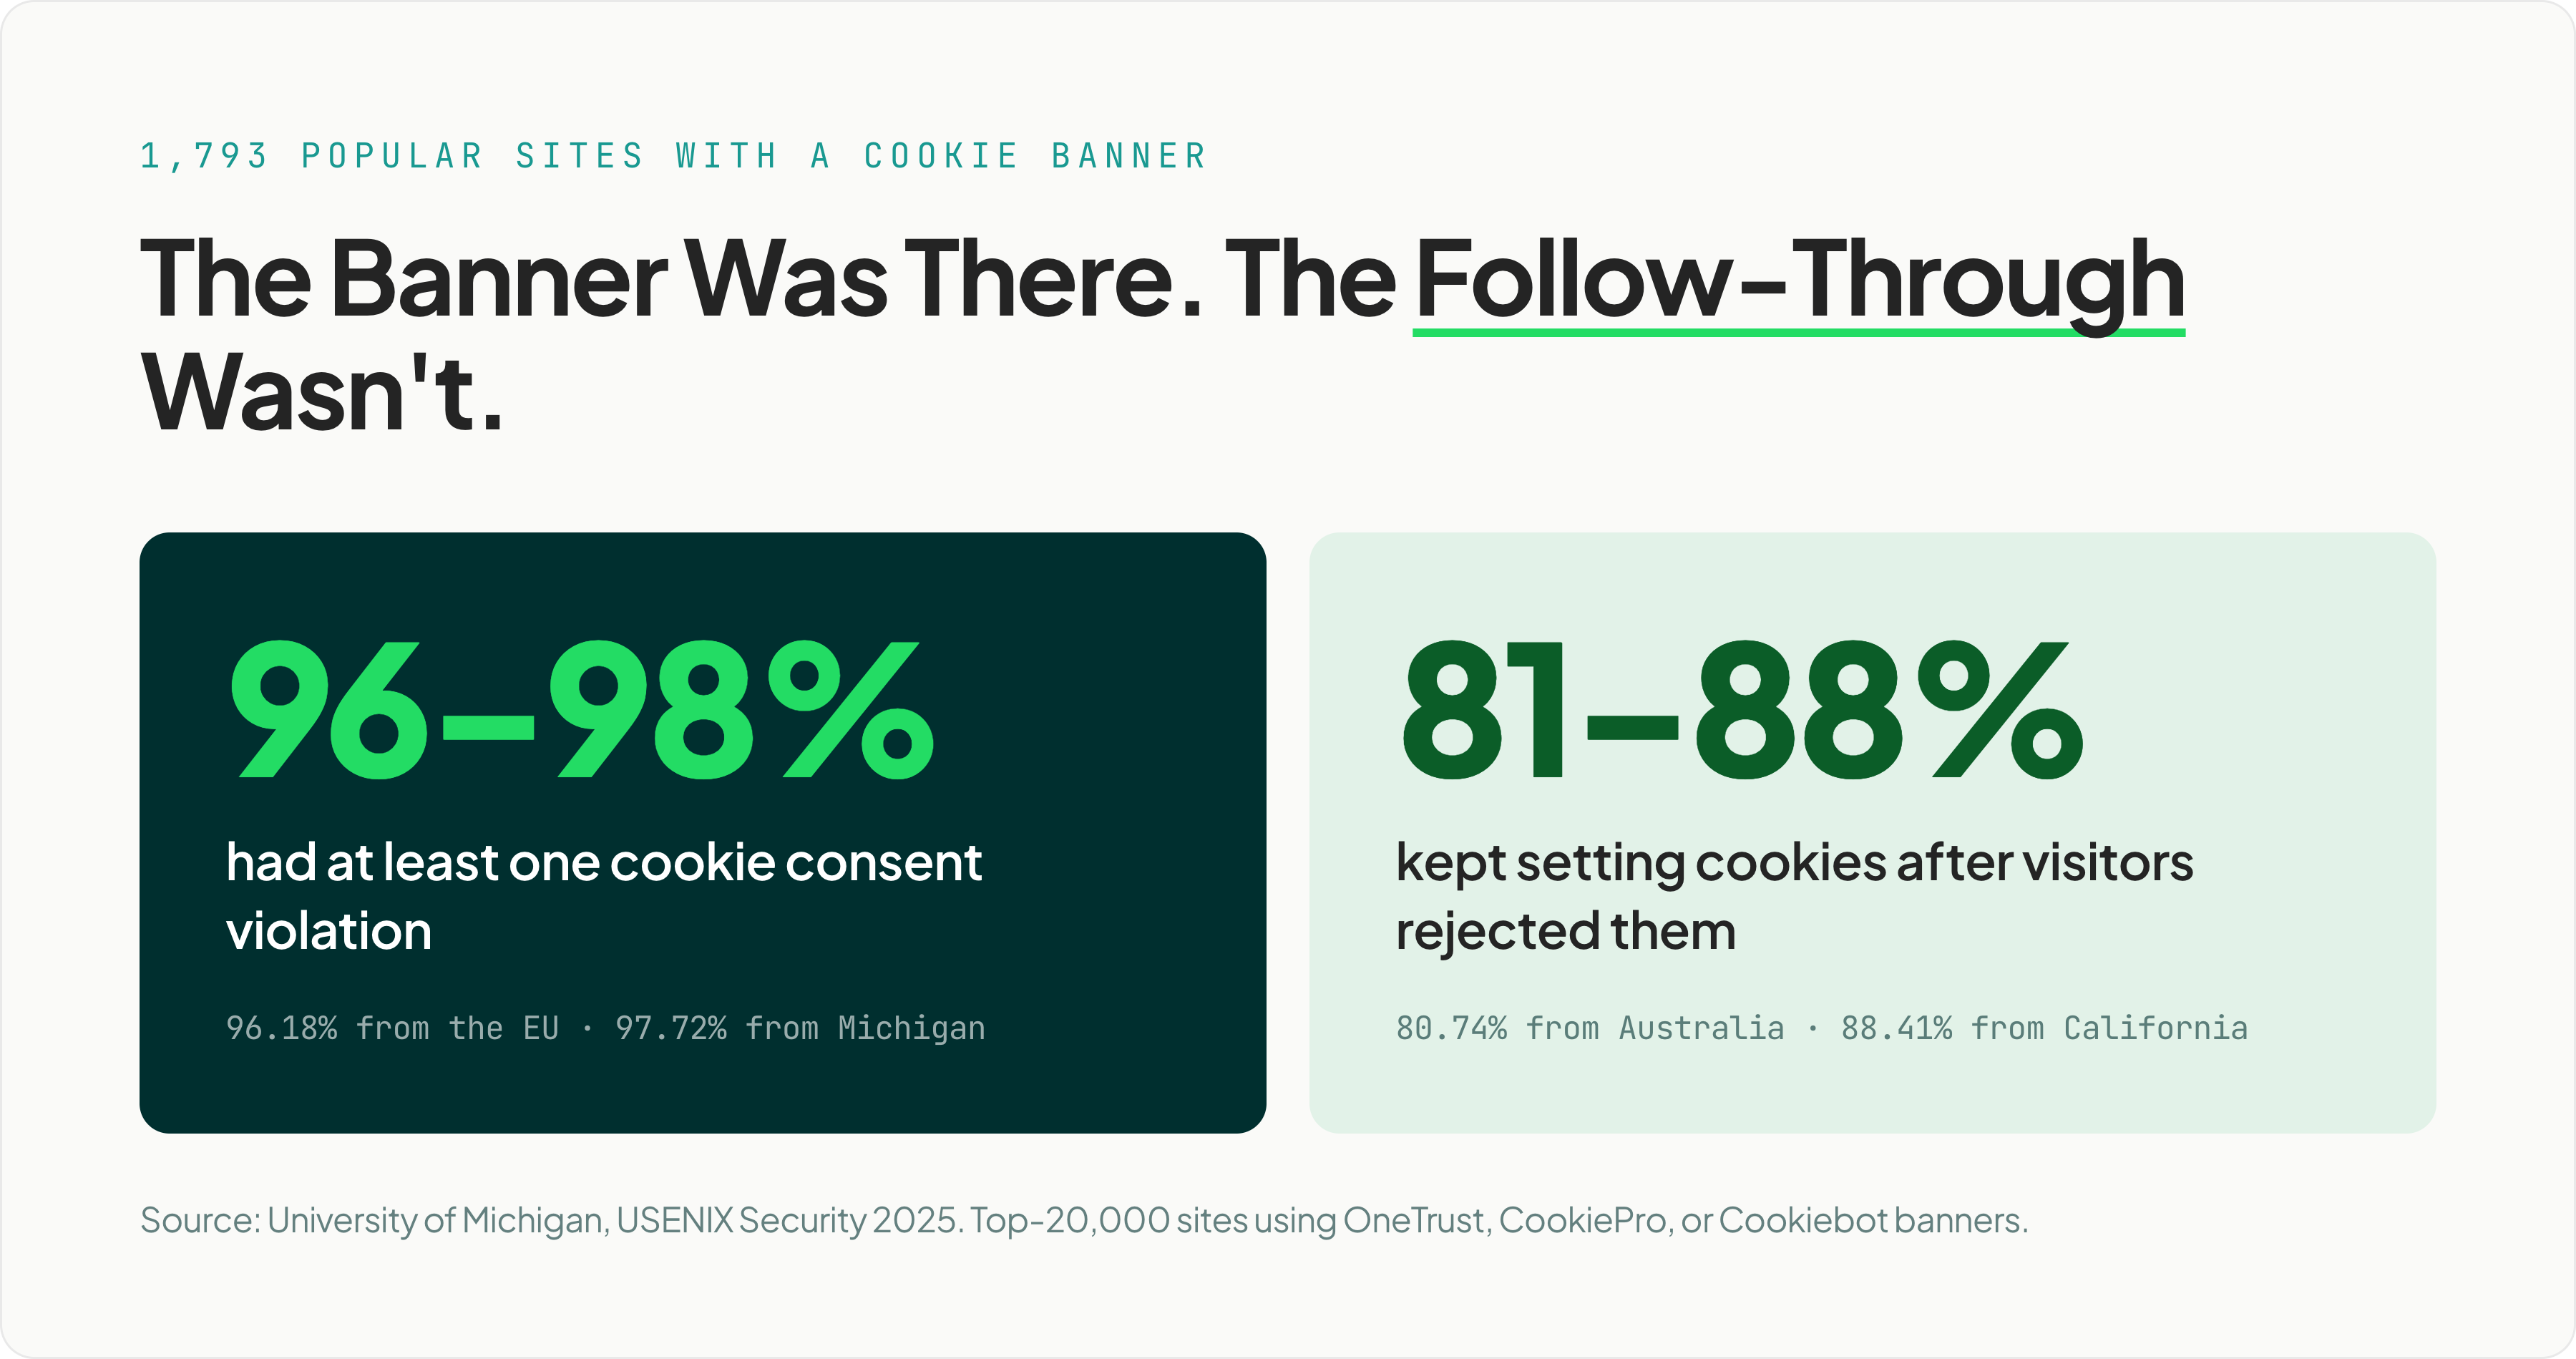
In a recent test, nearly every popular website with a cookie banner still got consent wrong somewhere. A University of Michigan team tested 1,793 popular sites running banners from three major consent platforms and found at least one consent violation on 96% to 98% of them, depending on where the visit came from.
What does consent management mean?
Consent management treats data processing permission as a record that travels with a user, from the notice a person first reads to the day that consent expires.
The GDPR defines consent as a "freely given, specific, informed and unambiguous indication" of a person's wishes, given by a statement or a clear affirmative action (Article 4(11)).
Article 7(1) adds the part that makes consent something to manage: the business must be able to demonstrate it. So every consent question comes down to three facts. Did this person consent? To what? And when?
Answering those questions is the controller's job. The controller is the organization that decides why and how personal data gets used, so it sets the consent rules and keeps the proof. A processor, such as an analytics or advertising vendor, handles data on the controller's behalf and can't go beyond the consent the controller collected.
Privacy and consent management overlap, but they aren't the same job. Privacy management also covers security, access requests, and vendor contracts. Consent management is the permission layer that decides whether data can be used at all, and the types of consent it handles range from explicit opt-in to consent implied by behavior.
Does displaying a cookie banner mean a site is managing consent properly?
A cookie banner doesn't prove a site manages consent: in the largest recent study, nearly every site with a banner still broke at least one consent rule, often by tracking visitors who said no.
In a study presented at USENIX Security 2025, University of Michigan researchers crawled 1,793 top-20,000 websites that used OneTrust, CookiePro, or Cookiebot banners. Between 96.18% (measured from the EU) and 97.72% (measured from Michigan) had at least one cookie consent violation. Between 80.74% (Australia) and 88.41% (California) kept setting cookies after visitors rejected them.
A 2024 Web Conference study found the same gap one layer down. Researchers checked 2,230 websites using the IAB's Transparency and Consent Framework. The consent signal was right on 97.8% of them: the sites stored and passed on the visitor's choice correctly. Yet 52.3% still set tracking cookies after the visitor declined.
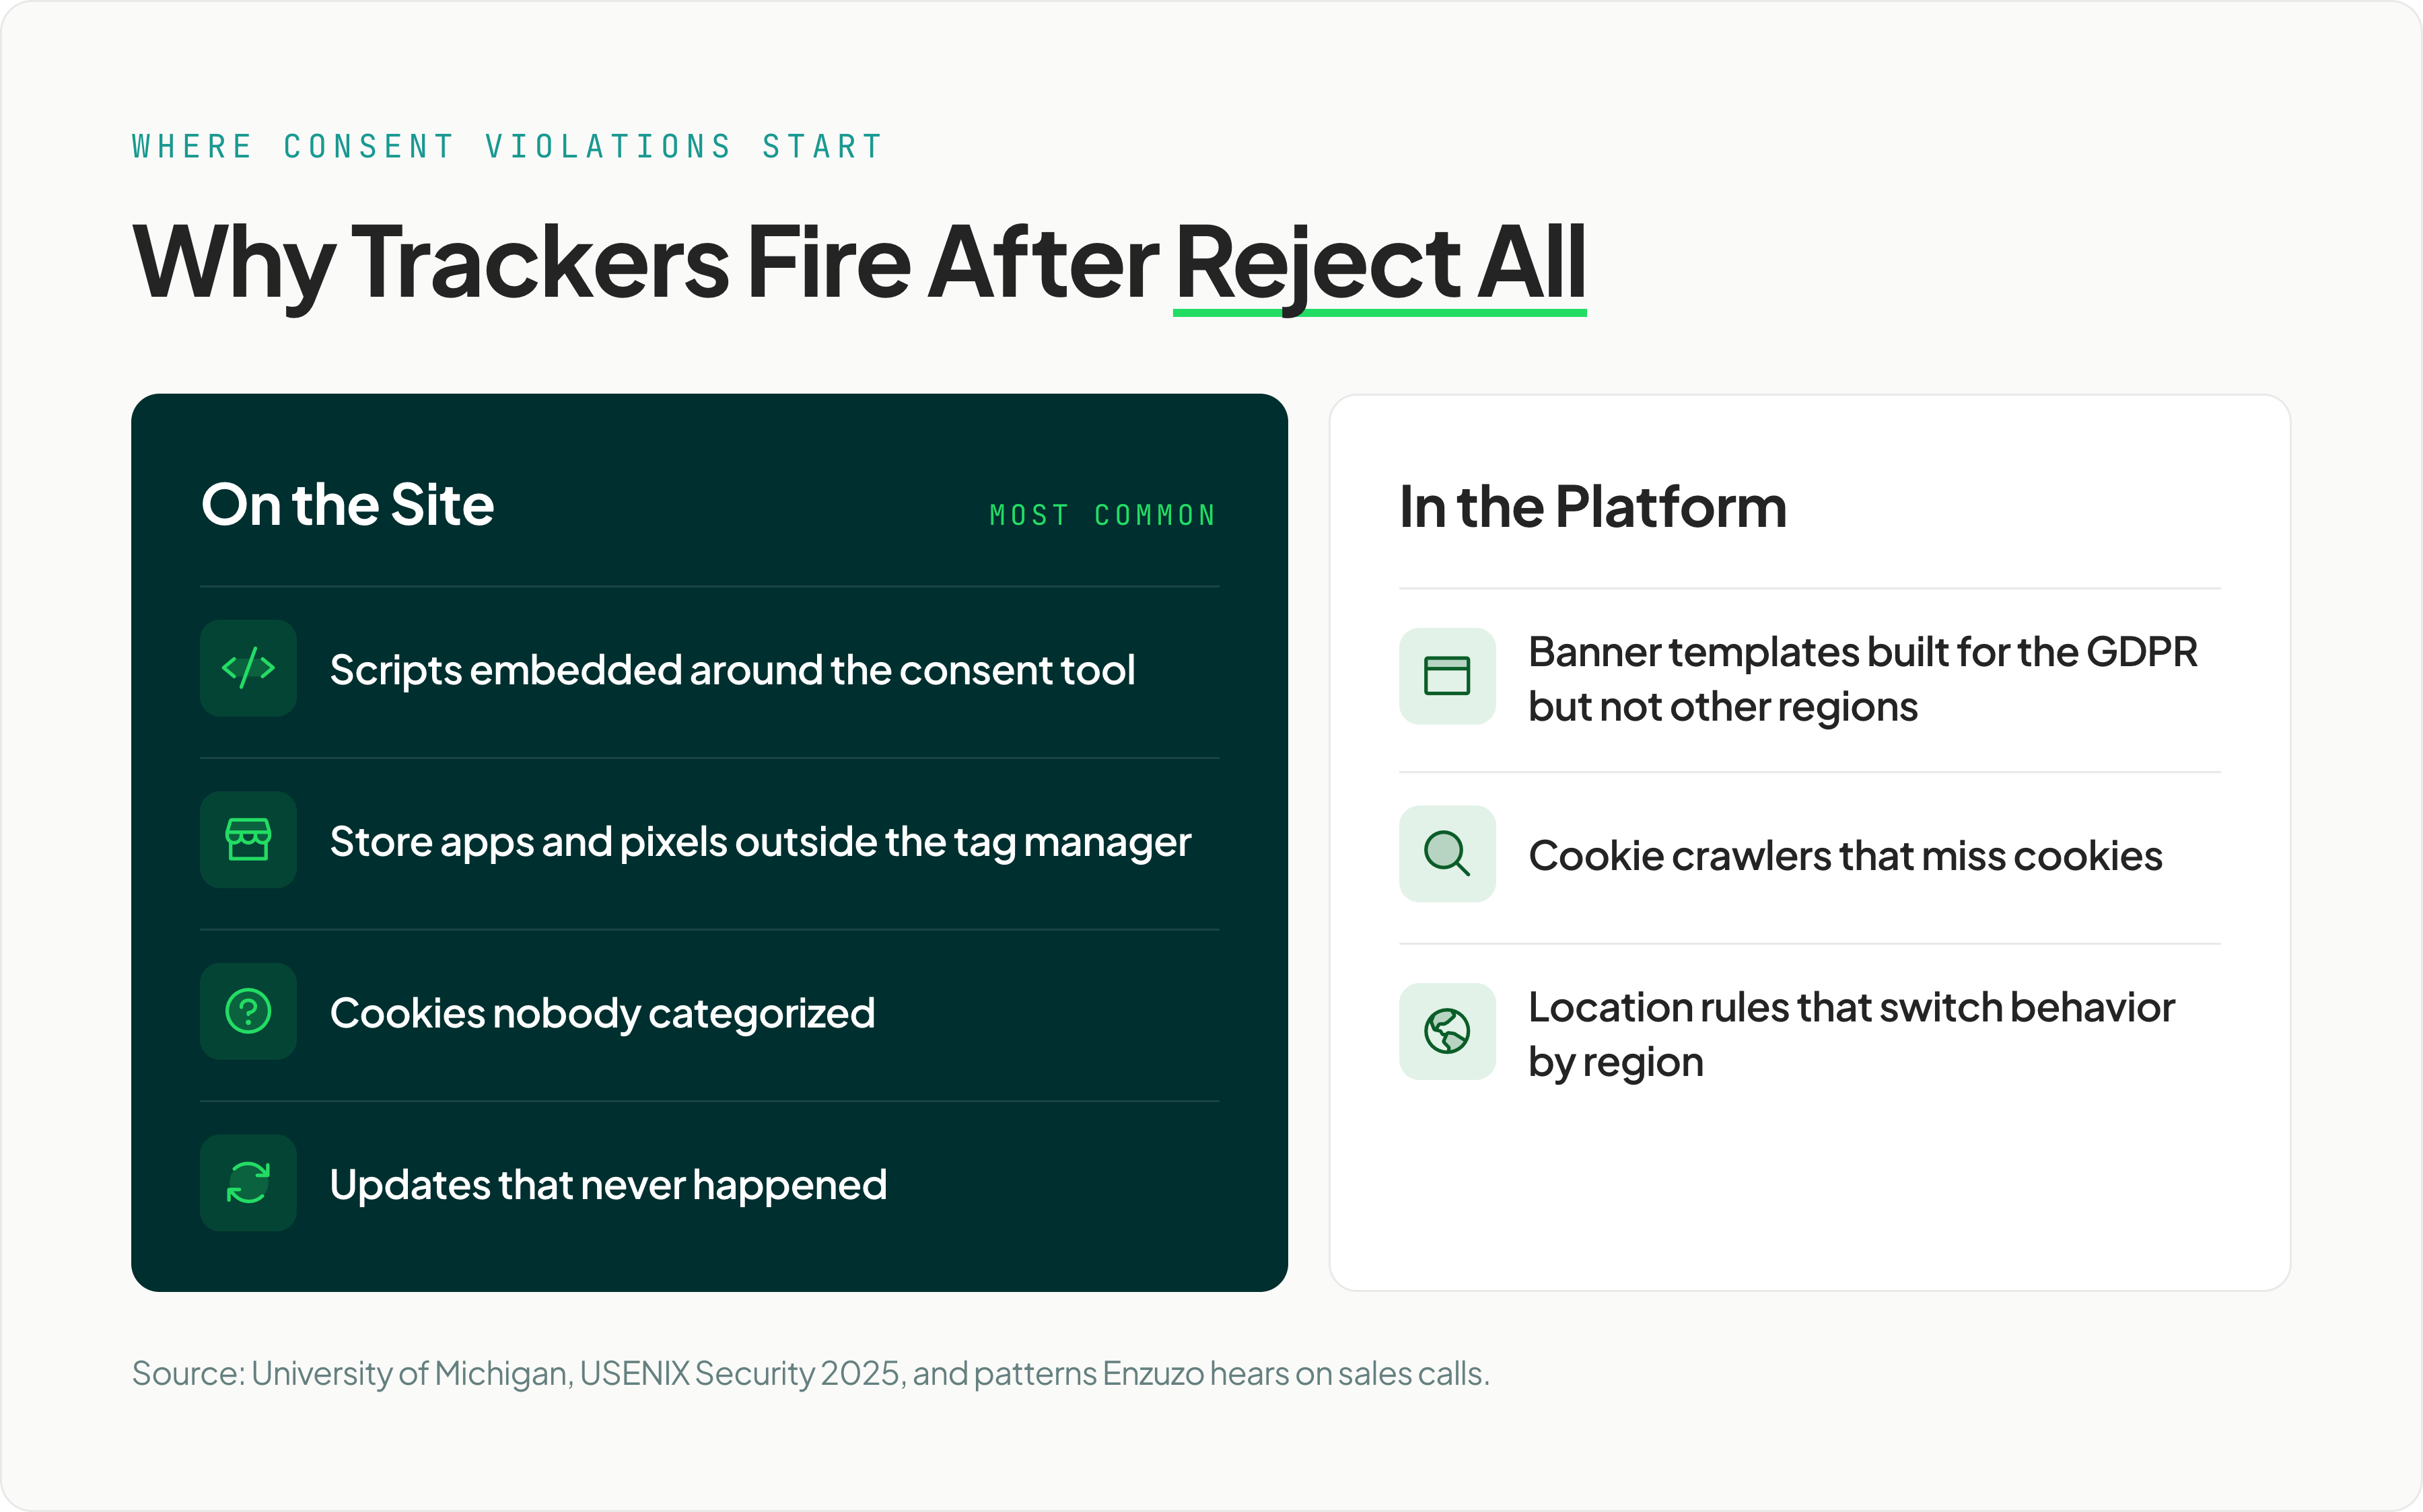
The Michigan paper traces violations to both sides of the setup. On the platform side, it points to banner templates built for the GDPR but not other regions, cookie crawlers that miss cookies, and location rules that switch behavior by region. On the site side, it points to scripts embedded around the consent tool, cookies nobody categorized, and updates that never happened.
The authors' own summary is plain: most undeclared cookies come from "website developers not categorizing cookies or CMP crawlers missing some cookies."
Enzuzo hears the same pattern with its users. A marketing pixel hard-coded into the site template, a store app that injects its own tracking, or an analytics tool nobody added to the tag manager will fire no matter what the banner says.
California's privacy regulator has said the tool doesn't carry the blame either. After fining the retailer Todd Snyder, the head of enforcement at the California Privacy Protection Agency said, "Using a consent management platform doesn't get you off the hook for compliance"
A full consent management platform does more than a basic banner, but only if it's wired into every script on the site. Learn more about cookie banners and what they should do.
What are the stages of the consent management process?
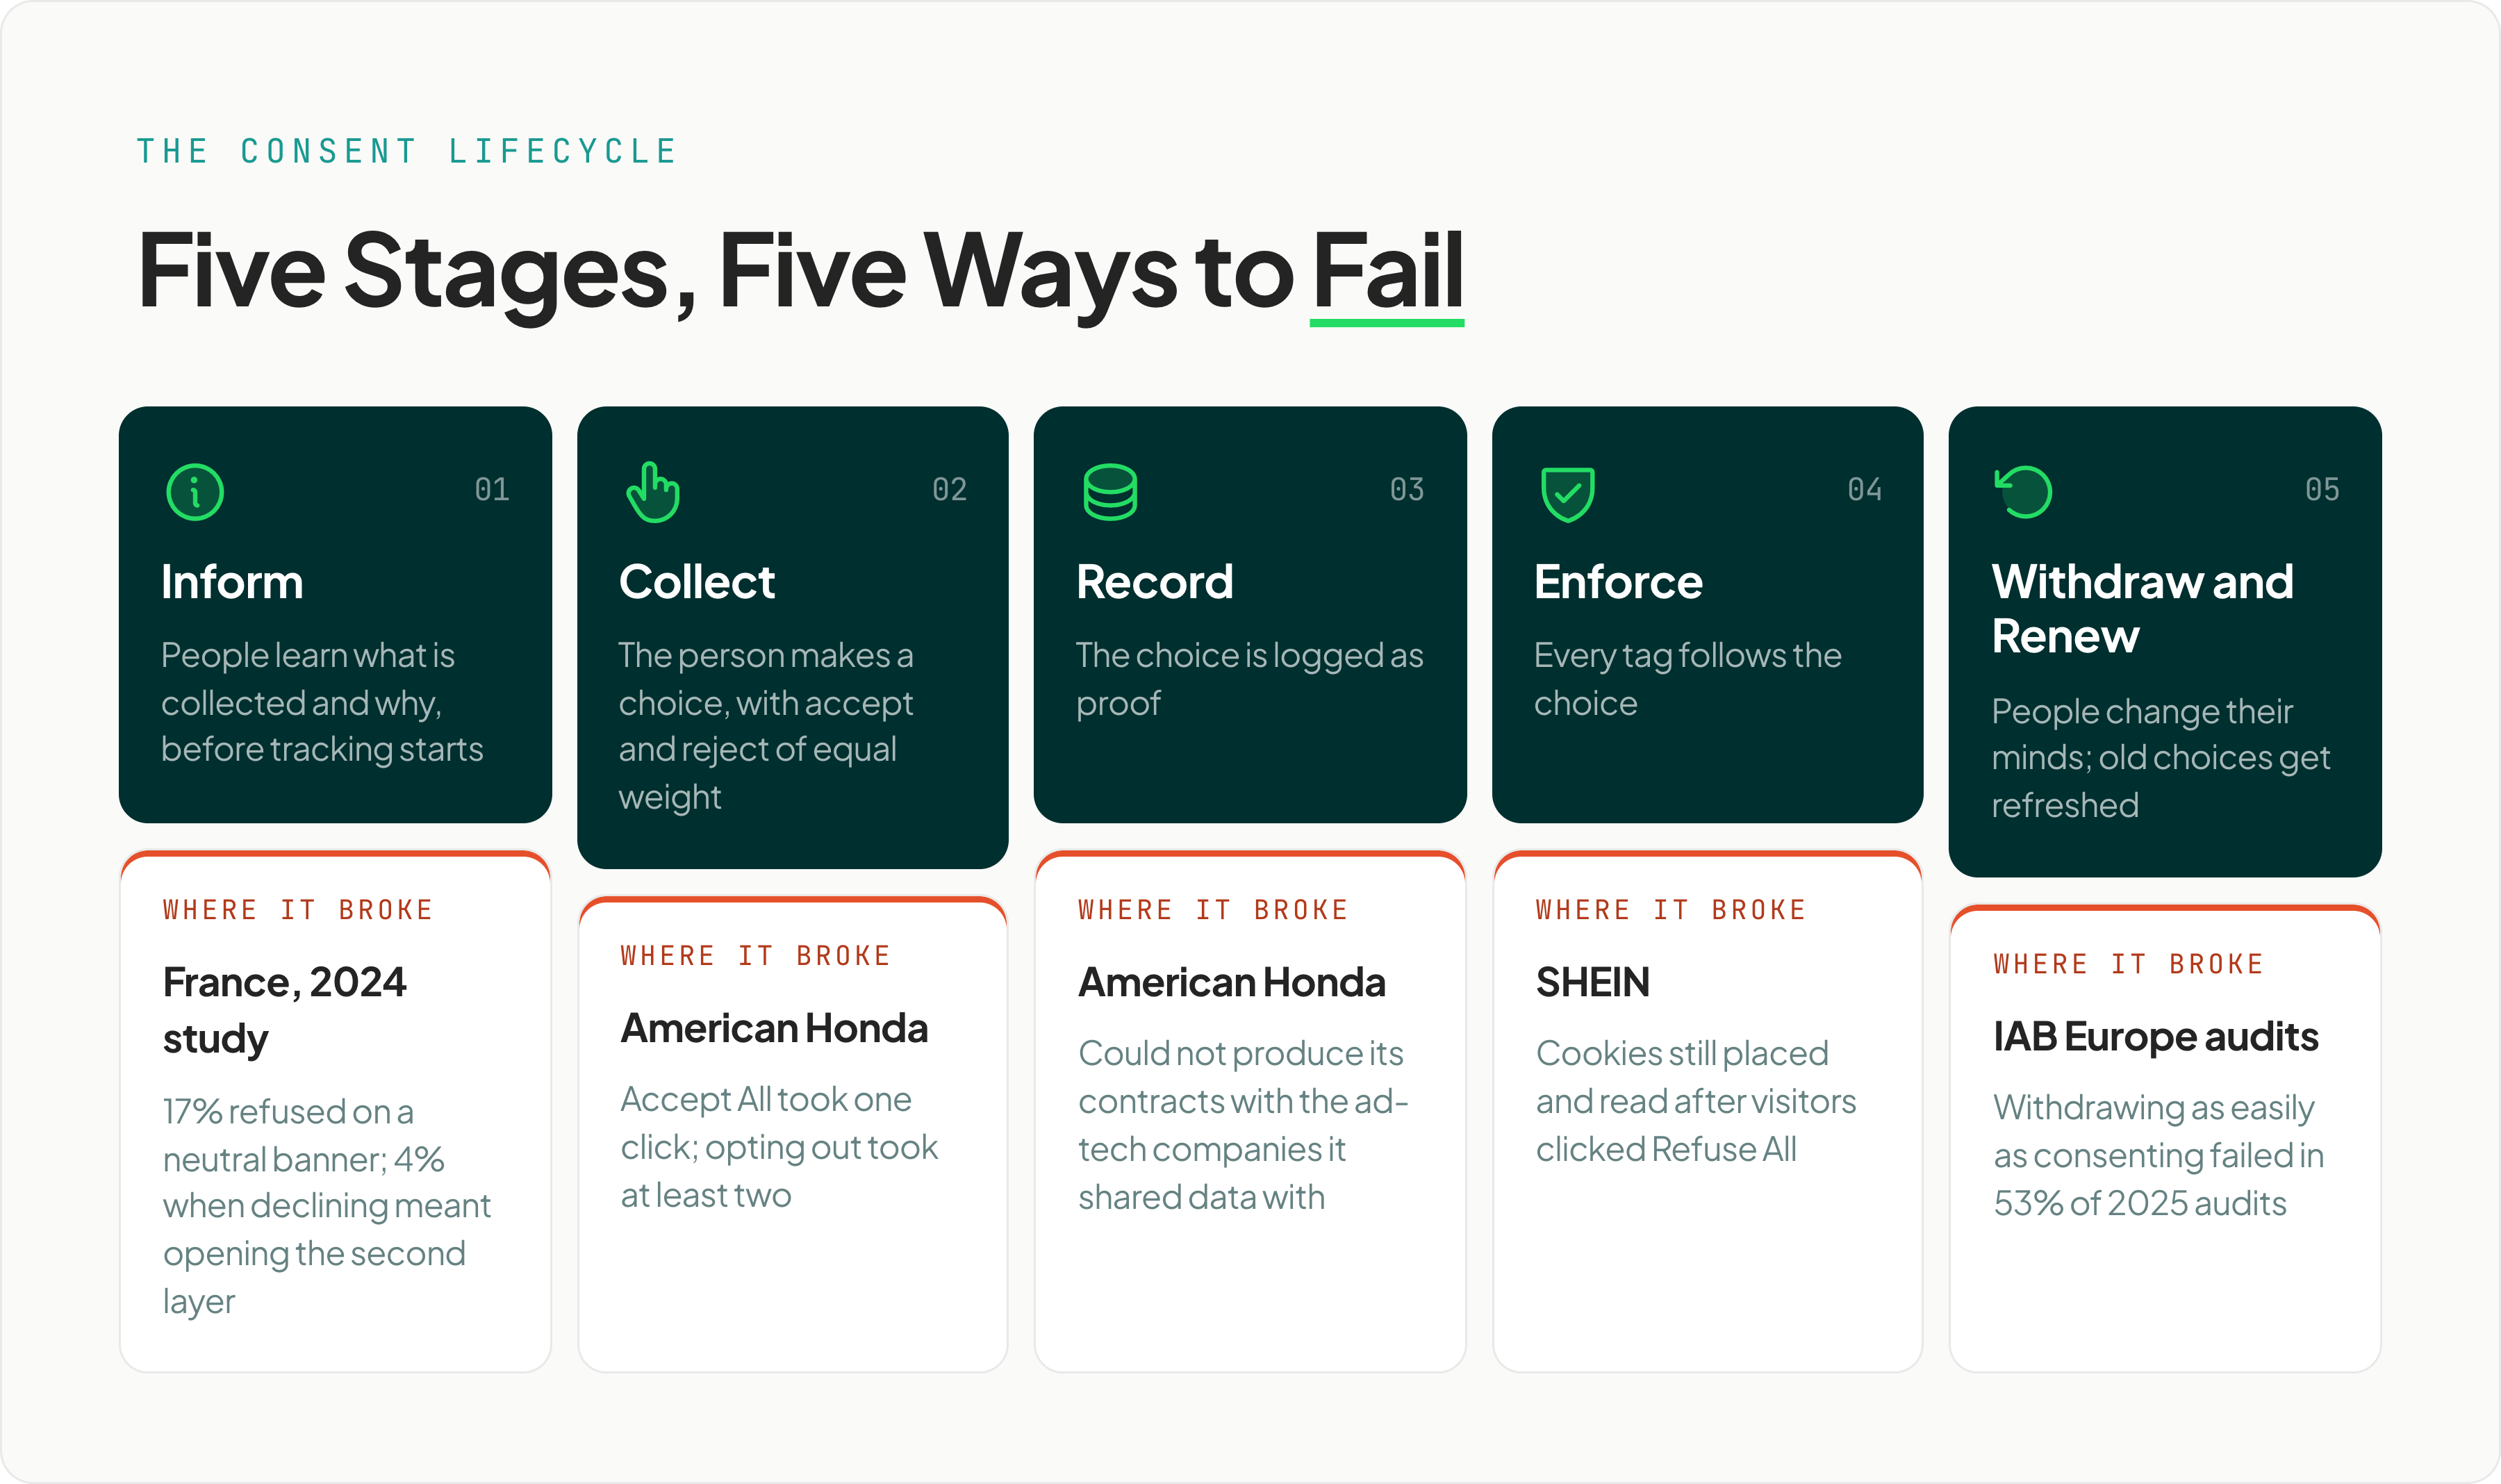
The consent management process, often called the consent lifecycle, runs in five stages: inform people, collect a valid choice, record it, enforce it across every tool, and let people withdraw or renew it.
| Stage | What happens | What the system needs | Legal hook |
|---|---|---|---|
| 1. Inform | People learn what's collected and why, before tracking starts | A clear notice and banner, backed by an accurate cookie inventory | ePrivacy Directive Art. 5(3); GDPR Art. 4(11) (informed) |
| 2. Collect | The person makes a choice | Accept and reject options of equal weight, with per-purpose choices | GDPR Art. 4(11); CCPA regulations § 7004 |
| 3. Record | The choice is logged as proof | A consent log with the time, the banner version, and each choice | GDPR Art. 7(1) |
| 4. Enforce | Every tag follows the choice | Script blocking, consent signals to ad platforms, GPC handling | ePrivacy Directive Art. 5(3); state opt-out rules |
| 5. Withdraw and renew | People change their minds, and old choices get refreshed | A lasting way to reopen choices, plus a renewal schedule | GDPR Art. 7(3) |
Stage 1, inform: what must people be told before any data is collected?
People must be told what data is collected, by whom, and why before any non-essential tracking starts.
The EU's cookie rule requires "clear and comprehensive information" about the purposes before a cookie is stored or read (ePrivacy Directive, Article 5(3)).
California spells out the list. Its regulations (§ 7012) say a notice at collection must name the categories of personal information, the purposes, whether each category is sold or shared, and how long it's kept. It must also link to the opt-out and the privacy policy, and a business that gives no notice can't collect the data at all.
Explaining this in plain language matters because most people don't know what cookies do. In a UK government experiment with 5,019 adults, only about 20% correctly identified which data cookies collect.
Banner design changes influence behaviour, too. In a 2024 experiment co-authored by a researcher at France's data protection authority, 3,947 people in France saw different banner designs. With a neutral banner, 17% refused cookies. When declining meant opening the banner's second layer, only 4% did.
Accuracy counts as much as clarity. The European Data Protection Board's cookie banner taskforce found sites labeling non-essential cookies as essential, and said the business must be able to prove a that.
Strictly necessary cookies are the main category that can run in the EU without consent.
France's CNIL also grants an analytics exemption for some audience-measurement cookies, but only under strict conditions. The cookies must produce anonymous statistics for the site itself, with no cross-site tracking and no identifiable data passed to third parties.
Stage 2, collect: what makes consent valid?
Valid consent is freely given, specific, informed, and unambiguous, and it takes a clear action, so a pre-ticked box never counts. The EU's top court confirmed this in its Planet49 ruling in 2019.
Freely given has a specific meaning. GDPR Article 7(4) tells regulators to weigh whether a service was made conditional on agreeing to data processing it doesn't need, which is why paywall-style cookie walls draw so much scrutiny.
Rejecting consent has to be as easy as accepting it. France's regulator, the CNIL, found that accepting personalized ads took 2 clicks while choosing generic ads took 6 in Google's account-creation flow before October 2023.
Its decision said that making refusal more complex than acceptance "is actually to discourage users from refusing," as part of a EUR 325 million fine across two Google companies.
California reached the same place under a different law. The CPPA found that American Honda's cookie tool let people accept all cookies in one click but made opting out take at least two. The CPPA ordered Honda to add a Reject All button matching its Allow All button.
California's CCPA regulations spell it out: a banner offering only Accept All and More Information isn't a symmetrical choice, while Accept All and Decline All would be.
California also names the opt-out itself. A business that sells or shares personal information must post a homepage link titled "Do Not Sell or Share My Personal Information" (Civil Code § 1798.135). The regulations also allow a single link titled "Your Privacy Choices" instead. Posting the link doesn't replace GPC: the regulations say the business must still process opt-out preference signals.
Unequal paths show up constantly in consent design. In a CHI 2022 review of 191 consent interfaces from five major platforms, 88.0% used at least one dark pattern, and the most common, found on 78.5%, made the less private option the easier one to pick.
The EU position is narrower than many people assume. The EDPB taskforce's majority view is that a banner with an accept button and no reject option on any layer is an infringement. It stops short of requiring the reject button on the first layer. Enzuzo's banner can show a Decline button next to Accept on the first layer, and Enzuzo recommends keeping it on for GDPR compliance.
Rules differ by country, and the banner requirements guide covers each one. For design ideas, see these cookie banner examples.
Start building your own with Enzuzo's cookie banner generator.
Stage 3, record: how does a business prove what someone chose?
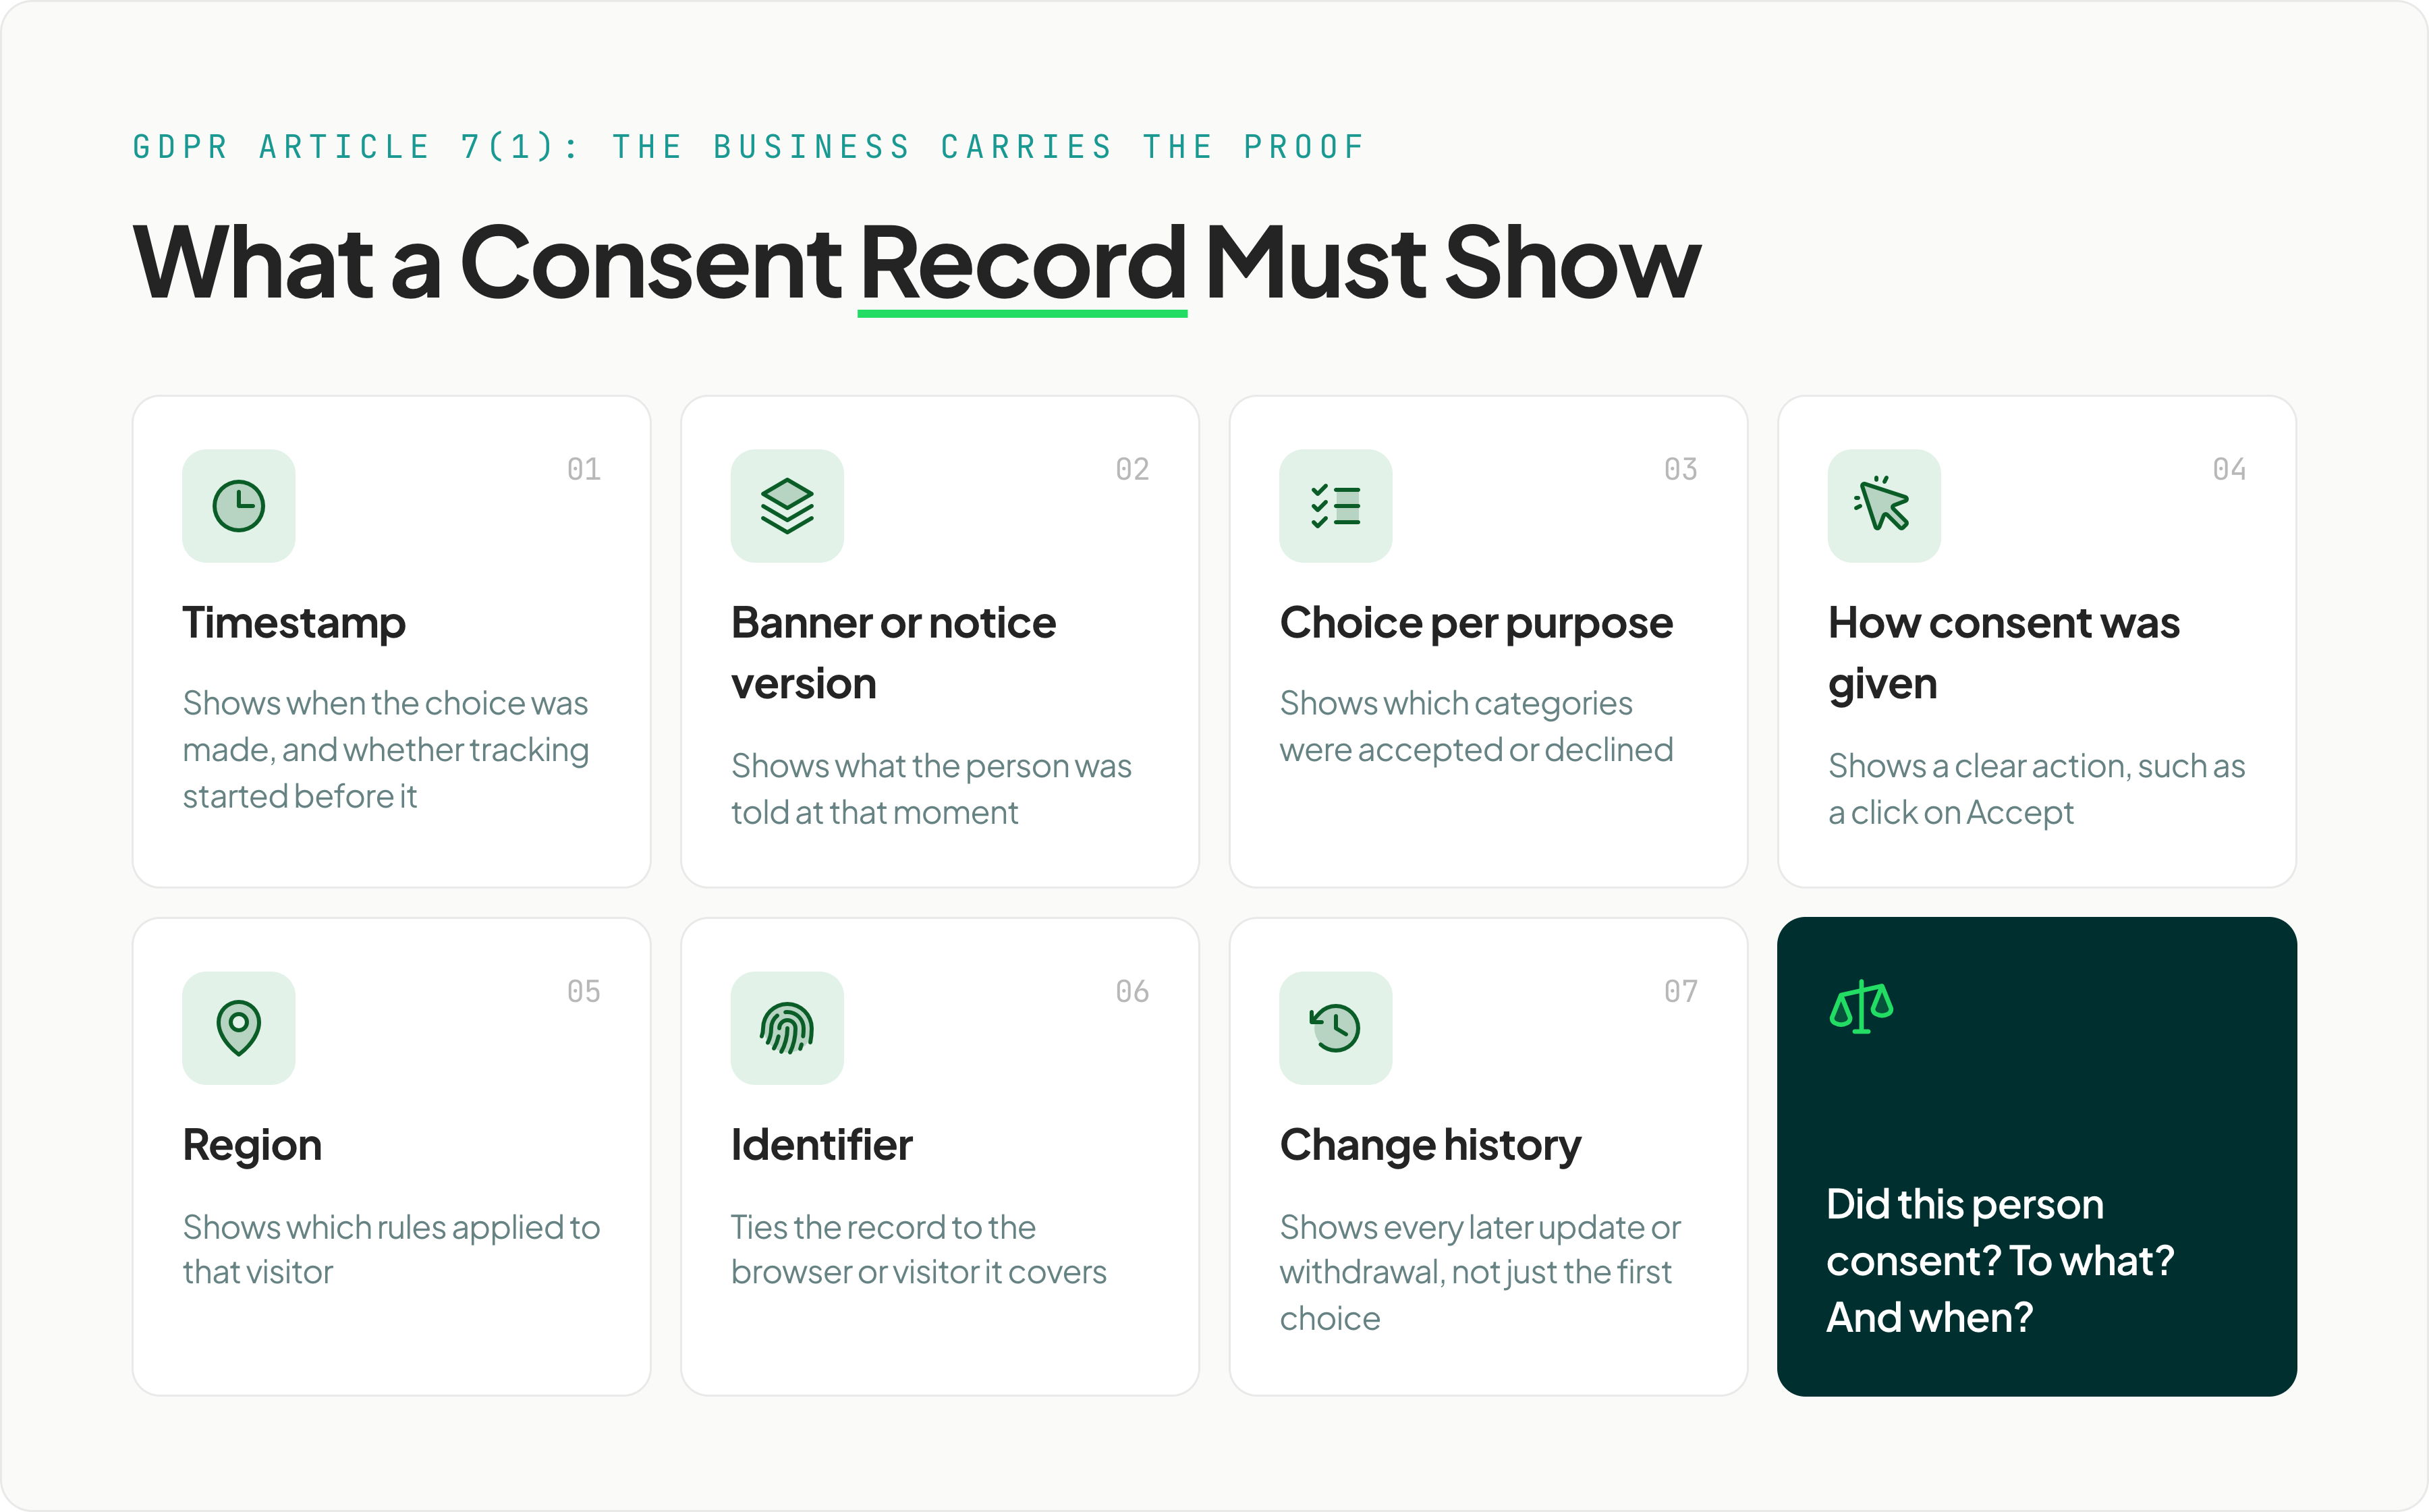
A business proves consent with a record of each choice: when it happened, what the person saw, and what they agreed to.
| Field | Why it matters |
|---|---|
| Timestamp | Shows when the choice was made, and whether tracking started before it |
| Banner or notice version | Shows what the person was told at that moment |
| Choice per purpose | Shows which categories were accepted or declined |
| How consent was given | Shows a clear action, such as a click on Accept |
| Region | Shows which rules applied to that visitor |
| Identifier | Ties the record to the browser or visitor it covers |
| Change history | Shows every later update or withdrawal, not just the first choice |
Regulators are important, but lawsuits are where businesses need hard evidence. Proving a specific visitor said yes when a demand letter claims otherwise, is the core essence of consent management.
This applies to third-party data sharing, too. The CPPA noted that Honda couldn't produce its contracts with the ad-tech companies it shared personal information with, a separate violation in the same order.
No law sets a single retention period for consent logs. A practical default is to keep each record for as long as the data it covers is in use, plus enough time to answer a complaint or claim.
Switching consent platforms raises two separate issues. The consent logs can be exported and carried over. The consent stored in each visitor's browser usually can't, because it's stored in the old platform's own cookie, so returning visitors see a banner again.
When a business moves to Enzuzo, its team handles the migration, including transferring existing consent records.
Stage 4, enforce: how do consent choices reach every tool?
Consent choices reach each tool through a signal that the tool obeys: a script that stays blocked until consent, a consent state passed to ad platforms, or a browser opt-out signal the site honours.
Enforcement is where the failures happen.
SHEIN's site placed advertising cookies the moment visitors arrived, and continued reading and placing new ones even after users clicked Refuse All. The CNIL fined SHEIN's Irish subsidiary EUR 150 million in September 2025.
Opt-outs break the same way in the US. Ford asked people to confirm their email before processing an opt-out, then kept selling or sharing data.
The CPPA fined Ford $375,703 and ordered it to audit its cookies, pixels, and web beacons for Global Privacy Control within 90 days.
Healthline Media paid $1.55 million to California's Attorney General after about 65,000 opt-outs, most of them GPC signals, went unhonored.
Consent also has to reach the systems behind the website. Tractor Supply's opt-out form didn't stop personal information flowing to advertising partners through its trackers, part of what drew a $1.35 million fine. The same goes for CRMs, email platforms, customer data platforms, and ad audiences uploaded from them: a choice made in the banner has to follow the data into every system that uses it.
Global Privacy Control is a browser setting that sends an opt-out signal to every site a person visits. Twelve states require covered businesses to honor signals like it, including California, Colorado, and Texas; the state privacy laws tracker lists all twelve.
Enzuzo's consent management platform can detect a visitor's Global Privacy Control signal and automatically opt them out of non-essential services and cookies once GPC support is turned on.
Inside Google Tag Manager, tags havebuilt-in consent checks, and other tags can be set to require a consent type before they fire. The consent tool sets those consent types when the visitor chooses.
Scripts that bypass the tag manager never get that check, which is why so many keep firing after a rejection. The tag manager setup walks through the wiring, and for Google's own ad and analytics tags, the consent state travels through Google Consent Mode.
Stage 5, withdraw and renew: how easy must it be to change your mind?
Withdrawing consent must be as easy as giving it, under GDPR Article 7(3). Withdrawal stops future processing, but it doesn't make earlier processing unlawful.
This check fails often, even among registered platforms. In IAB Europe's 2025 compliance audits of consent platforms, the check for withdrawing consent failed in 53% of audits.
A way back in has to stay available after the banner closes. The EDPB taskforce said regulators can't impose one specific tool, such as a floating icon; what matters is that withdrawal of consent takes no more effort than consenting did. Visitors can reopen Enzuzo's cookie manager at any time from a link placed anywhere on the site, such as the footer.
Withdrawal also connects consent to a person's other data rights. Under GDPR Article 17(1)(b), someone who withdraws consent can ask for their data to be erased when no other legal ground covers it. Article 15 lets anyone ask what data a business holds about them and get a copy. The Data Subject Access Requests guide covers this in detail.
Collecting data for a new purpose needs renewed consent. The EDPB's consent guidelines say a controller must get "a new and specific consent" if its purposes change after consent was given or it adds a purpose (paragraph 90). In practice, a new use of the data means a new banner version and a fresh ask.
Stored data choices also need to be refreshed periodically. Ireland's Data Protection Commission treats six months as the outer limit before asking again (DPC guidance). France's CNIL recommends keeping a visitor's choice for six months.
What is cookie consent management?
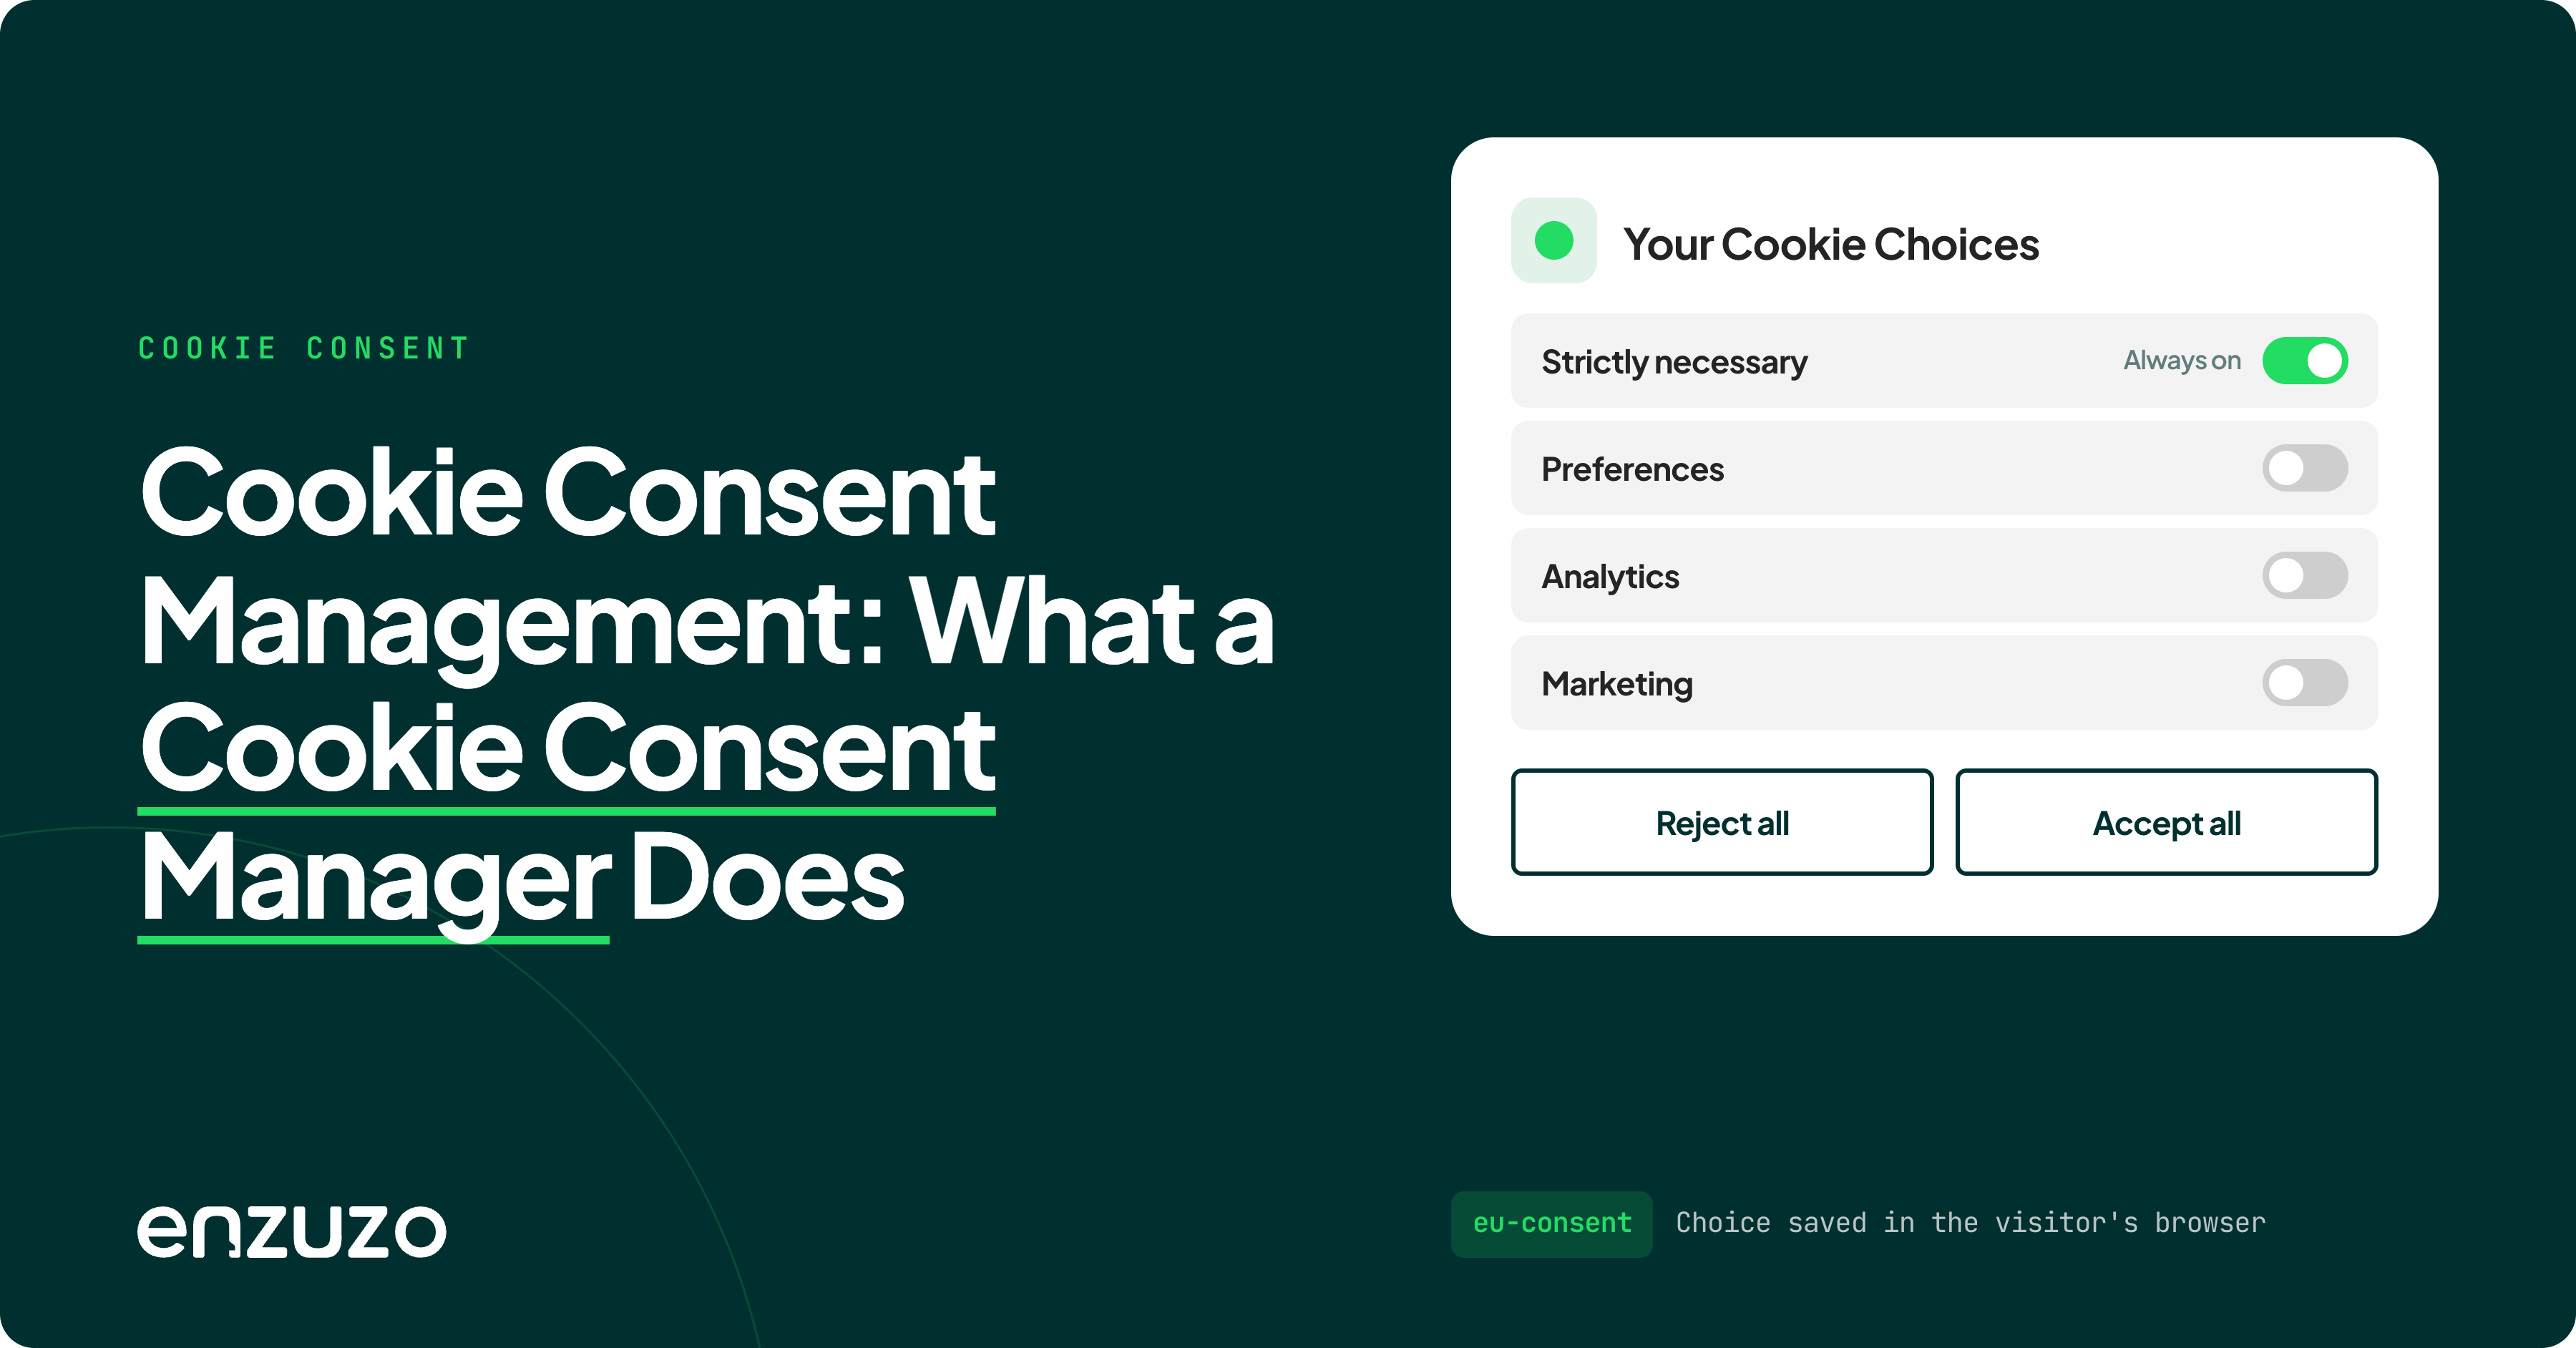
Cookie consent management is the website slice of consent management: the banner, the per-category cookie choices, and the blocking that keeps non-essential cookies off until a visitor agrees. It applies all five stages to one channel, the browser. The cookie consent management guide goes deeper on that channel.
What happens when a business gets consent wrong?
A business that gets consent wrong faces regulator fines in Europe and California and private lawsuits under US wiretap laws.
Consent management fines
Regulators have fined companies for unequal accept and reject paths in their cookie banner, tracking that ignored a refusal, and opt-outs that never took effect. The seven cases in the table below are the most recent ones.
Enzuzo's roundup of cookie banner fines covers more cases.
| Company | Regulator | Date | Penalty | What went wrong | Stage that failed |
|---|---|---|---|---|---|
| CNIL (France) | Sep 2025 | EUR 325 million, across two Google companies | Ad cookies placed at account creation without valid consent; refusing personalized ads took 6 clicks vs 2 to accept (flow before Oct 2023); Gmail ads shown without consent | Collect | |
| SHEIN | CNIL (France) | Sep 2025 | EUR 150 million | Ad cookies placed before any banner click; cookies still placed and read after Refuse All | Enforce |
| American Honda | CPPA (California) | Mar 2025 | $632,500 | Accept All took one click, opting out took at least two; no contracts with ad-tech partners | Collect, record |
| Todd Snyder | CPPA (California) | May 2025 | $345,178 | For 40 days the banner appeared and vanished; GPC signals not processed; opt-outs required a photo holding ID | Enforce |
| Healthline Media | California Attorney General | Jul 2025 | $1.55 million | About 65,000 opt-outs, mostly GPC, not honored; article titles suggesting health conditions shared for ad targeting | Enforce |
| Tractor Supply | CPPA (California) | Sep 2025 | $1.35 million | Opt-out form didn't stop sharing through trackers; GPC not honored until July 2024 | Enforce |
| Ford | CPPA (California) | Feb 2026 | $375,703 | Email confirmation required before an opt-out; data sold or shared after opt-out | Collect, enforce |
The CNIL issued both of its fines under French laws that implement the EU's ePrivacy rules, not under the GDPR. The GDPR's own ceiling for breaking its consent conditions is EUR 20 million or 4% of worldwide annual turnover, whichever is higher (Article 83(5)).
GDPR fines keep climbing too. They passed EUR 6 billion for the first time in 2026: about EUR 6.11 billion as of March 1, across 2,685 fully documented fines, according to the CMS Enforcement Tracker.
In California, CCPA administrative fines run up to $2,663 per violation and $7,988 per intentional violation or violation involving a consumer known to be under 16.
How do tracking lawsuits and demand letters start?
Tracking lawsuits in the US usually start with a claim that a site's pixels or scripts recorded visitors without consent. Many rely on wiretap laws such as the California Invasion of Privacy Act (CIPA), which allows $5,000 per violation.
The volume has grown fast. The sponsor of California's SB 690 told an Assembly committee that CIPA lawsuits grew from about 600 to about 4,000 in 18 months.
SB 690 would end private lawsuits under CIPA's pen register provision for website and app tracking. It passed the Legislature on August 28, 2026, and went to the Governor, who has until September 30 to act (bill status).
The SB 690 guide covers what it changes and what it leaves standing, and this demand letter example shows what the letters look like. Meta Pixel lawsuits are the most common wiretap lawsuit, and Florida's wiretap law produces similar letters.
Consent management and marketing attribution
Consent management affects attribution because every visitor who declines drops out of cookie-based tracking and measurement. How big that gap gets depends on banner design, region, and whether consent signals reach the ad platforms.
How many visitors accept tracking?
Most people accept tracking when a banner is neutral, and a site's consent rate, the share of visitors who accept, moves with the design.
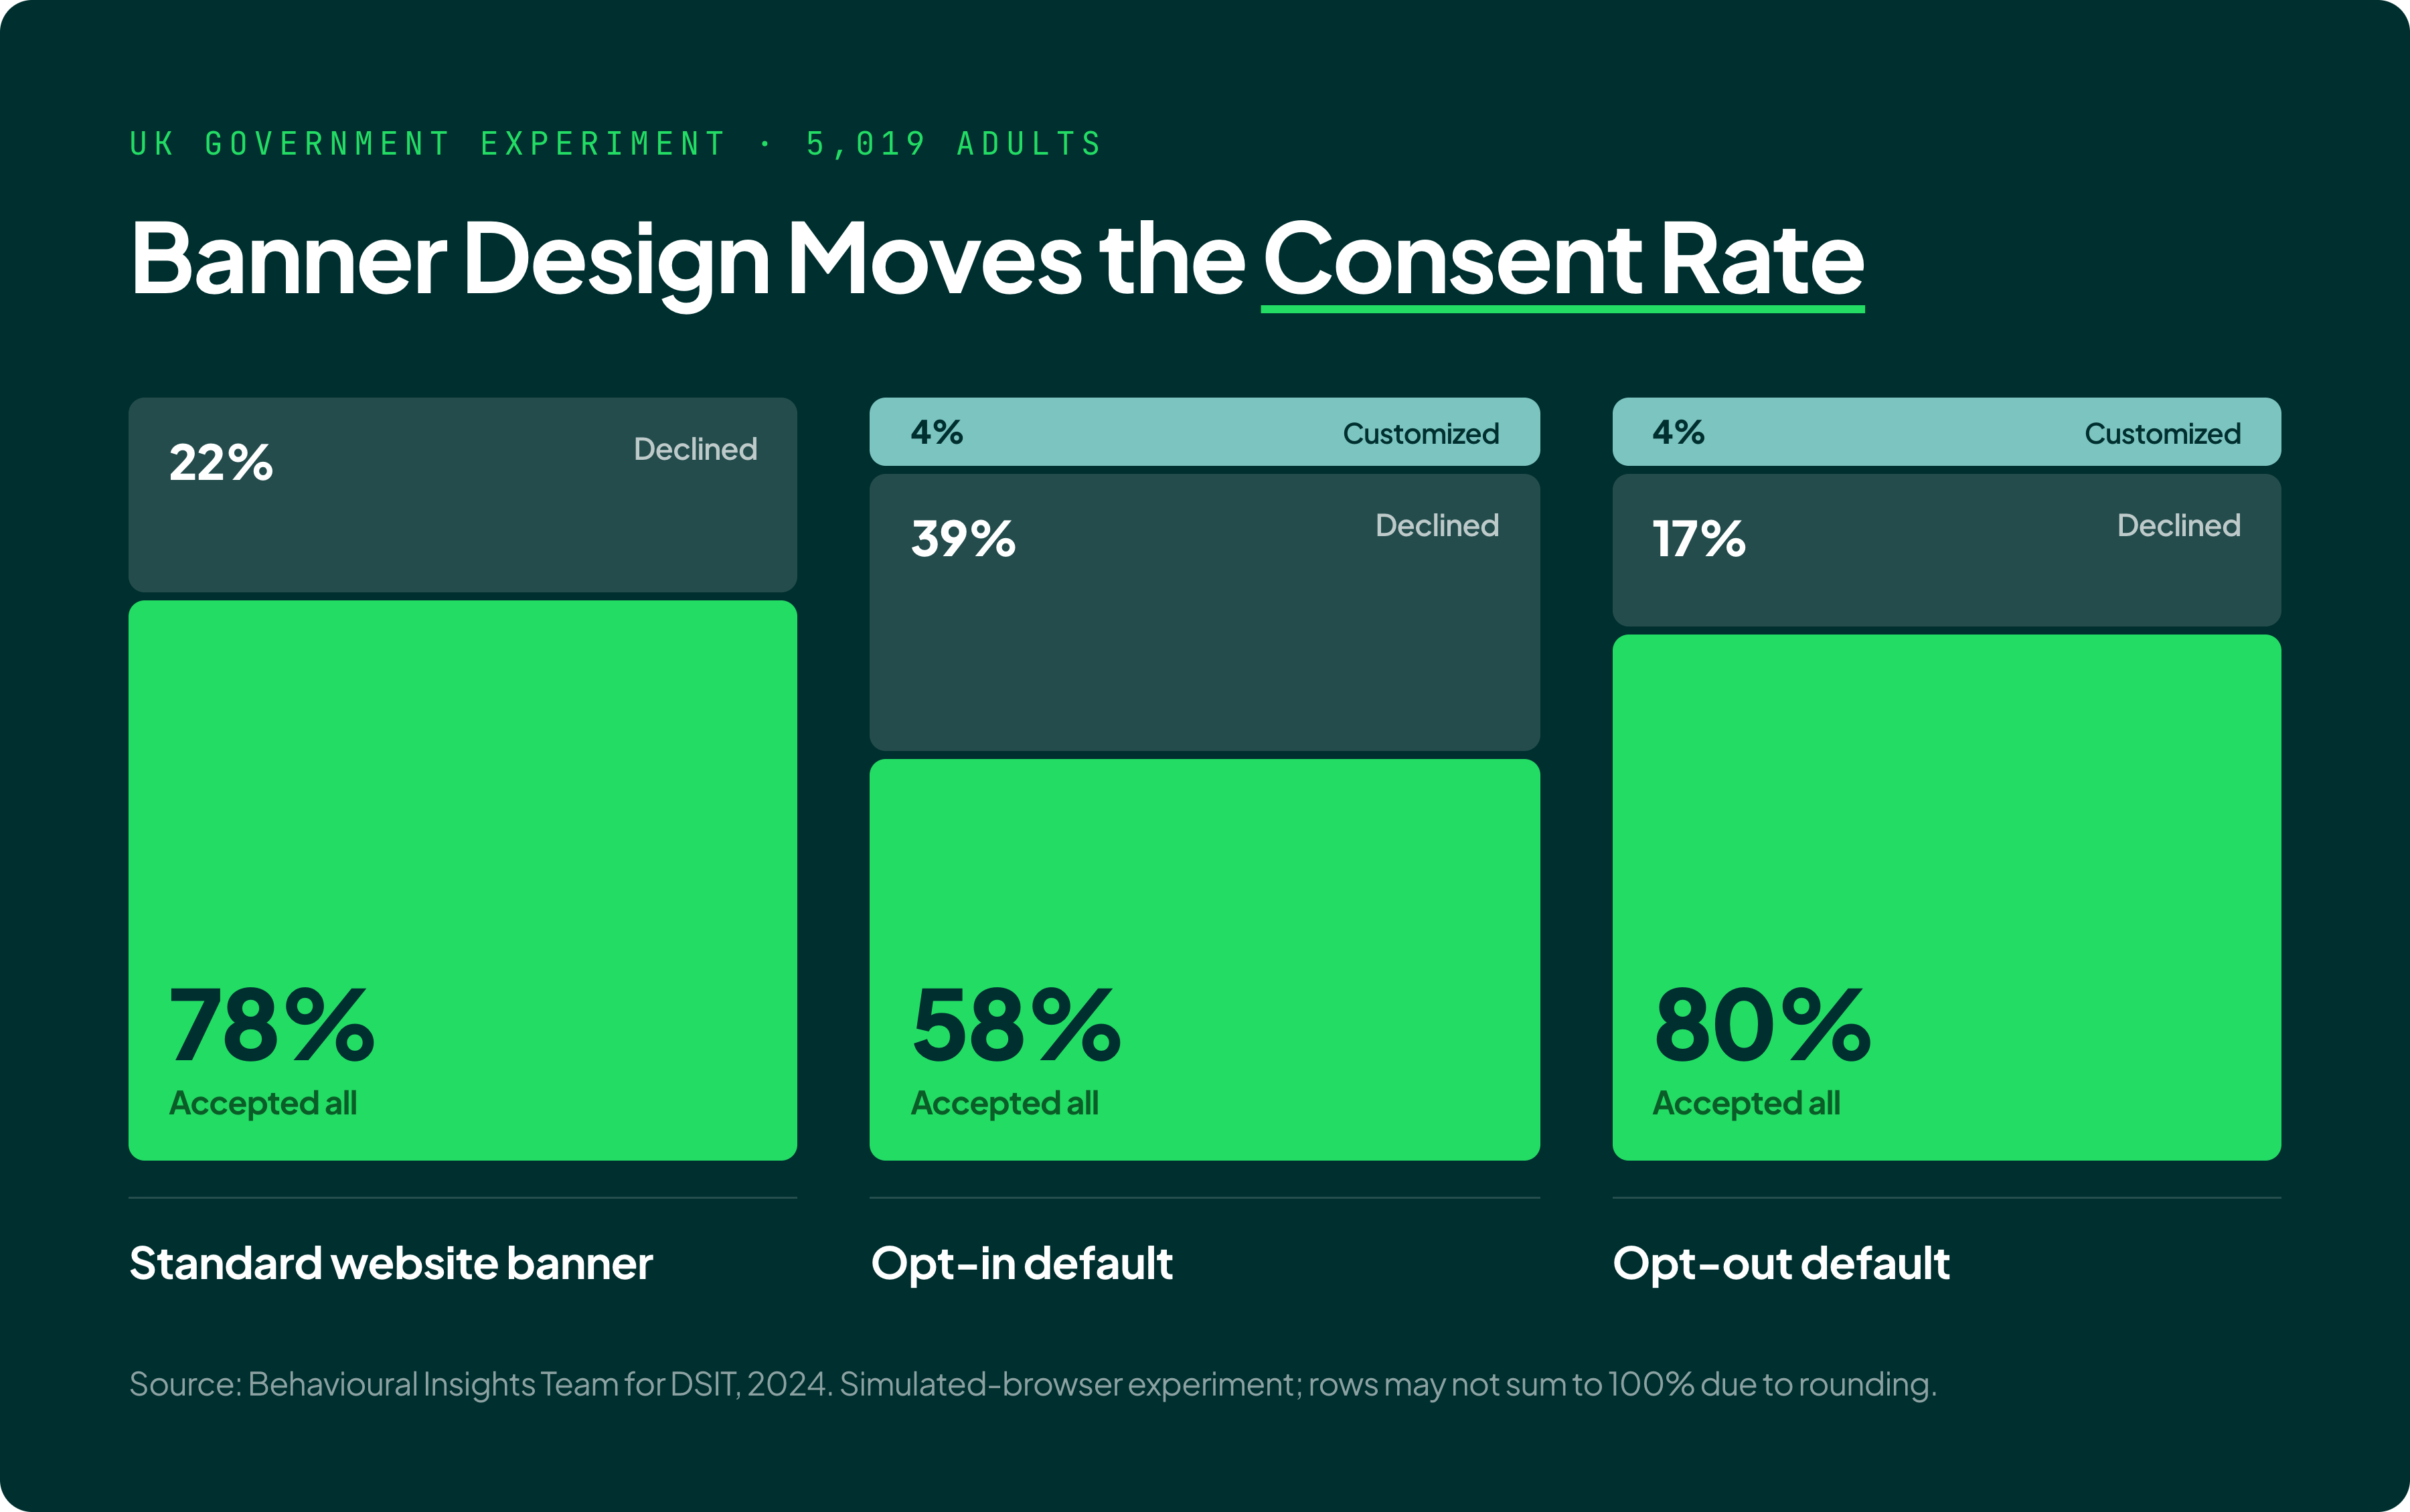
In the UK government experiment, 78% of participants accepted all cookies on a standard website banner, and 22% declined. With an opt-in default, 58% accepted, 39% declined, and 4% customized. An opt-out default produced 80% acceptance.
People decide fast. Participants spent about 3 seconds on the neutral banner, compared with 15 to 20 seconds on the browser-level designs, and 44% of those who accepted said they did it out of habit. An earlier US study found only 45.3% of participants ended up with the choice they said they wanted.
For a marketing team, that range is the budget. On 10,000 visits, the neutral banner in that experiment would leave about 2,200 visits outside cookie-based measurement; the opt-in default would leave about 4,200.
What happens to attribution when someone declines?
When users decline, analytics and ad cookies don't load, so that visitor's conversions go unattributed, remarketing audiences shrink, and analytics reports show gaps.
The effect gets large when opt-in becomes the default. When Apple made app tracking opt-in, trackable US traffic on Apple devices fell from 73% to 18%, and trackable users drew about 51% higher ad prices, according to FTC PrivacyCon research. That study covers iOS apps rather than websites, but it shows how fast an opt-in default reshapes the audience that can be measured.
How does Google Consent Mode fit into consent management?
Consent Mode is a signal, not a consent platform. It carries the visitor's choice to Google, but it doesn't collect that choice or block other vendors' scripts.
Google Consent Mode acts as a trusted intermediary from the consent platform to Google's tags, which influence ad bidding and adsense revenue in Europe. When users decline cookies, Google Consent Mode records that choice but uses modeling to serve ads and estimate conversion metrics instead.
Since March 2024,Google has required advertisers to send consent signals for users in the European Economic Area to keep ad personalization and audience features. Microsoft followed: since May 5, 2025, Microsoft Advertising has required UET consent mode or an IAB consent signal for traffic from the EEA, the UK, and Switzerland.
Google Consent Mode has a basic and an advanced setting, and the difference explains why some Google requests still appear after a visitor declines.
In basic mode, Google's tags don't fire at all without consent. In advanced mode, they keep sending measurements without cookies, which Google uses to model conversions.
Enzuzo is a Google-certified CMP Gold Partner for Google Consent Mode v2, supporting Microsoft UET Consent Mode too. The Consent Mode setup guide covers implementation, and the Microsoft consent mode roundup covers Bing.
Consent management laws
Consent management is required, in different forms, by the GDPR and ePrivacy rules in Europe, the CCPA and 19 other US state privacy laws in effect, wiretap laws such as CIPA, and Canada's privacy laws.
| Law | Where | Consent model | Key consent rule |
|---|---|---|---|
| GDPR and ePrivacy Directive | EU and EEA | Opt-in | Non-essential cookies need consent first; consent must be freely given, specific, informed, and unambiguous |
| UK GDPR and PECR | United Kingdom | Opt-in | Same opt-in model for non-essential cookies |
| CCPA and CPRA | California | Opt-out of sale and sharing | Do Not Sell or Share link (or a single alternative opt-out link); honor Global Privacy Control even when the link is posted; accept and decline choices must be symmetrical |
| Other state privacy laws | 19 more states in effect; Oklahoma and Alabama from 2027 | Opt-out of sale and targeted ads; opt-in for sensitive data in most states | 12 states require honoring universal opt-out signals; Iowa and Utah don't require opt-in for sensitive data |
| CIPA and other state wiretap laws | California and several other states | Consent as the defense | $5,000 per violation under CIPA |
| PIPEDA | Canada | Meaningful consent | Bill C-36, its proposed successor, is at second reading |
| Quebec Law 25 | Quebec | Opt-in, privacy by default | Consent asked separately from other terms; express consent for sensitive information; tools that identify, locate, or profile off by default |
| LGPD | Brazil | Consent is one of ten legal bases | Consent given in writing or another way that shows the person's will, with the burden of proof on the business; specific, highlighted consent for sensitive data, with limited exceptions |
| COPPA | United States | Verifiable parental consent | Since April 22, 2026, separate parental consent before sharing a child's data with third parties |
State-by-state details, including the twelve GPC states, are in the U.S. privacy laws tracker. Canada's rules are covered in the PIPEDA guide and the Law 25 guide.
Consent rules keep spreading. According to UNCTAD, 155 of 195 countries (79%) had data protection laws as of February 2026.
Is consent always required to process personal data?
Consent isn't always required: the GDPR lists six legal bases for processing personal data, and consent is only one of them. The table below shows the other five exceptions.
| Legal basis | When it applies | Consent needed? |
|---|---|---|
| Consent | The person agrees to a specific purpose, such as marketing cookies or email marketing | Yes, and it must be recorded |
| Contract | Processing is needed to deliver what the person signed up for, such as shipping an order | No |
| Legal obligation | A law requires it, such as tax record-keeping | No |
| Vital interests | Processing protects someone's life | No |
| Public task | A public authority carries out an official function | No |
| Legitimate interests | The business has a legitimate interest that the person's rights don't override | No, but it needs a documented balancing test, and it can't justify cookies |
Legitimate interest is the basis most often stretched. The EDPB taskforce said "the legal basis for the placement/reading of cookies pursuant to Article 5 (3) cannot be the legitimate interests of the controller." Yet in the Web Conference study, 72.8% of the sites that passed its consent-signal check still claimed legitimate interest for at least one purpose.
Opt-in vs opt-out consent
Opt-in consent means no non-essential tracking runs until the person agrees, while opt-out consent lets collection start by default and stop when the person objects. The GDPR uses opt-in. California's CCPA uses opt-out for the sale and sharing of personal information, and most other US state laws add opt-in for sensitive data.
Explicit consent is an unmistakable statement, such as ticking an unticked box. Implied consent is inferred from behavior, and it rarely meets the GDPR standard. Granular consent lets people choose purpose by purpose. The full list of consent types covers the rest.
Consent management vs preference management
Consent management decides whether a business can use someone's data at all, while preference management decides how it uses that data afterward, such as which emails a person gets and how often.
The two meet in the preference center, where people change cookie choices and communication settings, and where they can withdraw consent.
Many businesses assume a newsletter opt-in covers cookies, too. It doesn't: a form consent and a cookie consent are separate choices.
Preferences people share on purpose, such as topics or product interests, count as zero-party data. Dedicated preference management tools handle the communication side.
What does consent management cover beyond cookie banners?
Consent management covers every channel where a business needs permission to collect or use personal data, including email, marketing calls and texts, health data, children's data, and mobile apps, not only website cookies.
| Channel | Consent rule | Main law |
|---|---|---|
| Website cookies and trackers | Consent before non-essential tracking in the EU; opt-out of sale and sharing in US states; consent as the defense to wiretap claims | ePrivacy Directive, CCPA, CIPA |
| Marketing email in the EU and UK | Consent, or a soft opt-in for a business's own similar products when the contact details came from a sale or negotiations for one, with an opt-out offered at collection and in every message | ePrivacy Directive Art. 13(2); UK PECR reg. 22 |
| Marketing email in Canada | Express consent, or implied consent for 2 years after a purchase or 6 months after an inquiry | CASL |
| Autodialed or prerecorded marketing calls and texts | Prior express written consent | TCPA |
| Consumer health data in Washington | Consent to collect for a specified purpose, a separate consent to share, and a separate authorization to sell | My Health My Data Act |
| Children's data in the US | Verifiable parental consent, plus separate consent before disclosure to third parties | COPPA |
| Mobile apps | Operating-system permission prompts, such as Apple's App Tracking Transparency; in the EU, third-party SDKs that store or read data on the device fall under the same consent rule as cookies | Platform rules; ePrivacy Directive, per EDPB guidelines |
Rules for calls and texts shifted recently. The FCC's one-to-one consent rule was vacated by a federal appeals court in January 2025 and repealed in July 2025. Washington's health-data law is covered in the MHMDA guide.
What are consent management best practices?
Consent management best practices come down to testing each collection, storage, and audit stage the way a regulator or a plaintiff's lawyer would:
Each test takes a few minutes in a normal browser:
- Open the site in a fresh private window and watch the network tab before clicking anything. Cookies or tracking requests at this point are the SHEIN failure. Look for scripts outside the tag manager too, since hard-coded pixels and store-app pixels are common culprits.
- Count the clicks to accept and to reject. Unequal paths were the Google and Honda findings, and Tractor Supply was ordered to make both buttons similar in size and design.
- Reject, reload, and watch the network tab again. Trackers that still fire are the failure the Michigan study measured on most sites.
- Turn on Global Privacy Control in the browser and confirm the site treats the visit as opted out. Ford, Healthline, and Tractor Supply all fell short here.
- Withdraw consent through the preference link and confirm the tags stop. SHEIN kept reading cookies after a refusal, and IAB Europe found withdrawal problems in 53% of its audits.
- Pull the consent record for the test visit. It should show the time, the banner version, and each choice, which is what GDPR Article 7(1) expects a business to produce.
- Re-scan cookies after any site or tag change. The Michigan study found most undeclared cookies came from cookies nobody categorized or crawlers missed. Enzuzo's built-in Scan My Domain feature finds the scripts on a domain so they can be sorted into functional, analytics, marketing, and preferences categories.
Want it set up for you? Book a call
Consent management setup
Setting up consent management follows the five stages in order, starting with an inventory of what the site actually runs:
- Inventory every cookie and script on the site, including pixels outside the tag manager, so the notice can describe them accurately (stage 1).
- Decide the rules by region: opt-in where the law requires it, opt-out and GPC handling in US states that require them (stages 2 and 4).
- Configure the banner with accept and reject options of equal weight and a choice per purpose (stage 2).
- Connect enforcement: block non-essential scripts until consent, add consent checks in the tag manager, pass consent to ad platforms, and carry opt-outs into back-end systems such as the CRM (stage 4).
- Turn on consent logging, add a lasting link to reopen choices, and set a schedule to renew consent and re-scan the site (stages 3 and 5).
Our guide to cookie consent management covers the setup in detail.
Honda's banner is the clearest example of consent management gone wrong, and its fix shows what regulators want. The CPPA ordered a Reject All button to match the Allow All button, a user-experience designer's review of how people submit requests, and GPC applied to consumers Honda already knows.
The remedies in the other cases spell out what regulators expect:
- Tractor Supply was ordered to make its reject button similar in size and design to its accept button, and to apply GPC to known consumers as well.
- Ford was ordered to audit its cookies, pixels, and web beacons for GPC within 90 days.
- Google changed its account-creation flow in October 2023 so that refusing personalized ads took the same effort as accepting them.
- Todd Snyder's banner, which appeared and instantly vanished for 40 days, shows why a consent tool needs checking after launch.
A well-built consent flow looks like the reverse of those cases. Accept and reject appear side by side with equal weight, choices are offered per purpose, nothing non-essential loads before a click, and a link to reopen settings stays in the footer. For visual inspiration, these cookie banner examples show real designs.
Where does a consent management platform fit in?
A consent management platform (CMP) automates the consent lifecycle process: it shows the banner, stores each choice, blocks or signals tags, and gives people a way back to their settings.
Enzuzo's consent management platform can hold non-essential scripts until a visitor consents, set banners to opt-in, opt-out, or hidden by region, and pass choices to Google as a Gold Partner for Consent Mode v2. The CMP explainer covers how platforms work, read the best CMPs guide to compare your options, and CMP pricing for the details.
What does a cookieless web mean for consent management?
A cookieless web wouldn't remove the need for consent, because EU rules cover tracking pixels, scripts that make the browser send data, IP-based tracking, and hashed identifiers, not just cookies.
Third-party cookies haven't gone away in Chrome, either. In April 2025, Google dropped its plan for a standalone cookie prompt and left the choice in Chrome's settings. In October 2025, it retired most of its Privacy Sandbox technologies, citing low adoption.
Routing tracking through a site's own server doesn't escape the rule. The EDPB guidelines apply whenever the browser is told to send data, so consent is still needed unless an exemption applies. The data that holds up in a cookieless web is first-party data people chose to share.
The shortcuts that claw back lost data, such as firing tags before consent or ignoring a rejection, are exactly what draws a lawsuit or a heavy fine.
Frequently asked questions
What are the key components of a consent management system?
A consent management system is part software and part process. The software side is the banner, the consent log, the cookie scanner, and the connections that pass each choice to tags and back-end tools. The process side is the cookie inventory, the rules for each region, and a named owner who reviews changes. The connections are the part most often missing.
How can organizations ensure ongoing compliance with consent management?
Organizations keep consent management compliant by re-testing it on a schedule rather than setting it once. That means re-scanning cookies after site or tag changes and re-running the reject and GPC tests. It also means refreshing stored choices (Ireland's regulator treats six months as the outer limit), keeping records current, and updating the banner when data practices change.
What is consent driven commerce?
Consent-driven commerce is a model where a business builds its marketing on data people chose to share, through opt-ins, preference centers, and a clear value exchange, instead of passive tracking. It matters more as browsers and laws restrict third-party tracking, because consented first-party data is the part of an audience a business can keep measuring.
What is consent governance?
Consent governance is the set of owners, policies, and reviews that keeps consent management consistent over time. It decides who approves new tags and data uses, when a change in data practices triggers a new notice or banner version, how long consent records are kept, and how the whole setup gets audited.
Why do cookies still load after a visitor clicks Reject All?
Cookies usually keep loading after Reject All because some scripts never pass through the consent tool: pixels hard-coded into the site, tracking added by store apps, or scripts that load before the consent tool does. The Michigan study also found cookies nobody categorized and cookies the platform's crawler missed. California's regulator has said using a CMP doesn't shift that responsibility.
Does closing or ignoring a cookie banner count as consent?
Closing or ignoring a cookie banner doesn't count as consent under the GDPR, which requires a clear affirmative action such as clicking Accept. Under opt-out laws like California's CCPA, collection can continue until the person opts out, so the effect of an ignored banner depends on where the visitor is and which model the site uses there.
If someone rejects cookies after tracking already fired, are those cookies deleted?
A rejection stops tracking from that point on, but it doesn't undo what already happened: under GDPR Article 7(3), withdrawal doesn't make earlier processing unlawful. A site can clear the cookies it set itself, while data already sent to other companies needs separate handling. That's why the safer setup blocks non-essential tracking until the visitor chooses.
Does a website need a cookie banner in U.S. states without a privacy law?
A website can still face tracking claims in states without a comprehensive privacy law, because tracking lawsuits often rely on wiretap laws rather than comprehensive privacy laws. California's CIPA and Florida's wiretap law are both used this way. Location rules that switch a banner off by region were also one of the failure factors in the Michigan study.
What is consent lifecycle management?
Consent lifecycle management is the practice of handling a person's consent from the first notice through every later change: informing, collecting, recording, enforcing, and honoring withdrawals or renewals. The lifecycle view matters because most failures happen after the first click, when a choice has to reach every tool and stay current.
What is GDPR consent management?
GDPR consent management means meeting the GDPR's standard whenever consent is the legal basis. Consent must be freely given, specific, informed, and unambiguous, the business must be able to prove it, and withdrawing must be as easy as giving it. For cookies, the EU's ePrivacy rules add that non-essential cookies need that consent before they're set, and legitimate interest can't stand in for it.
How long should consent records be kept?
No law sets one retention period for consent records. A practical default is to keep each record for as long as the data it covers is in use, plus time to answer a complaint or claim. That's a different question from how long a choice stays valid: Ireland's regulator treats six months as the outer limit before asking a visitor again.
Do consent records carry over when a business switches consent platforms?
Consent logs can usually be exported and moved to a new platform, but the choice stored in each visitor's browser generally can't, because each platform uses its own cookie. Returning visitors see a banner again after a switch, so exporting the old logs first keeps the historical proof.
Osman Husain
Osman is the content lead at Enzuzo. He has a background in data privacy management via a two-year role at ExpressVPN and extensive freelance work with cybersecurity and blockchain companies. Osman also holds an MBA from the Toronto Metropolitan University.
LinkedIn →More related blogs
Your next read