PIPEDA vs GDPR, CCPA, HIPAA, and Other Privacy Laws
Osman Husain
Canada's closest counterpart to the GDPR is PIPEDA, the federal private-sector privacy law. It grants fewer individual rights than the GDPR and carries far lighter penalties.
Businesses in Alberta, British Columbia, or Quebec follow their province's private-sector law, not PIPEDA, for personal information they handle within the province. An Ontario hospital, clinic, or pharmacy follows PHIPA for patient records handled inside Ontario.
PIPEDA still applies to personal information that crosses a provincial or national border for commercial reasons.
| Law | Region | Who it covers | Consent standard | Max penalty | Key limit |
|---|---|---|---|---|---|
| PIPEDA | Canada (federal) | Any private-sector organization handling personal information in commercial activity, at any size (a substantially similar provincial law displaces it inside Alberta, BC, and Quebec) | Knowledge and consent by default; express for sensitive data; purposes limited to what a reasonable person would find appropriate | $100,000 on indictment, $10,000 on summary conviction, court-imposed, for a short list of section 28 offences | The Privacy Commissioner can't fine or issue binding orders; no general erasure or portability right today |
| GDPR | European Union | Controllers and processors of personal data | Any one of six lawful bases; consent is one option | Higher of EUR 20 million or 4% of worldwide annual turnover under Article 83, imposed by supervisory authorities | Consent is optional where another lawful basis applies |
| CCPA/CPRA | California, US | For-profit businesses doing business in California that meet one threshold: $25M+ revenue, 100,000+ consumers or households, or 50%+ of revenue from selling or sharing data | Notice plus a right to opt out of sale or sharing; opt-in only under 16 | $2,500 per violation; $7,500 per intentional violation or one involving a consumer under 16, under section 1798.155, assessed by the California Privacy Protection Agency | Thresholds leave many small businesses out; no general consent requirement to collect |
| HIPAA | United States (federal) | Covered entities (health plans, clearinghouses, providers transmitting health data electronically) and their business associates; protected health information only | No patient authorization for treatment, payment, or operations; written authorization for marketing, sale of PHI, and psychotherapy notes | Civil: tiered, $100 to $50,000 per violation, $1.5M annual cap per identical violation, inflation-adjusted under 45 CFR 160.404; criminal up to $250,000 and 10 years under 42 U.S.C. 1320d-6 | Sectoral: binds only covered entities and their contractors, and only health information |
| PHIPA | Ontario, Canada | Ontario health information custodians (hospitals, practitioners, pharmacies, long-term care homes) and their personal health information | Knowledgeable consent, express or implied; custodians providing care may rely on implied consent, but disclosure to a non-custodian needs express consent under section 18 | Offence fines up to $200,000 or one year in prison for an individual, and up to $1,000,000 for a corporation under section 72(2) | Applies only inside Ontario and only to custodians; PIPEDA still reaches cross-border data handled commercially, and non-custodians |
| PIPA (BC/AB) | British Columbia and Alberta, Canada | Private-sector organizations in each province (in BC, also non-profits, unions, and professional bodies) | Consent required to collect, use, or disclose; express, implied where the purpose is obvious, or opt-out after notice; judged by what a reasonable person would find appropriate | Offence fines up to $10,000 for an individual and $100,000 for an organization under each Act: BC section 56(2) and Alberta section 59(2) | Reaches only organizations in the province; PIPEDA governs federally regulated businesses and cross-border data |
PIPEDA vs GDPR: is PIPEDA Canada's GDPR equivalent?
PIPEDA is Canada's GDPR equivalent in role, as the federal private-sector privacy law, but not in strength. The EU treats the two as close enough to let commercial data flow to Canada without extra safeguards. Past that, the GDPR offers six lawful bases where PIPEDA requires consent, six rights where PIPEDA grants access and correction, and fines up to 4% of turnover where PIPEDA's ceiling is $100,000.
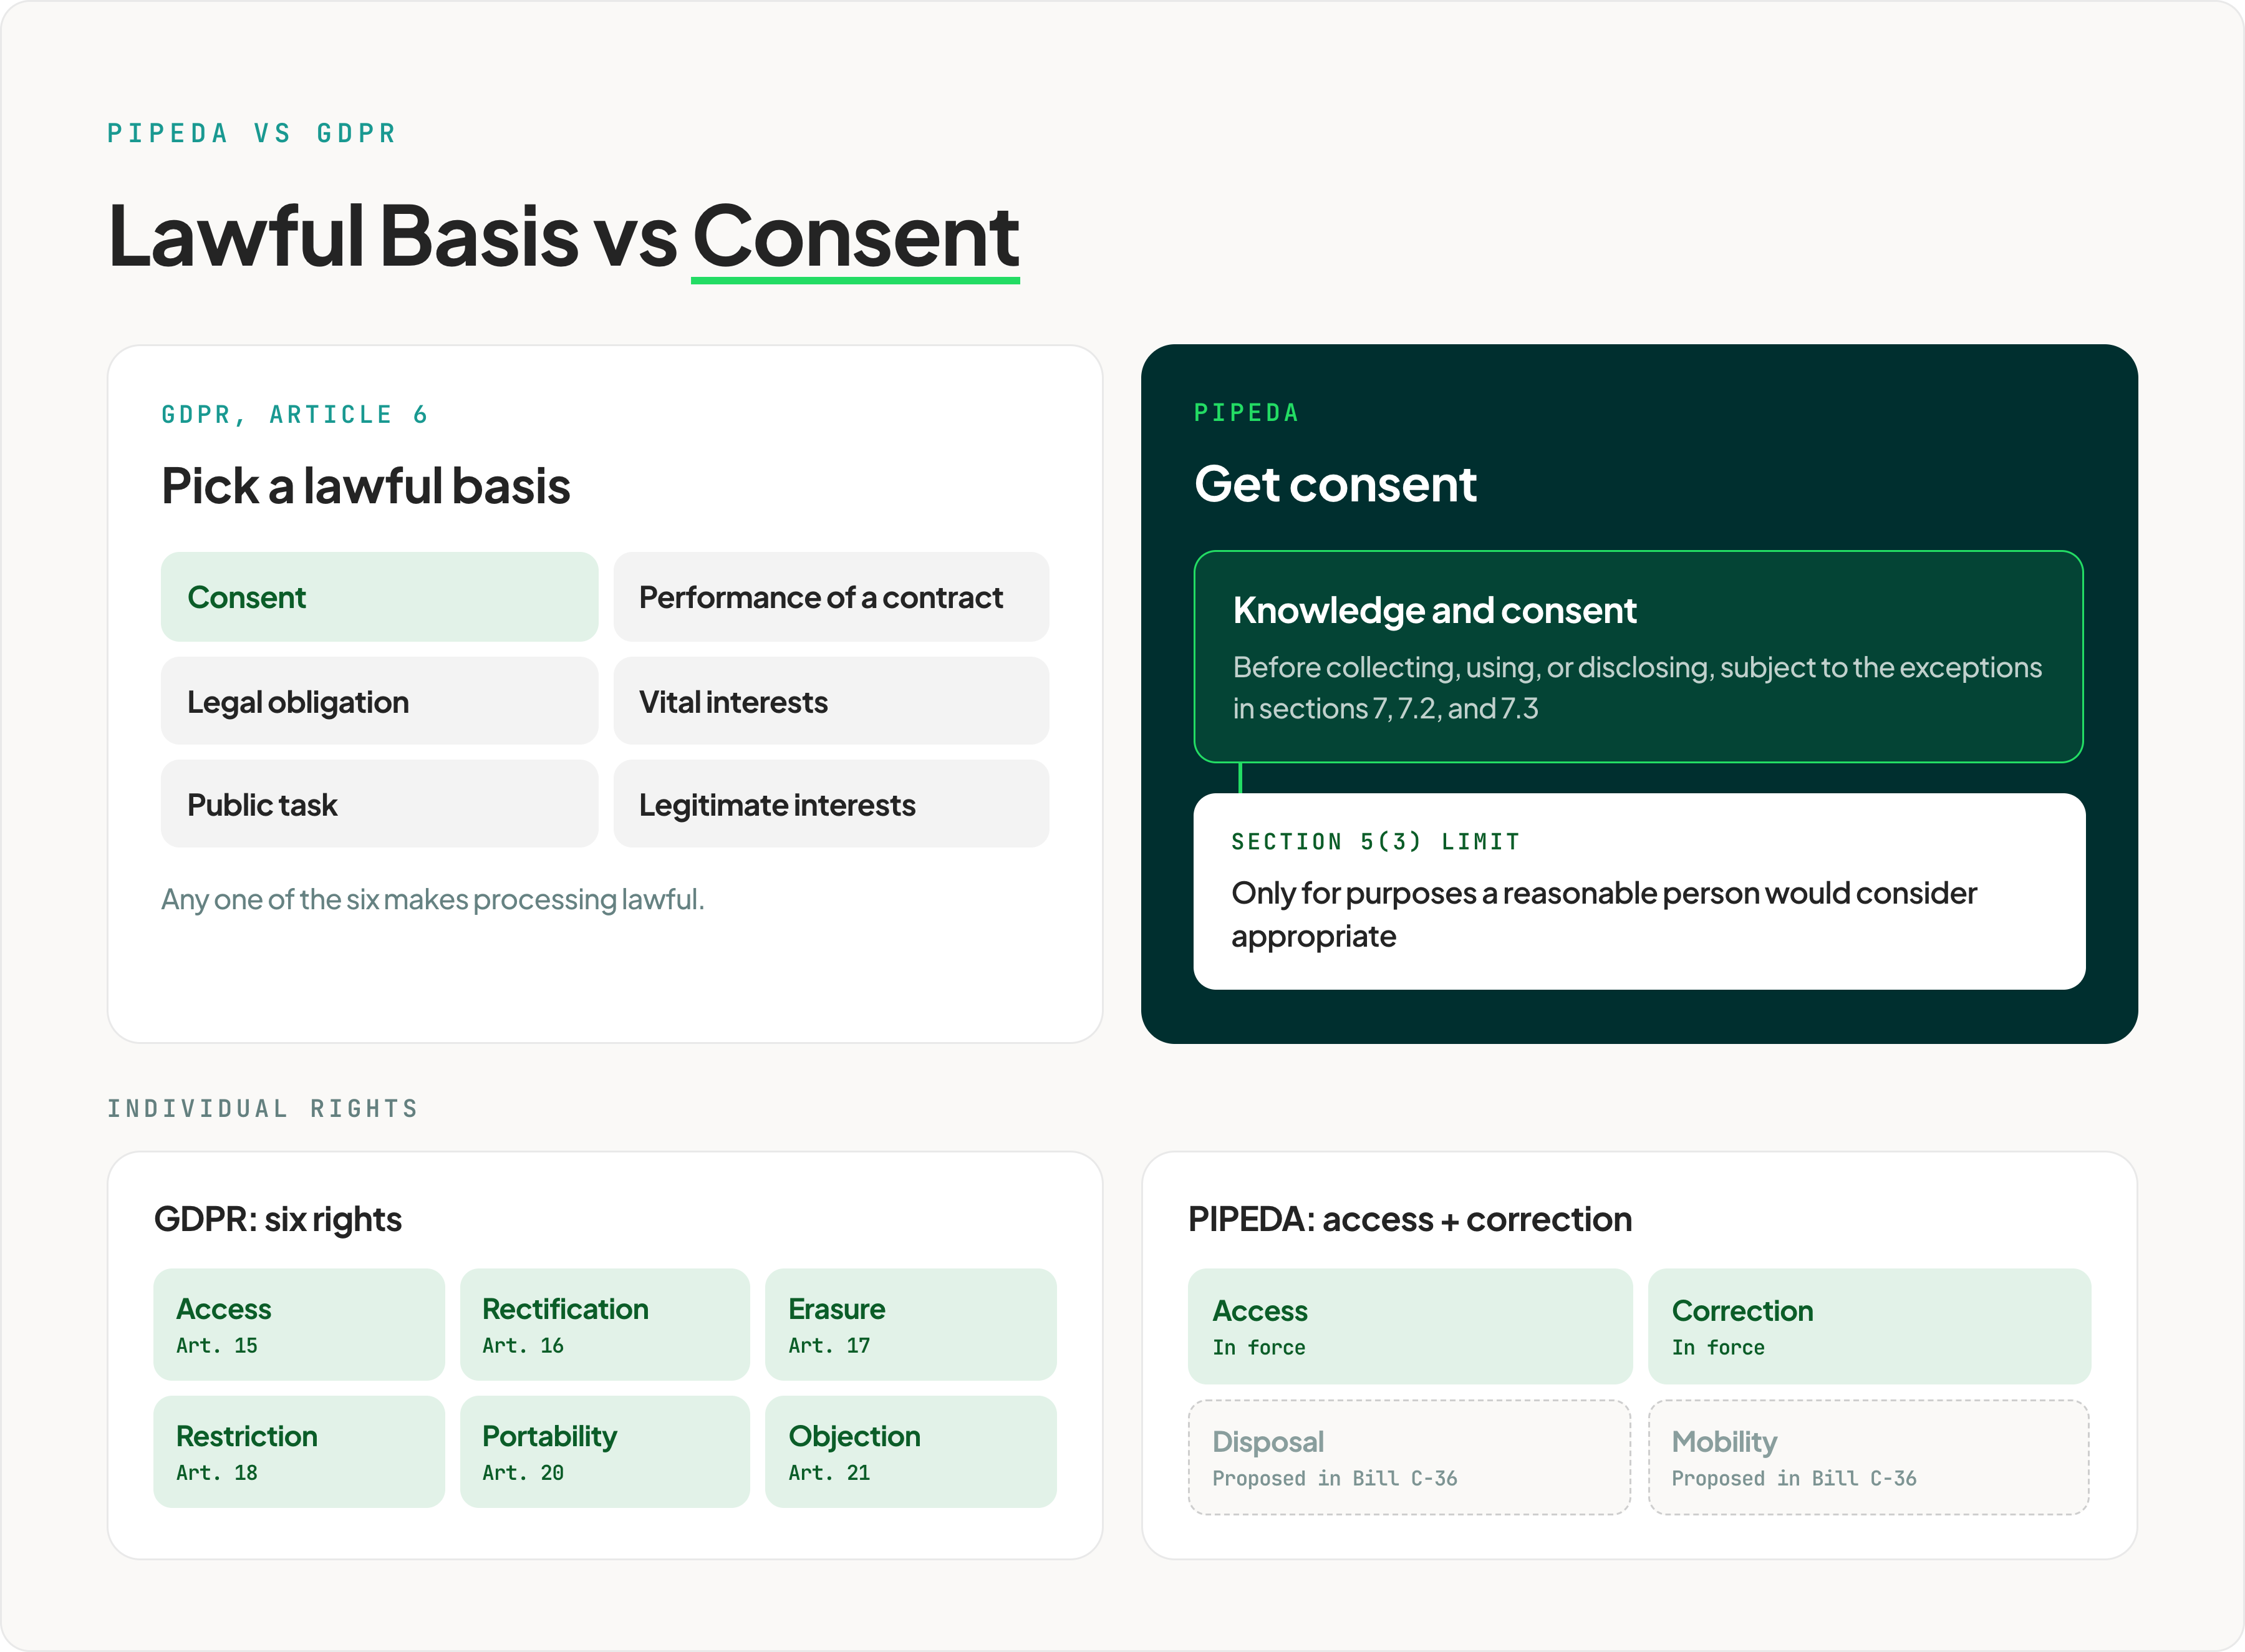
Under the GDPR, a business must choose a lawful basis before processing anything. Article 6 offers six: consent, performance of a contract, a legal obligation, vital interests, a public task, and legitimate interests. Any one of them makes the processing lawful, so consent is one option among six.
PIPEDA requires an individual's knowledge and consent before an organization collects, uses, or discloses their information, subject to the exceptions in sections 7, 7.2, and 7.3. Section 5(3) then limits collection, use, and disclosure to purposes a reasonable person would consider appropriate in the circumstances.
Consent can be express or implied depending on sensitivity; the Office of the Privacy Commissioner (OPC) expects express consent for sensitive information.
On individual rights, the GDPR's list is longer than PIPEDA's. Chapter 3 grants access (Article 15), rectification (16), erasure (17), restriction of processing (18), data portability (20), and objection (21).
Current PIPEDA grants access, and the right to challenge accuracy and have information corrected. Erasure, portability, and a standalone right to object don't exist in PIPEDA as it stands. Disposal and data mobility appear as proposals in Bill C-36.
Enforcement is where PIPEDA and the GDPR differ most. GDPR supervisory authorities can issue binding orders and fine in two tiers: up to the higher of EUR 10 million or 2% of worldwide annual turnover, and up to the higher of EUR 20 million or 4%.
Canada's Privacy Commissioner works as an ombudsperson. The OPC investigates, publishes findings, and makes recommendations; it can't order a change or impose a fine. PIPEDA's only fines attach to a short list of section 28 offences, such as knowingly failing to keep breach records or obstructing the Commissioner: $10,000 on summary conviction and $100,000 on indictment. Read the PIPEDA penalties guide for an in-depth breakdown.
A GDPR controller must notify its supervisory authority of a personal data breach without undue delay and, where feasible, within 72 hours of becoming aware of it.
Under PIPEDA, an organization reports to the Privacy Commissioner and notifies affected individuals only where it is reasonable to believe a breach creates a real risk of significant harm, as soon as feasible after it determines the breach occurred.
The GDPR requires a data protection officer where an organization is a public authority, where its core activities involve regular, systematic monitoring of people at scale, and where it processes special-category or criminal data at scale. PIPEDA has no DPO mandate. Its accountability principle requires an organization to designate someone accountable for compliance, whatever its size or risk profile.
The GDPR also makes a data protection impact assessment mandatory before processing likely to result in a high risk. PIPEDA sets no such duty, though the OPC still expects a privacy impact assessment for new projects involving personal information.
The EU's adequacy finding for Canada covers only commercial organizations subject to PIPEDA. It covers a Canadian retailer or SaaS vendor and doesn't extend to public bodies.
Bill C-36, the Protecting Privacy and Consumer Data Act, would narrow the GDPR vs PIPEDA penalty gap. Administrative fines would reach the higher of $10 million or 3% of gross global revenue, and fines on indictment the higher of $25 million or 5%. The bill was introduced and read a first time on June 15, 2026, and as of October 2026 awaits second reading in the House of Commons.
Unless and until Bill C-36 passes, PIPEDA is the GDPR's closest Canadian analogue, not its equal.
PIPEDA vs CCPA/CPRA: which is stricter, Canada's law or California's?
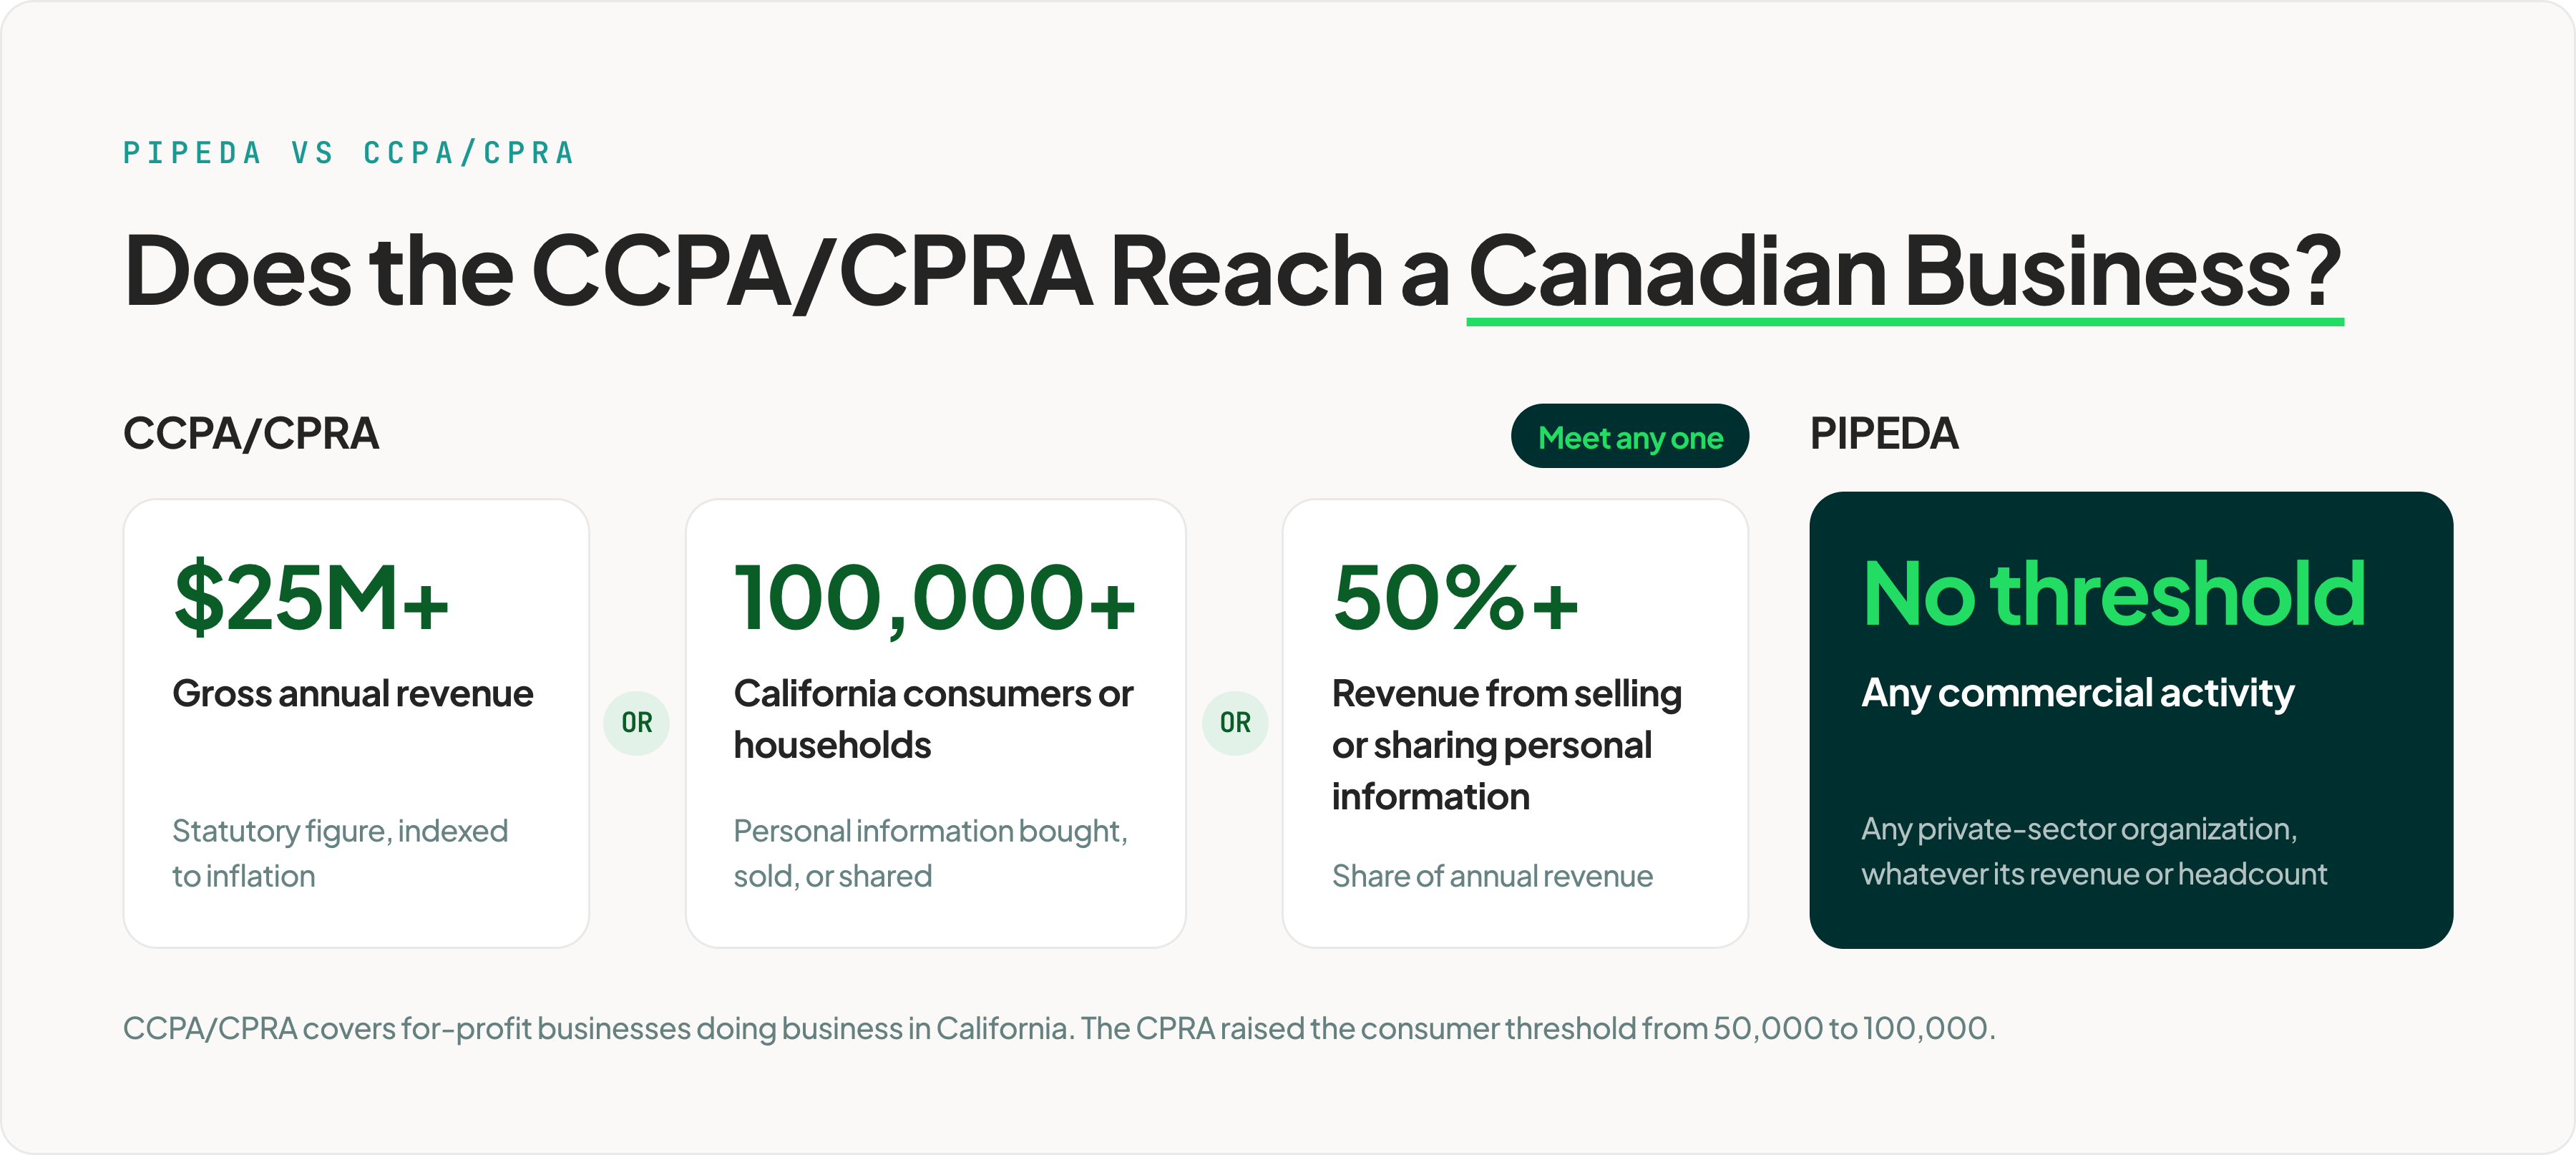
PIPEDA and California's CCPA/CPRA are strict in different places. PIPEDA covers commercial organizations of any size and requires consent up front; the CCPA/CPRA covers fewer businesses but itemizes more consumer rights.
PIPEDA has no size test: any private-sector organization handling personal information in commercial activity is in scope, whatever its revenue or headcount.
The CCPA/CPRA reaches only for-profit businesses that do business in California and clear at least one of three thresholds:
- more than $25 million in gross annual revenue
- processing the personal information of 100,000 or more California residents or households
- 50% or more of annual revenue from selling or sharing personal information
The CPRA doubled the second threshold from the original 50,000. A Canadian company that does business in California and meets one threshold is liable to both the PIPEDA and the CCPA.
Where PIPEDA asks for consent first, the CCPA/CPRA lets a business collect after giving notice. Consumers can opt out of the sale or sharing of their information. Opt-in consent is required only to sell or share the data of consumers under 16.
California itemizes more rights than PIPEDA. The CCPA/CPRA grants six consumer rights: the rights to know, delete, correct, opt out of sale or sharing, limit the use of sensitive personal information, and not be discriminated against for exercising them. Against that, PIPEDA's statutory rights are access and correction; a deletion right and portability are Bill C-36 proposals.
The California Privacy Protection Agency can assess administrative fines of up to $2,500 per violation under section 1798.155, rising to $7,500 per intentional violation or violation involving a consumer under 16. The Attorney General enforces alongside the agency, and consumers can sue directly over certain data breaches, with statutory damages up to $750 per incident.
PIPEDA's route runs through an investigation by the Privacy Commissioner and, if needed, the Federal Court, which can order corrective action and award damages.
PIPEDA vs HIPAA: does Canada have a HIPAA equivalent?
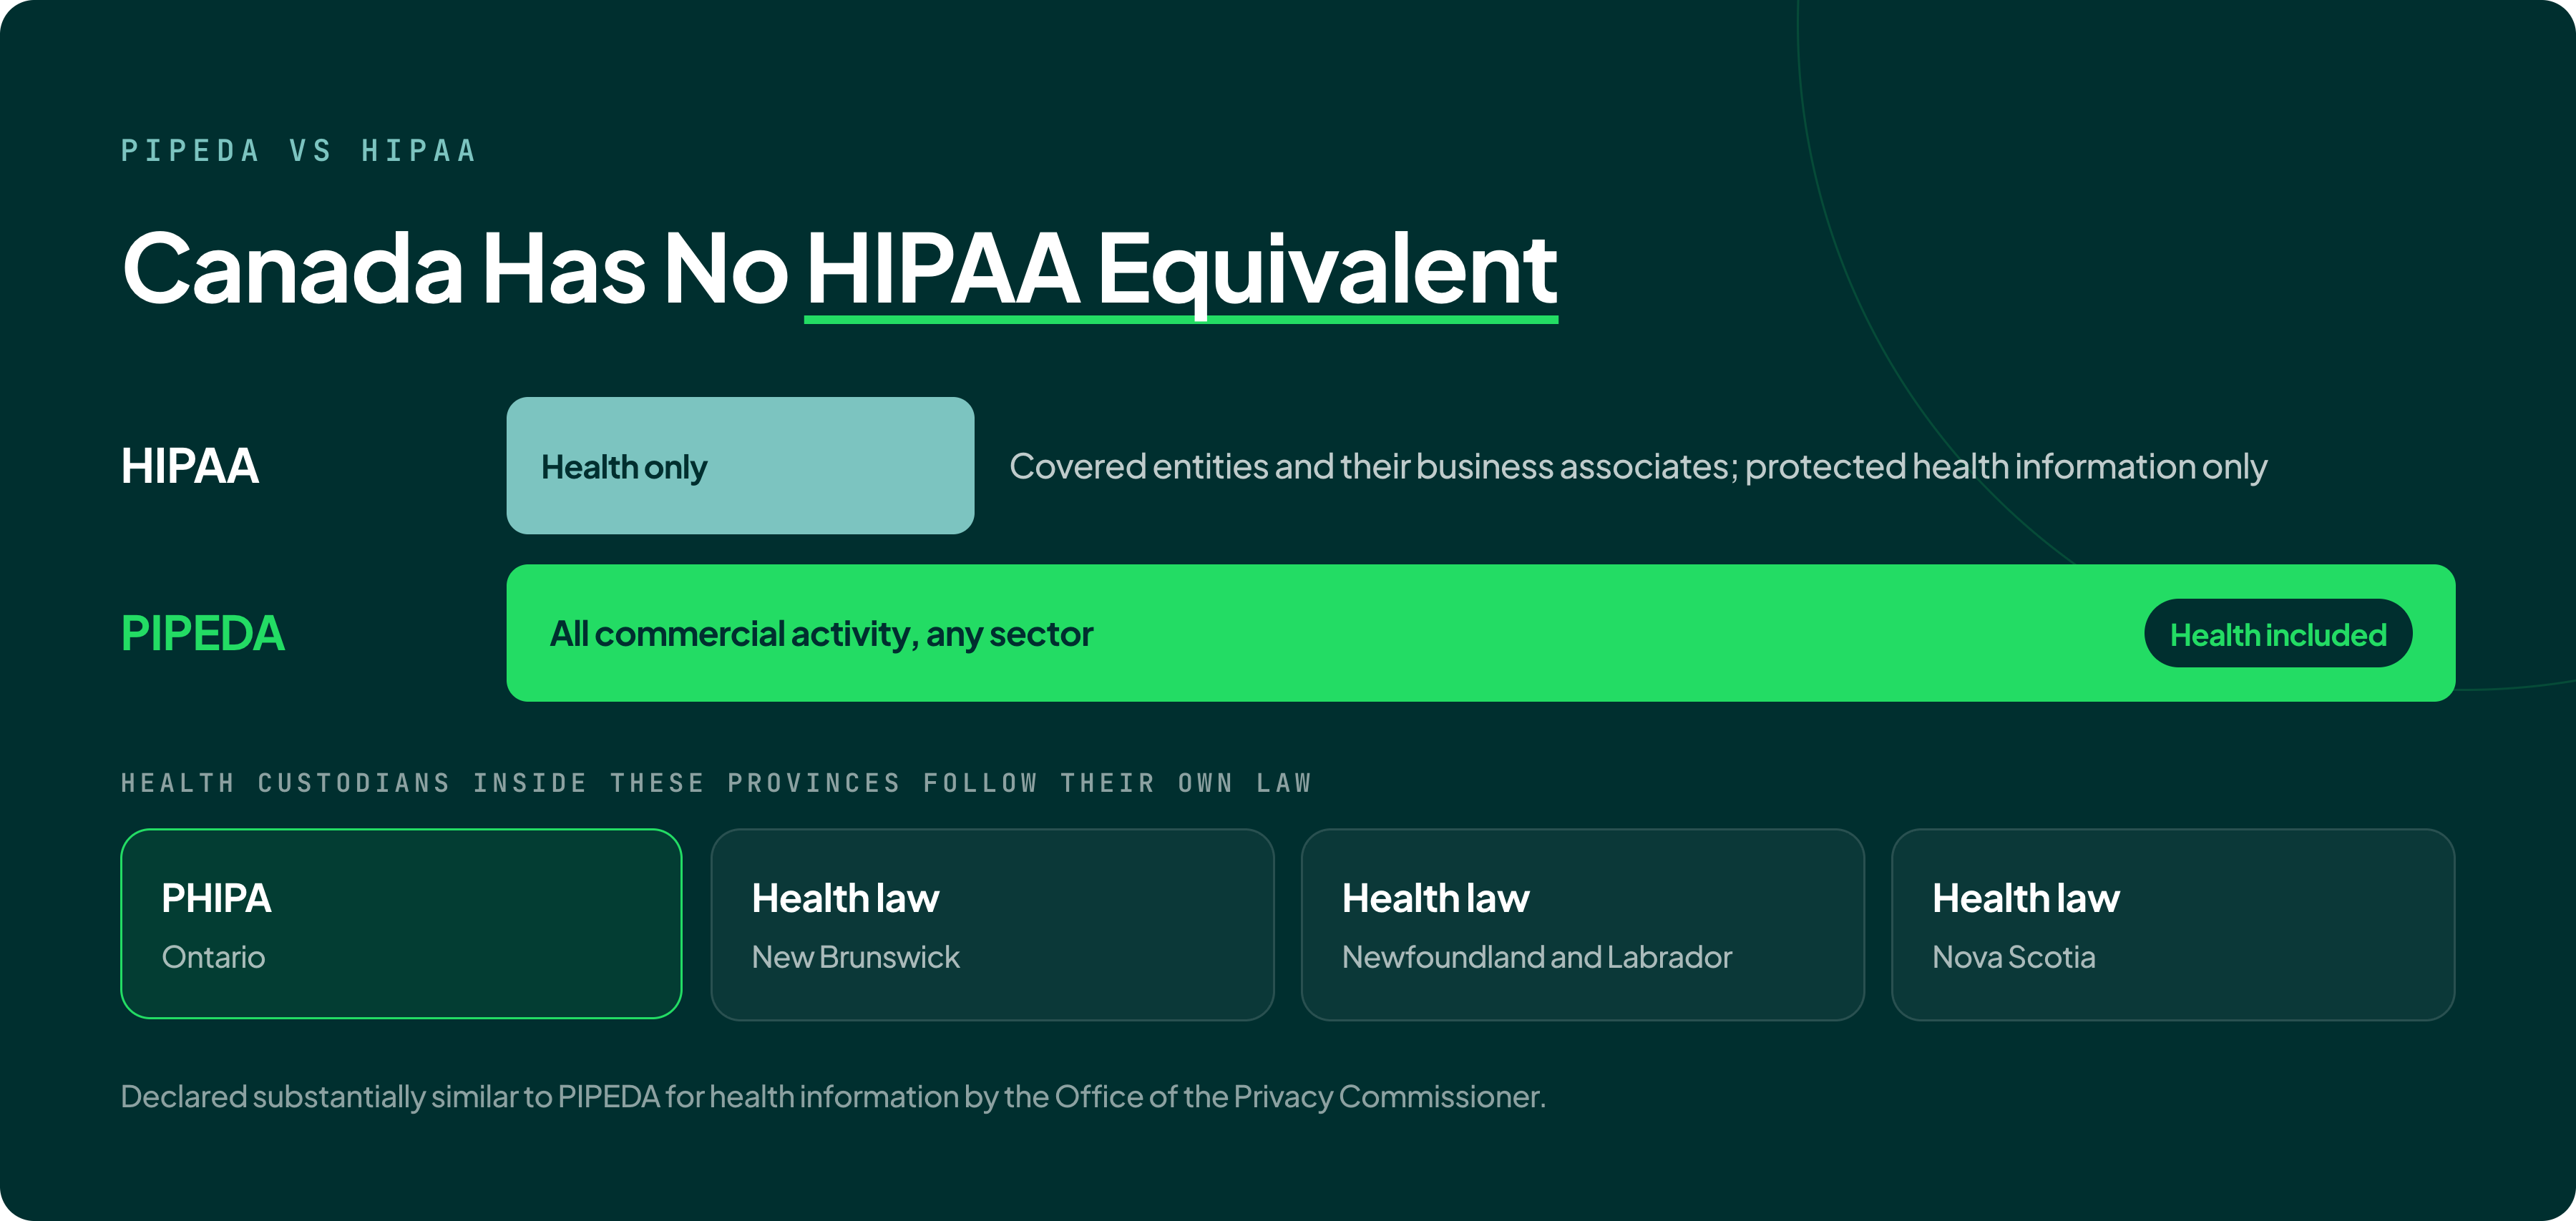
Canada has no HIPAA equivalent. Commercial health data falls under PIPEDA as ordinary personal information, and provincial health-privacy laws such as Ontario's PHIPA govern hospitals, clinics, and other custodians.
HIPAA is sectoral. Its Privacy Rule binds covered entities, meaning health insurers, healthcare clearinghouses, and providers that transmit health information electronically. It also binds the business associates that handle protected health information for them under a written contract. It protects one category of data, individually identifiable health information, and nothing else.
PIPEDA is omnibus. It applies to any organization handling personal information in the course of commercial activity, in any industry, and health information collected that way is considered personal information; the Act has no separate healthcare-specific verbiage.
HIPAA lets a covered entity use and disclose protected health information for treatment, payment, and health care operations without the patient's authorization. A written authorization is required only for specific uses: most marketing, any sale of protected health information, and psychotherapy notes. HIPAA permits by default what PIPEDA requires consent for.
HIPAA and PIPEDA both grant access and correction, on different clocks. Under HIPAA, a patient can inspect and copy their records, and the covered entity has 30 days to act, with one 30-day extension allowed.
PIPEDA gives an organization 30 days to answer an access request, with one extension of up to 30 more days in defined cases. Enzuzo's PIPEDA compliance checklist walks through the steps in detail.
HIPAA's penalties are heavier than PIPEDA's. Civil penalties run in four tiers keyed to culpability, from a violation the entity didn't know about up to willful neglect left uncorrected. The base ranges are $100 to $50,000 per violation, with a $1.5 million annual cap for identical violations, adjusted for inflation each year.
Criminal penalties climb through three tiers, topping out at up to $250,000 and ten years in prison for obtaining or disclosing health information with intent to sell it or cause harm. PIPEDA carries no administrative fine for a privacy violation, only the narrow section 28 offences.
The closest Canadian counterparts to HIPAA are provincial healthcare laws. The OPC has declared the health-privacy laws of Ontario (PHIPA), New Brunswick, Newfoundland and Labrador, and Nova Scotia substantially similar to PIPEDA for health information. Other provinces have health-privacy laws without that designation.
A Canadian vendor that creates, receives, maintains, or transmits protected health information for a US covered entity meets HIPAA's definition of a business associate, and the covered entity has to bind it by written contract. That contract doesn't displace PIPEDA; both apply.
PIPEDA vs PHIPA: does PHIPA replace PIPEDA in Ontario?
PHIPA doesn't replace PIPEDA. A federal exemption order removes Part 1 of PIPEDA from Ontario's health information custodians for personal information they collect, use, and disclose inside the province. PIPEDA keeps applying to everything the order doesn't cover.
Ontario's PHIPA, the Personal Health Information Protection Act, 2004 (S.O. 2004, c. 3, Sched. A), is a provincial, health-sector law. Section 1 states its purposes: rules for collecting, using, and disclosing personal health information that protect confidentiality while letting care happen, and a right of access for individuals to their records. The Information and Privacy Commissioner of Ontario oversees it.
PHIPA applies to health information custodians, a defined list in section 3(1) of the Act:
- health care practitioners and group practices
- hospitals, psychiatric facilities, and integrated community health services centres
- long-term care homes and retirement homes
- pharmacies
- health service providers that form part of an Ontario Health Team
Personal health information, defined in section 4(1), is identifying information about a person's physical or mental health or the health care they receive. It extends to their health number, their substitute decision-maker, and their digital health identifier.
The order that removes PIPEDA's overlap with PHIPA is the Health Information Custodians in the Province of Ontario Exemption Order (SOR/2005-399), made under paragraph 26(2)(b) of PIPEDA. It followed the federal declaration that PHIPA is substantially similar to PIPEDA. It was registered on November 28, 2005 and took effect the same day.
Section 1 of the order exempts any custodian PHIPA applies to from Part 1 of PIPEDA, for the collection, use, and disclosure of personal information that occurs within the Province of Ontario. That geographic limit is where PIPEDA comes back in.
PIPEDA still applies to an Ontario custodian's activities that fall outside the order, and to the organizations PHIPA never covered:
- personal information that crosses a provincial or national border, where the custodian's handling of it counts as commercial activity under PIPEDA (a publicly funded hospital delivering insured care may not meet that trigger)
- federal works, undertakings, and businesses operating in Ontario
- an organization that isn't a health information custodian, handling personal information in the course of commercial activity
PHIPA's rule for a custodian's vendors is stricter than PIPEDA's rule for a processor. A custodian stays responsible for personal health information in its custody or control, and its agents may collect, use, or disclose that information only where the custodian permits it and could lawfully do so itself.
Under PIPEDA, an organization remains responsible for personal information it transfers to a third party for processing, and secures comparable protection by contract rather than through a defined agent status.
An Ontario custodian that sends records to a US processor as part of a commercial activity is back under PIPEDA's cross-border duties, which the transfers guide covers. The order removes the overlap between the two laws for custodians inside Ontario; nothing in PIPEDA was repealed.
PIPEDA vs PIPA: which Canadian privacy law applies to your business?
Three Canadian provinces have general private-sector privacy laws the federal government has declared substantially similar to PIPEDA: Alberta, British Columbia, and Quebec.
An organization registered in either one of them is generally exempt from PIPEDA for personal information it handles that stays inside that province. For example, an online store in Alberta processing orders in Calgary and Edmonton alone is not subject to PIPEDA. But if that store starts to accept orders from Ontario, the situation changes and PIPEDA is now in effect.
The three provincial privacy laws are:
- British Columbia's Personal Information Protection Act (BC PIPA, SBC 2003, c. 63), in force since January 1, 2004 and overseen by the Office of the Information and Privacy Commissioner for BC
- Alberta's Personal Information Protection Act (Alberta PIPA, SA 2003, c. P-6.5), in force since January 1, 2004, deemed substantially similar that year, and overseen by Alberta's OIPC
- Quebec's Act respecting the protection of personal information in the private sector (P-39.1), substantially amended by Law 25 in phases from 2022 to 2024 and overseen by the Commission d'accès à l'information (CAI)
BC's PIPA reaches further than PIPEDA in one direction: it covers non-profits, unions, and professional bodies as well as businesses, where PIPEDA reaches an organization only through its commercial activity. The BC regulator reads it as covering BC organizations that handle information about people, regardless of corporate type.
Employee data is the clearest difference between PIPEDA and the two PIPAs. BC's and Alberta's Acts both regulate employee personal information directly: BC PIPA sections 13, 16, and 19, and Alberta PIPA sections 15, 18, and 21. Each allows an employer to collect, use, or disclose it without consent where that's reasonable for the employment relationship.
PIPEDA reaches employee information only at federally regulated employers such as banks, airlines, and telecoms. A provincially regulated employer in BC or Alberta follows its PIPA for staff data; PIPEDA doesn't reach it.
Alberta's PIPA is under review. A legislative committee reported in February 2025 with 12 recommendations, and the government ran a public survey in February 2026. No amendment bill has been tabled, and the 2003 Act remains the law.
Quebec's law is widely regarded as Canada's strictest private-sector privacy regime. Its regulator, the CAI, can impose administrative monetary penalties of up to the greater of 2% of worldwide turnover or CAD $10 million. Penal fines run from CAD $15,000 up to the greater of CAD $25 million or 4% of worldwide turnover, doubled for a repeat offence.
Law 25 applies to a business for its operations in Quebec. Under it, technology products offered to the public must default to the highest confidentiality settings. Quebec's transfer rules, including the assessment before data leaves the province, are covered in the transfers guide.
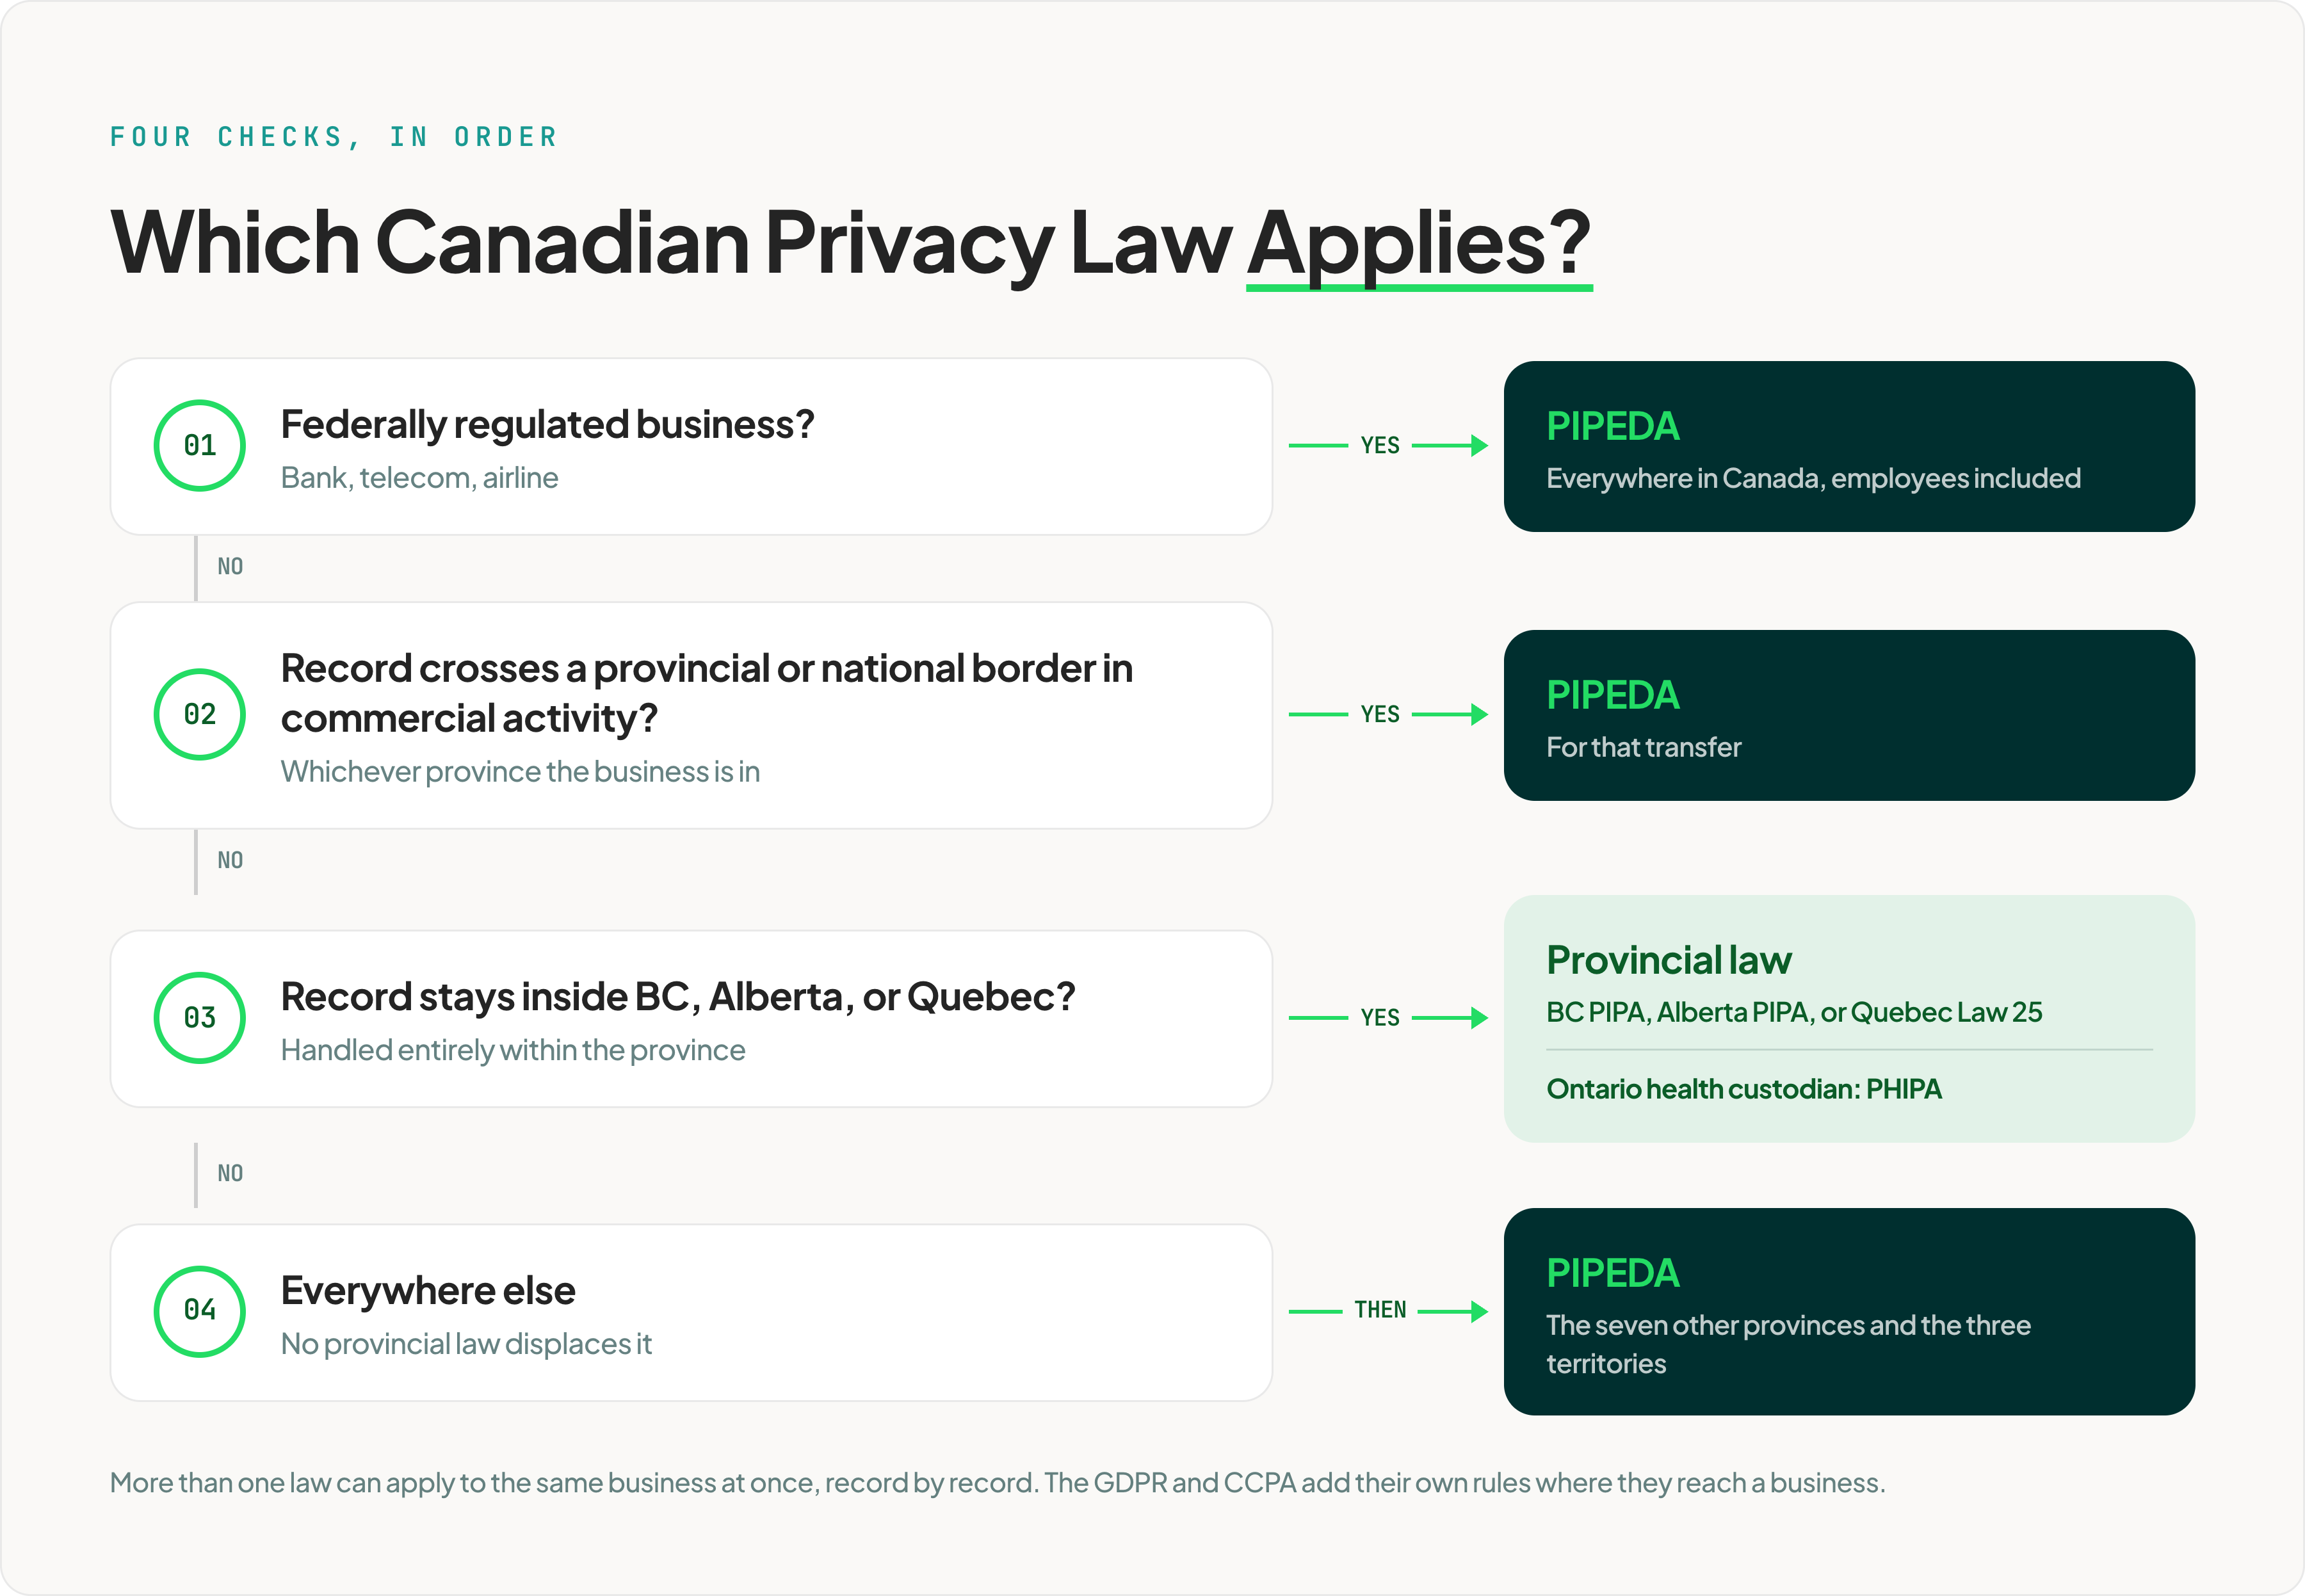
These four checks can help businesses decide which law applies:
- Banks, telecoms, airlines, or other federally regulated businesses: PIPEDA applies to how you handle personal information everywhere in Canada, including employees.
- If the record crosses a provincial or national border in the course of commercial activity, PIPEDA applies to that transfer, regardless of which province the business is in.
- If the record stays inside BC, Alberta, or Quebec, that province's law applies. In Ontario, health custodians follow PHIPA for personal health information, and three Atlantic provinces have health laws with the same substantially similar status.
- PIPEDA applies everywhere else in Canada: the seven other provinces and the three territories.
More than one law can apply to the same business at once. A BC retailer shipping to Alberta customers, or a Quebec SaaS company with users in Ontario, is under a provincial law for some records and PIPEDA for others.
Enzuzo's consent management platform shows a different consent experience by region, so one banner setup can serve PIPEDA, GDPR, and CCPA visitors. Its data request form takes in the access requests these laws grant.
To audit your PIPEDA compliance posture, speak with an in-house expert for a free evaluation.
Frequently asked questions
Does PHIPA replace PIPEDA for Ontario hospitals and clinics?
No, PHIPA doesn't replace PIPEDA; the two laws divide the territory. The federal Health Information Custodians in the Province of Ontario Exemption Order (SOR/2005-399) exempts Ontario's health information custodians from Part 1 of PIPEDA for personal information handled inside the province, where PHIPA governs. PIPEDA still reaches cross-border flows in commercial activity, federally regulated businesses, and any organization PHIPA doesn't cover.
Is PIPEDA stricter than the GDPR?
No, PIPEDA is not stricter than the GDPR overall. PIPEDA is stricter on one point: it requires consent where the GDPR offers six lawful bases. On regulator power and penalties, the GDPR is the tougher law: its authorities issue binding orders and fine up to 4% of turnover. The Privacy Commissioner can only recommend, and PIPEDA's ceiling is $100,000.
Does the CCPA apply to Canadian companies?
Yes, the CCPA/CPRA applies to a for-profit Canadian company that does business in California and meets one of its three thresholds. Those are revenue over $25 million (indexed to inflation), a set volume of Californians' personal information, or a set share of revenue from selling or sharing it. PIPEDA duties for Canadian customers continue alongside.
Does PIPEDA cover health information?
Yes, PIPEDA covers health information when an organization handles it in the course of commercial activity. It treats that data as personal information like any other, with no separate health regime. Canada has no federal equivalent of HIPAA. Provincial health-privacy laws such as Ontario's PHIPA govern health custodians inside their own provinces.
Does HIPAA apply to Canadian companies?
HIPAA applies to a Canadian company when it meets the definition of a business associate: it creates, receives, maintains, or transmits protected health information for a US covered entity. That covered entity must bind it by written contract. Otherwise a Canadian company is outside HIPAA, and PIPEDA or a provincial health law such as PHIPA governs its health data.
Does PIPEDA apply in Alberta, British Columbia, and Quebec?
Yes, PIPEDA still applies in Alberta, British Columbia, and Quebec, to federally regulated businesses such as banks and telecoms and to personal information that crosses a provincial or national border. Everything else a business handles within the province falls under the provincial law: Alberta's PIPA, BC's PIPA, or Quebec's private-sector act as amended by Law 25.
Would Bill C-36 make PIPEDA equivalent to the GDPR?
No, Bill C-36 would not make PIPEDA the GDPR's equal; it would narrow the penalty gap. It would replace Part 1 of PIPEDA and set administrative fines up to the higher of $10 million or 3% of global revenue and fines on indictment up to the higher of $25 million or 5%. It had first reading on June 15, 2026 and awaits second reading; PIPEDA is unchanged.
Osman Husain
Osman is the content lead at Enzuzo. He has a background in data privacy management via a two-year role at ExpressVPN and extensive freelance work with cybersecurity and blockchain companies. Osman also holds an MBA from the Toronto Metropolitan University.
LinkedIn →More related blogs
Your next read