Osman Husain
No, PIPEDA doesn't require personal information to be stored in Canada. A business can use a service provider or cloud host abroad, as long as it remains accountable for the data and provides comparable protection through contract or other means (Schedule 1, 4.1.3).
Under PIPEDA's openness principle, the Office of the Privacy Commissioner (OPC) expects you to tell people plainly that their data may be processed abroad, where a foreign court or government could reach it.
A common myth about PIPEDA is that it forces Canadian data to stay in Canada. In fact, the Act is silent on where data is stored; what it governs is how the data is protected once it moves. Three duties apply: accountability, safeguards, and openness. They follow the data wherever it goes.
Does PIPEDA require data to be stored in Canada?
PIPEDA has no data-localization rule: neither the Act nor its regulations name a country where personal information must be stored. A transfer abroad runs under the same accountability, safeguard, and openness duties that apply at home. You can store or process Canadian customers' data in the US, the EU, or anywhere else, as long as you meet those duties.
The confusion usually comes from other laws that do restrict where data goes; none of them is PIPEDA:
- Public-sector residency rules. Nova Scotia's Personal Information International Disclosure Protection Act (PIIDPA) requires public bodies and their service providers to keep personal information in Canada, with narrow exceptions, until a modernized law replaces it in 2027. British Columbia dropped its equivalent rule in 2021.
- Quebec's Law 25. Before a business sends personal information outside Quebec, Law 25 requires a privacy impact assessment (section 17). The data can go only if that assessment finds it will receive adequate protection under a written agreement. It applies to any enterprise doing business in Quebec, and the prevailing view is it also reaches companies outside the province that handle Quebec residents' data, so a company based elsewhere is not automatically outside its scope.
- Alberta's PIPA. A business that uses a service provider outside Canada has to notify the individuals affected (section 13.1) and list the destination countries and purposes in its privacy policy (section 6(2)).
What does PIPEDA require for a cross-border transfer?
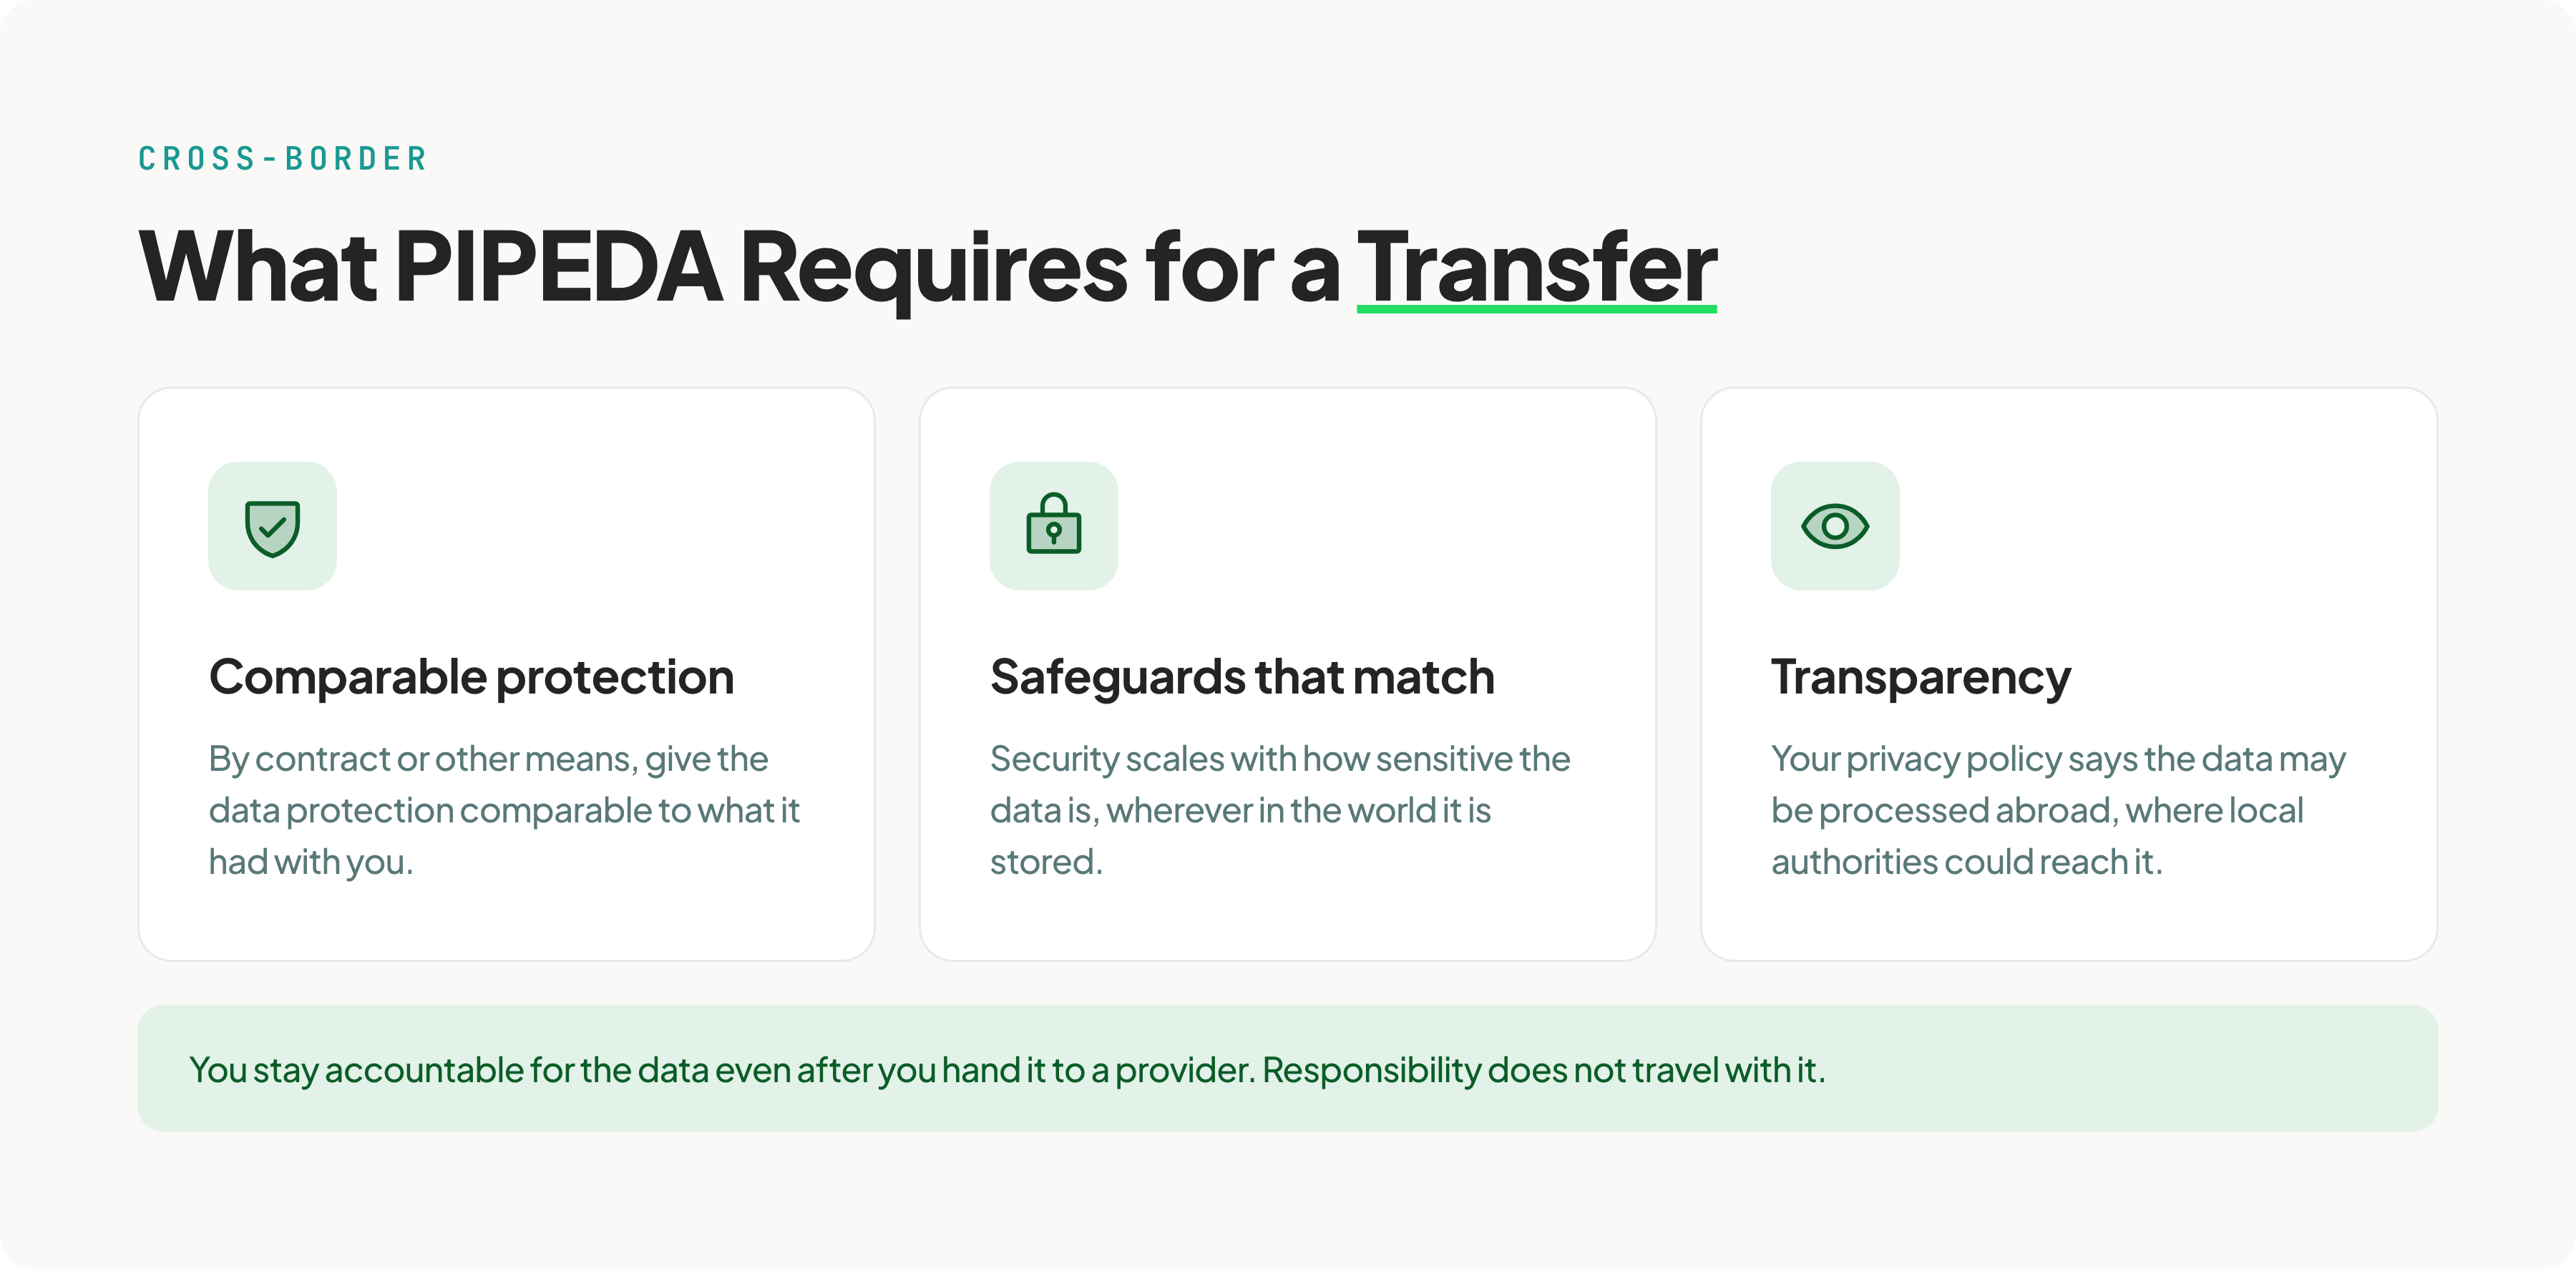
Under PIPEDA, responsibility for personal information remains with the business that first obtained it. Whether it's transferred internally or outside Canada, the primary entity responsible for it will not change. These four duties are explicitly required:
- Comparable protection. Use contracts or other means to give the data protection comparable to what it had when it was stored in Canada.
- Safeguards that match sensitivity. Security around the data scales with its sensitivity, wherever it's stored (4.7).
- A risk assessment first. The OPC expects you to weigh the risks before you transfer, including the destination country's legal regime and any government access powers (see cross-border guidelines).
- Transparency. Tell people plainly that their data may be processed in another country, where local courts or authorities could reach it.
Transfers into Canada are simpler: the EU's adequacy decision for Canada covers personal information an EU business sends to a company subject to PIPEDA, so those transfers need no extra mechanism.
Transfers for processing: what is the OPC's position?
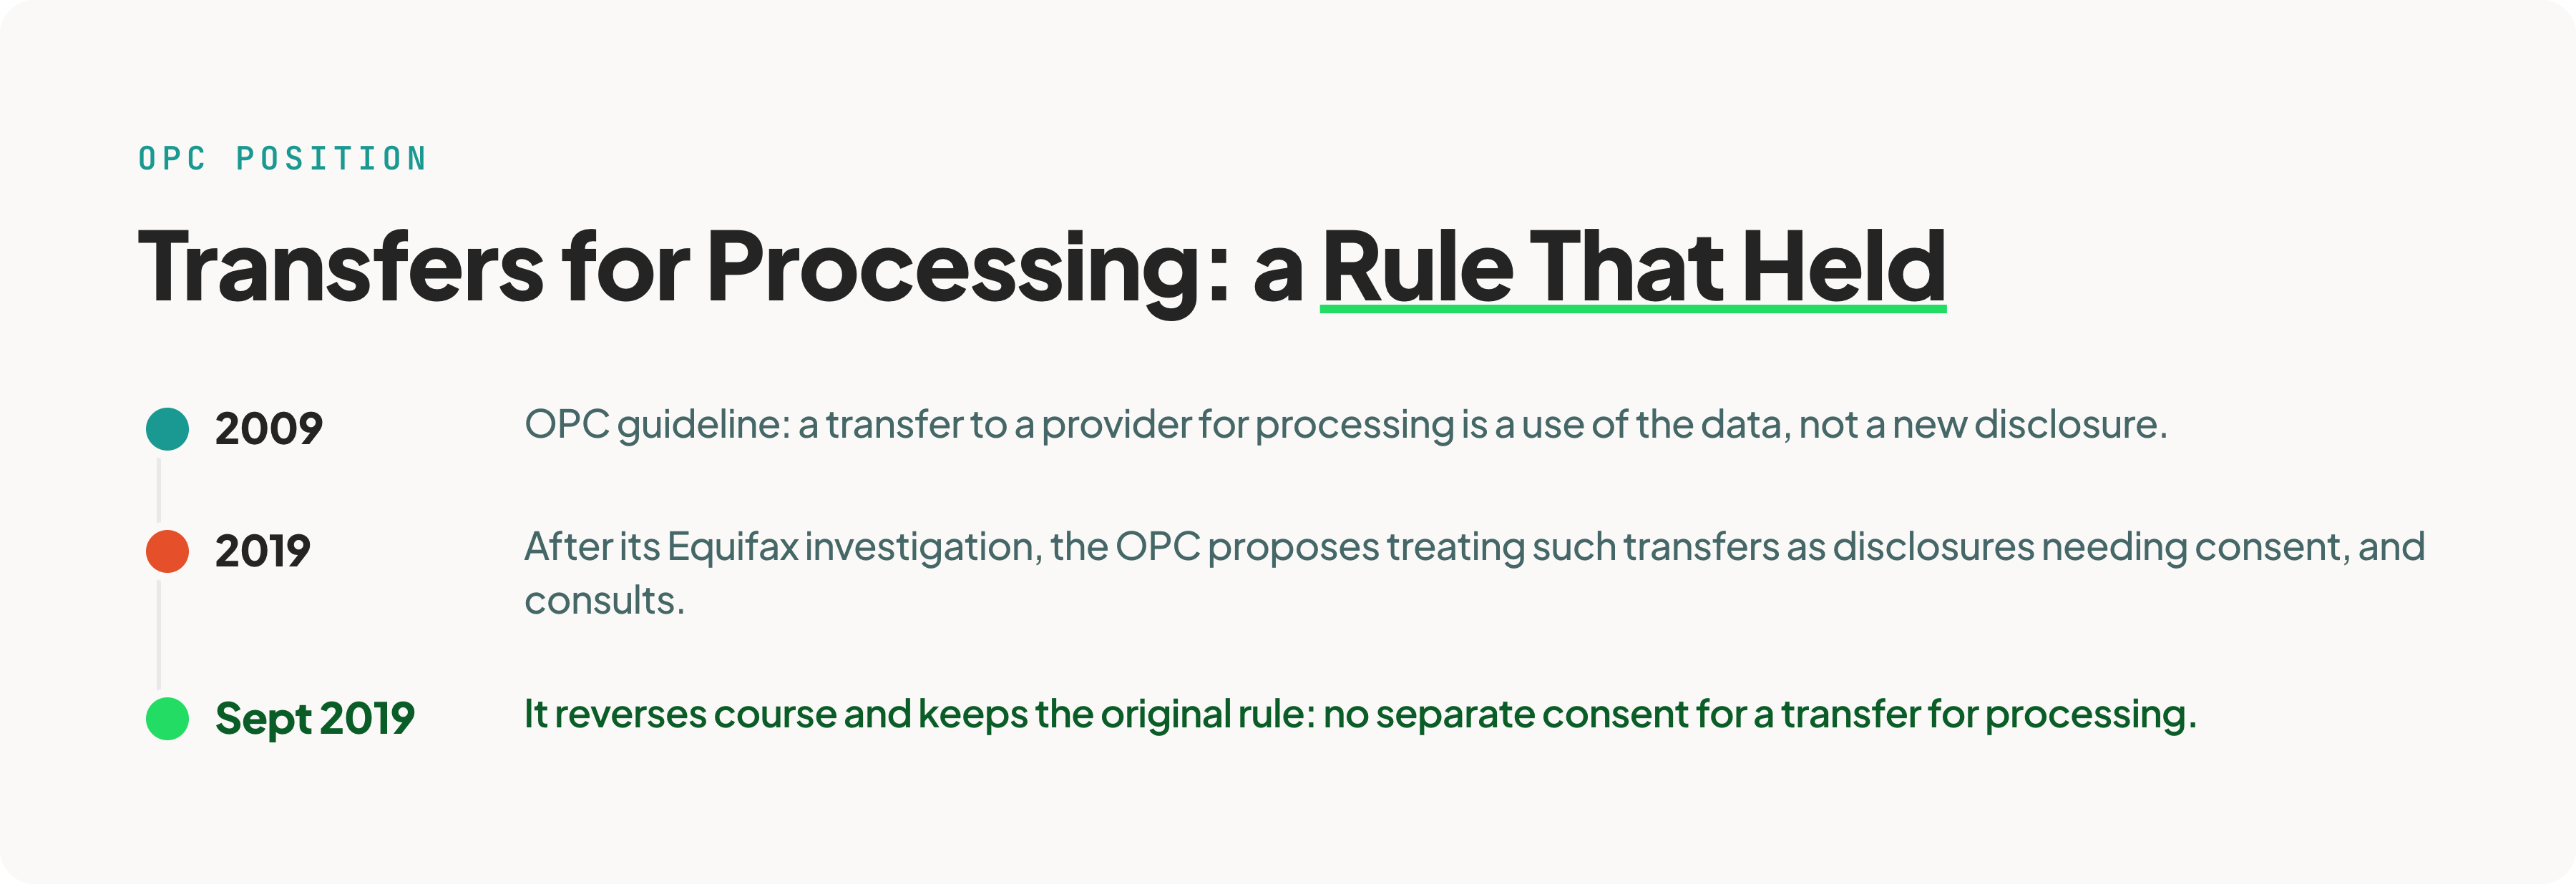
A transfer to a provider for processing counts under PIPEDA as a use, not a new disclosure, so it doesn't need separate consent. Your existing consent covers the purpose, and sending the data to a processor to serve that purpose is part of the same use.
The OPC tested that position in its 2019 Equifax investigation. It found the company had failed to protect Canadians' data transferred to its US parent for processing, and it proposed treating such transfers as disclosures that need their own consent. It opened a public consultation, then in September 2019 dropped the proposal and kept the 2009 rule: no separate consent for a transfer for processing.
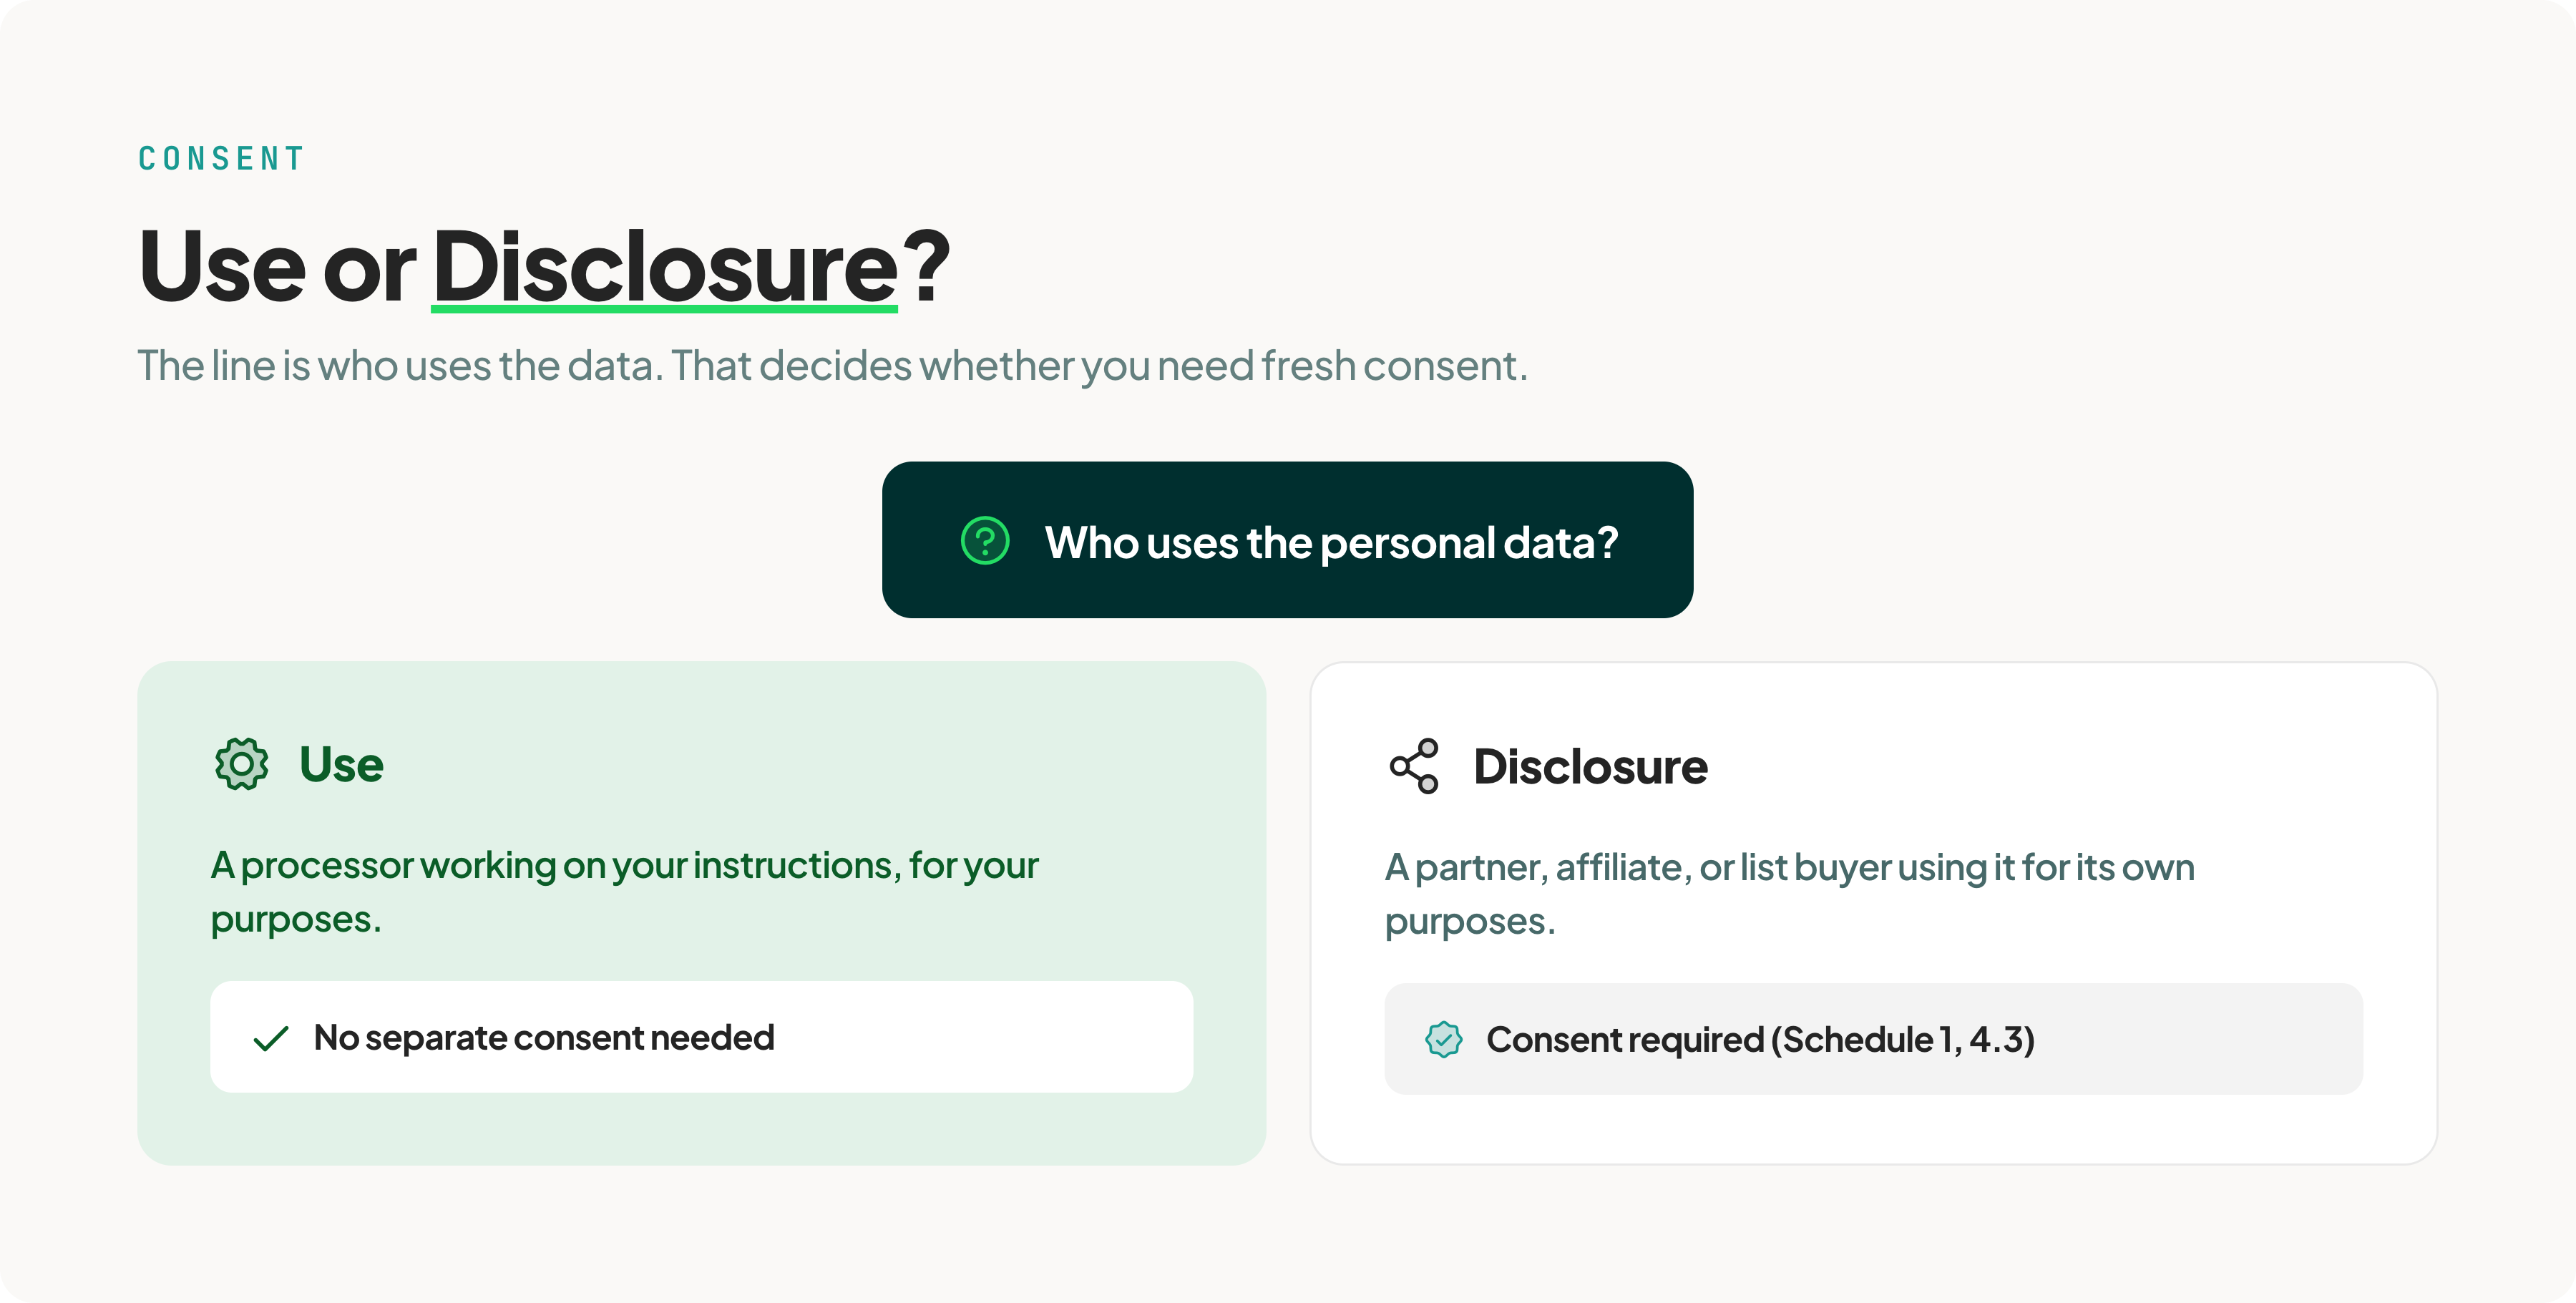
The line between a use and a disclosure is who uses the data. A processor works on your instructions and for your purposes, so the transfer is a use.
A recipient that uses the information for its own purposes, such as a partner, an affiliate selling its own services, or a buyer of a customer list, receives a disclosure. Disclosure needs the person's knowledge and consent (Schedule 1, 4.3).
An individual can't refuse the transfer itself. Their consent is to the purpose, so their lever is withdrawing that consent (Schedule 1, 4.3.8), not vetoing which processor you use.
Bill C-36, at second reading as of September 2026, could revisit these rules; the OPC said in 2019 it wanted a reformed law to address transfers.
Do you need a data processing agreement under PIPEDA?
PIPEDA doesn't require a data processing agreement by that name, or any single prescribed contract. What it requires is comparable protection by contractual or other means (Schedule 1, 4.1.3).
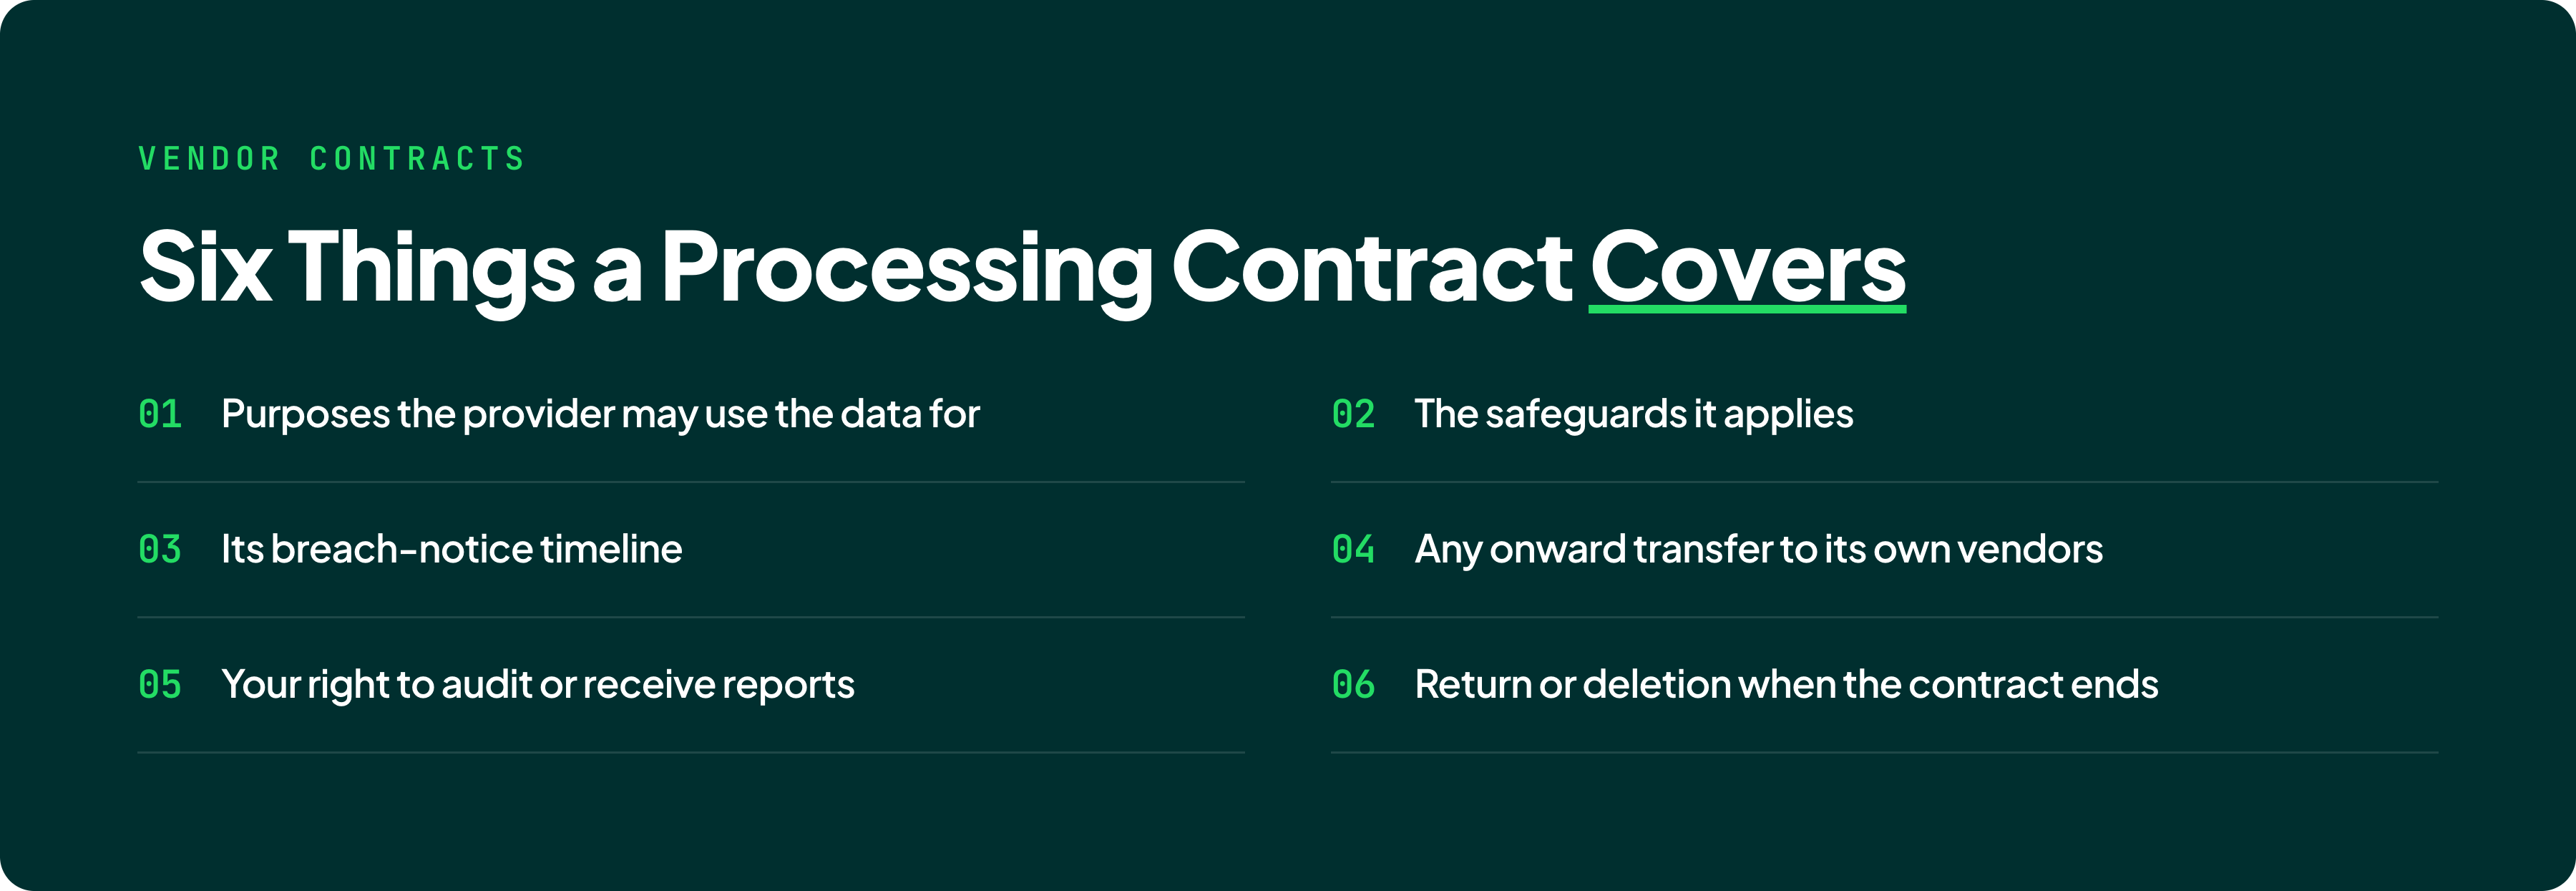
A written agreement, where you can get one, should give the transfer real substance, not just a label:
- the provider uses the data only for the purposes you set, not its own (4.1.3)
- its safeguards match the sensitivity of the data (4.7)
- you can verify its practices, by audit or by its own compliance reports
- any onward transfer to its sub-processors, including further transfers abroad, carries the same terms
- it tells you about a breach fast enough for you to meet your own reporting deadline
- it tells you, where the law allows, when a foreign authority compels the data, since no contract overrides that country's law
The PIPEDA compliance checklist covers vendor due diligence as one of its steps.
PIPEDA's transfer rules for SaaS and cloud companies
A SaaS company can fall on either side of the transfer rule, so the duties depend on its role.
When you use a US or EU cloud host, you are the customer. You carry the comparable-protection terms in your contract with the host, and your privacy notice tells your users about the cross-border processing.
SaaS providers are the data processor, too. Your business customer remains the accountable organization, so your job is to hold up your end. Notify it of a breach fast enough for it to report on time, pass the same protection terms to any sub-processors you use abroad, and use its data only for the service it bought.
Either way, the provider's location matters, because data held in another country is subject to that country's laws, including lawful-access powers that differ from Canada's. You can't contract that risk away, but you can be open about it, which is what PIPEDA's openness principle asks.
Cross-border transfer risk
The fastest way to find your transfer risk is to list every provider that touches Canadian personal data. Then ask, for each one, whether your contract requires comparable protection and whether your privacy policy tells people the data leaves Canada. A gap in either is where a complaint would land.
The disclosure itself can be short. A line like "We use service providers in the United States to process your data, where it may be subject to US law" meets the openness duty for most sites.
Enzuzo's consent management platform records what visitors agreed to, and its privacy policy generator keeps your disclosures, including the cross-border notice, in one place. The transparency part of a transfer is then on record.
Frequently asked questions
Can I store Canadian customers' data outside Canada?
Yes, personal information about people in Canada can be stored on servers outside Canada, including with a US or overseas cloud provider. The duty to protect it stays with you, met by contract or other means. Your privacy policy tells people the data may go abroad. No approval or data-localization step is required under federal law.
Does PIPEDA require consent to transfer data to a processor in another country?
No, PIPEDA doesn't require a separate consent for a transfer to a processor abroad. It treats the transfer as a use of the information rather than a disclosure, so the consent you have for the original purpose covers it. The OPC confirmed this in its 2019 conclusion. Your obligations are accountability and transparency.
Is a data processing agreement required under PIPEDA?
No, PIPEDA doesn't require a data processing agreement by name. It requires you to protect transferred data by contractual or other means, and a written processing agreement is the usual way to do that. It isn't a prescribed instrument the way a GDPR data processing agreement is, so the substance matters more than the label.
Do provincial laws add cross-border rules that PIPEDA doesn't?
Yes, Quebec, Alberta, and Nova Scotia's public-sector law all add cross-border rules PIPEDA doesn't. Quebec's Law 25 requires a privacy impact assessment before you send personal information outside the province, and Alberta's PIPA requires you to notify individuals when a service provider is outside Canada. Nova Scotia still requires public bodies to keep data in Canada. A business caught by one of these follows it on top of PIPEDA.
Does a real estate brokerage have to follow PIPEDA when it shares client information across a border?
Yes, a brokerage handling client information commercially falls under PIPEDA, and in Ontario that holds even if the data never leaves the province, since Ontario has no private-sector privacy law. Sending client files abroad for processing doesn't require extra consent, though the brokerage remains accountable and must tell clients about it.
Osman Husain
Osman is the content lead at Enzuzo. He has a background in data privacy management via a two-year role at ExpressVPN and extensive freelance work with cybersecurity and blockchain companies. Osman also holds an MBA from the Toronto Metropolitan University.
LinkedIn →More related blogs
Your next read