Cookie Banner Requirements by Country: EU, UK, US, and Canada (2026)
Osman Husain
Last verified: October 2026.
Cookie banner requirements are the rules that determine whether a website must ask before storing non-essential cookies, how it must offer the choice, and what happens after the user responds.
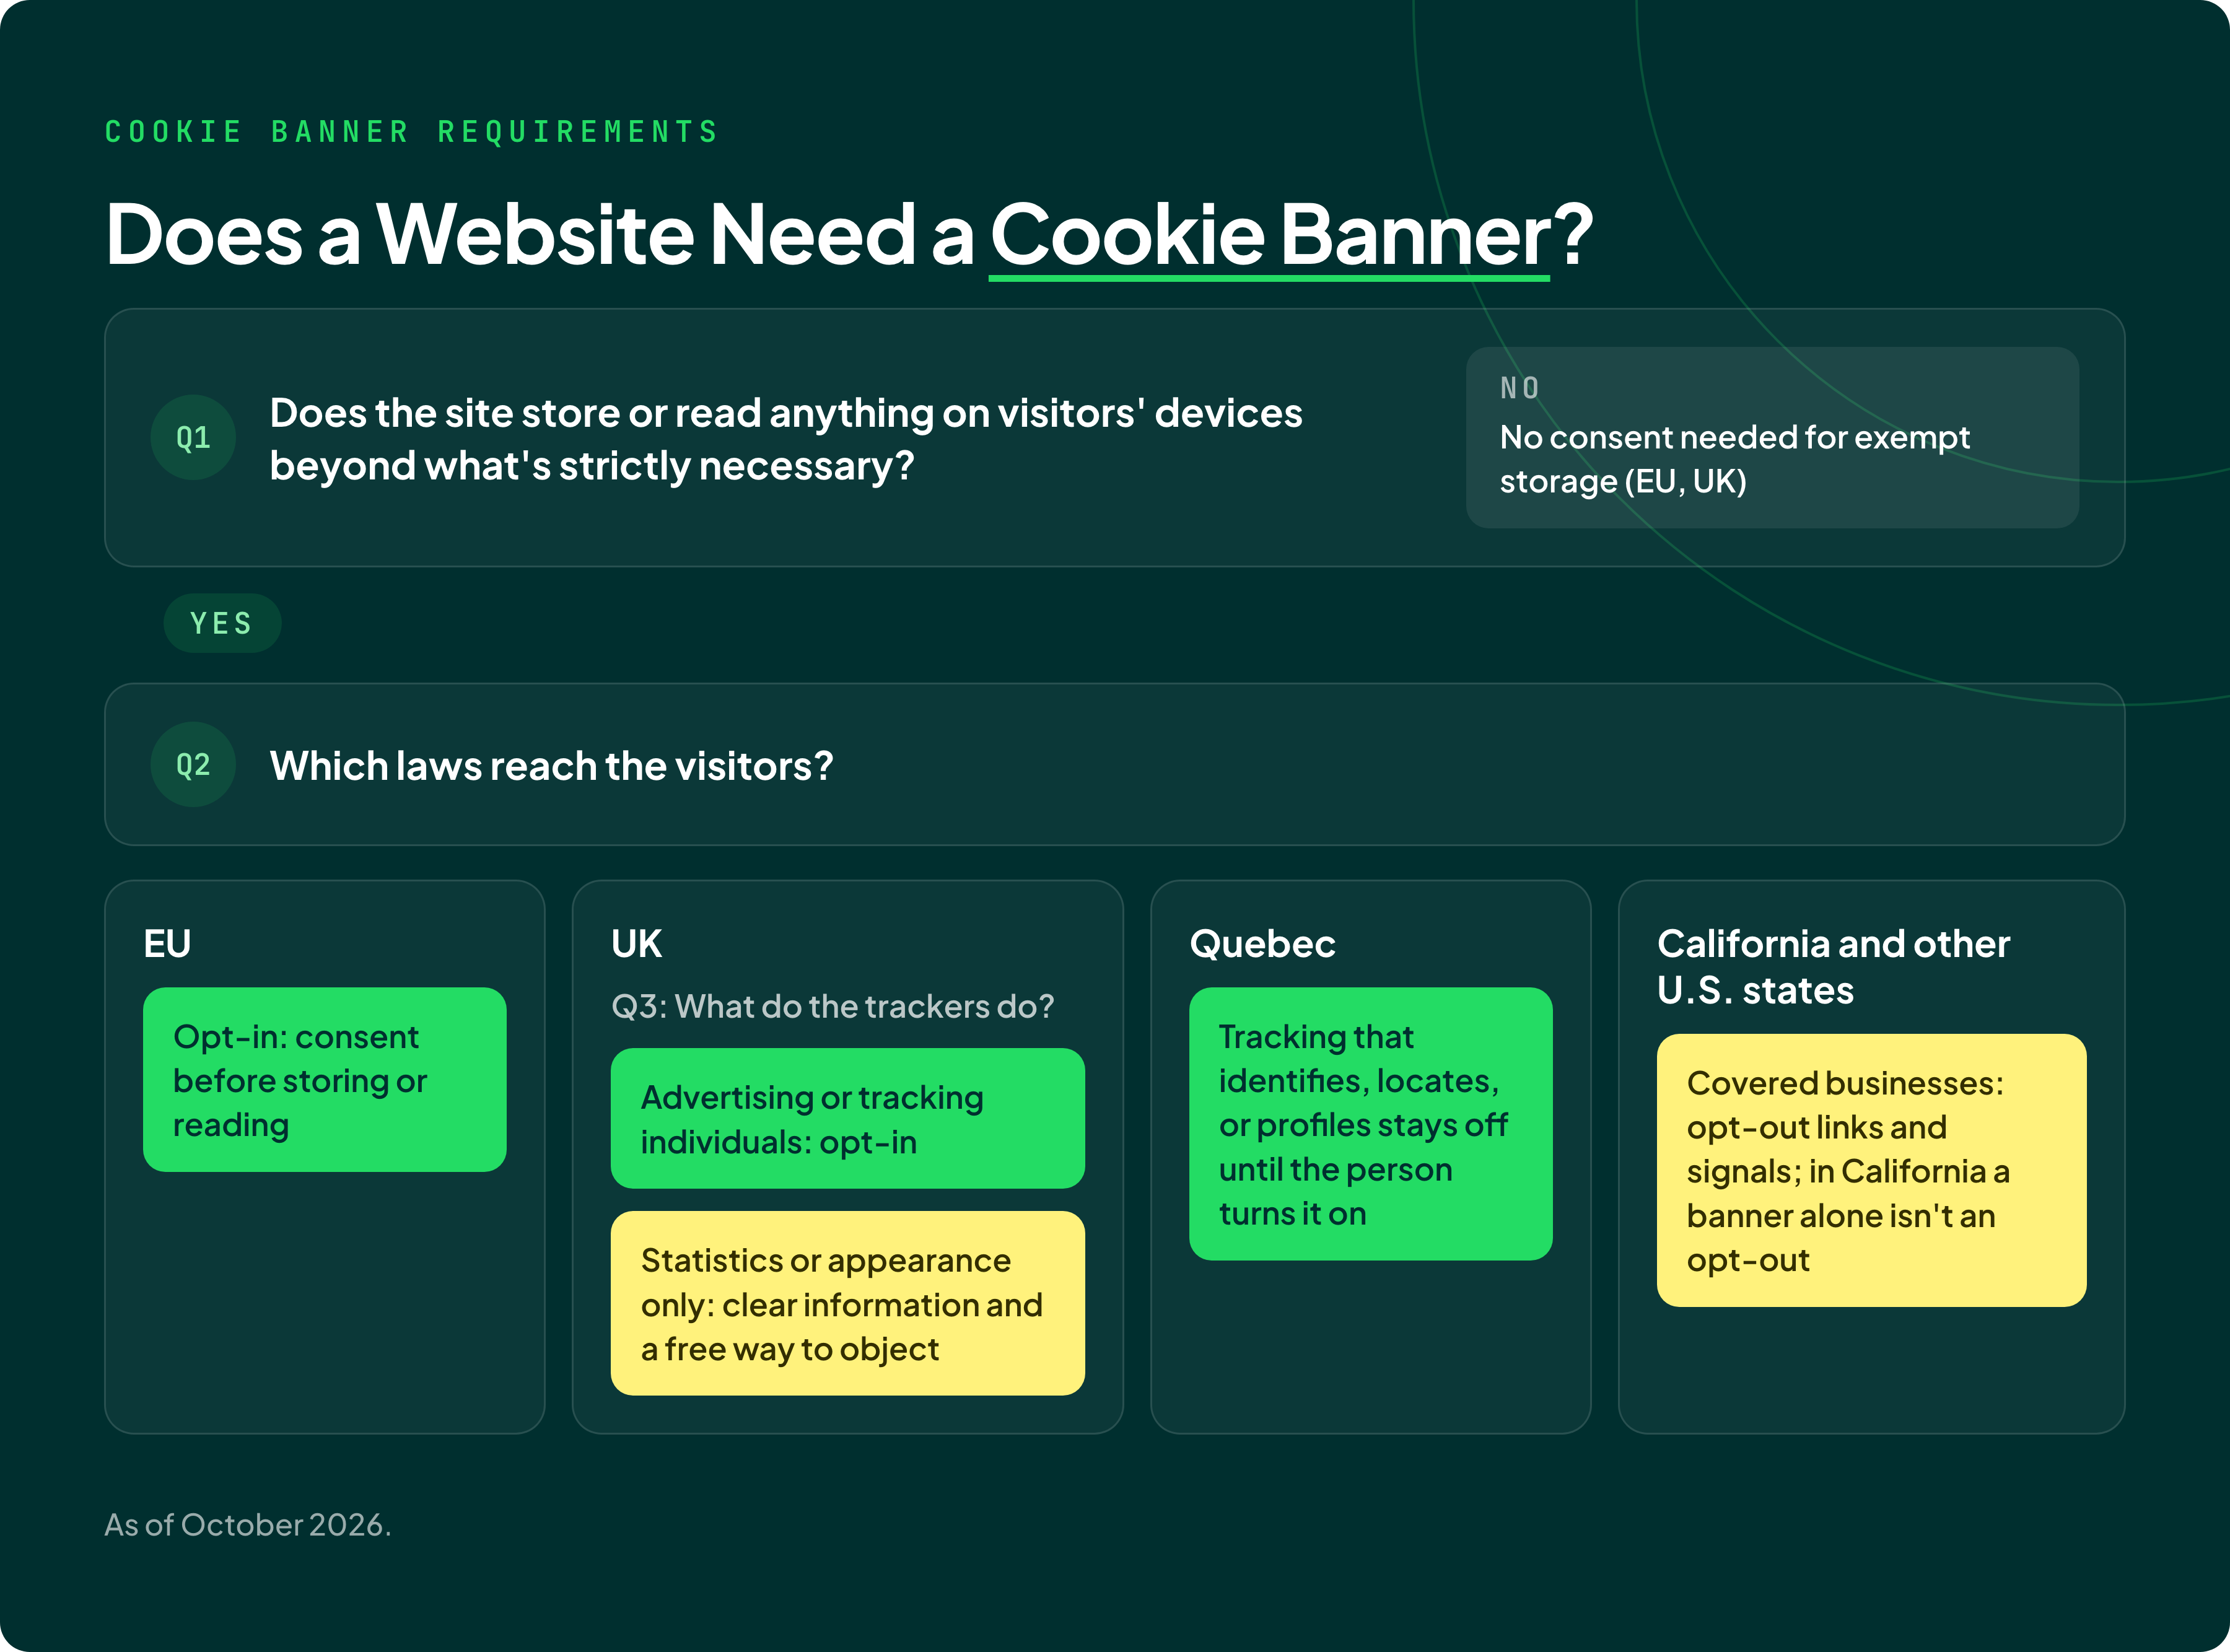
In the EU, UK, and Quebec, tracking waits for opt-in consent, with a UK exception for statistics cookies. U.S. states use opt-out models, and California's regulations say a banner alone isn't an acceptable opt-out for covered businesses.
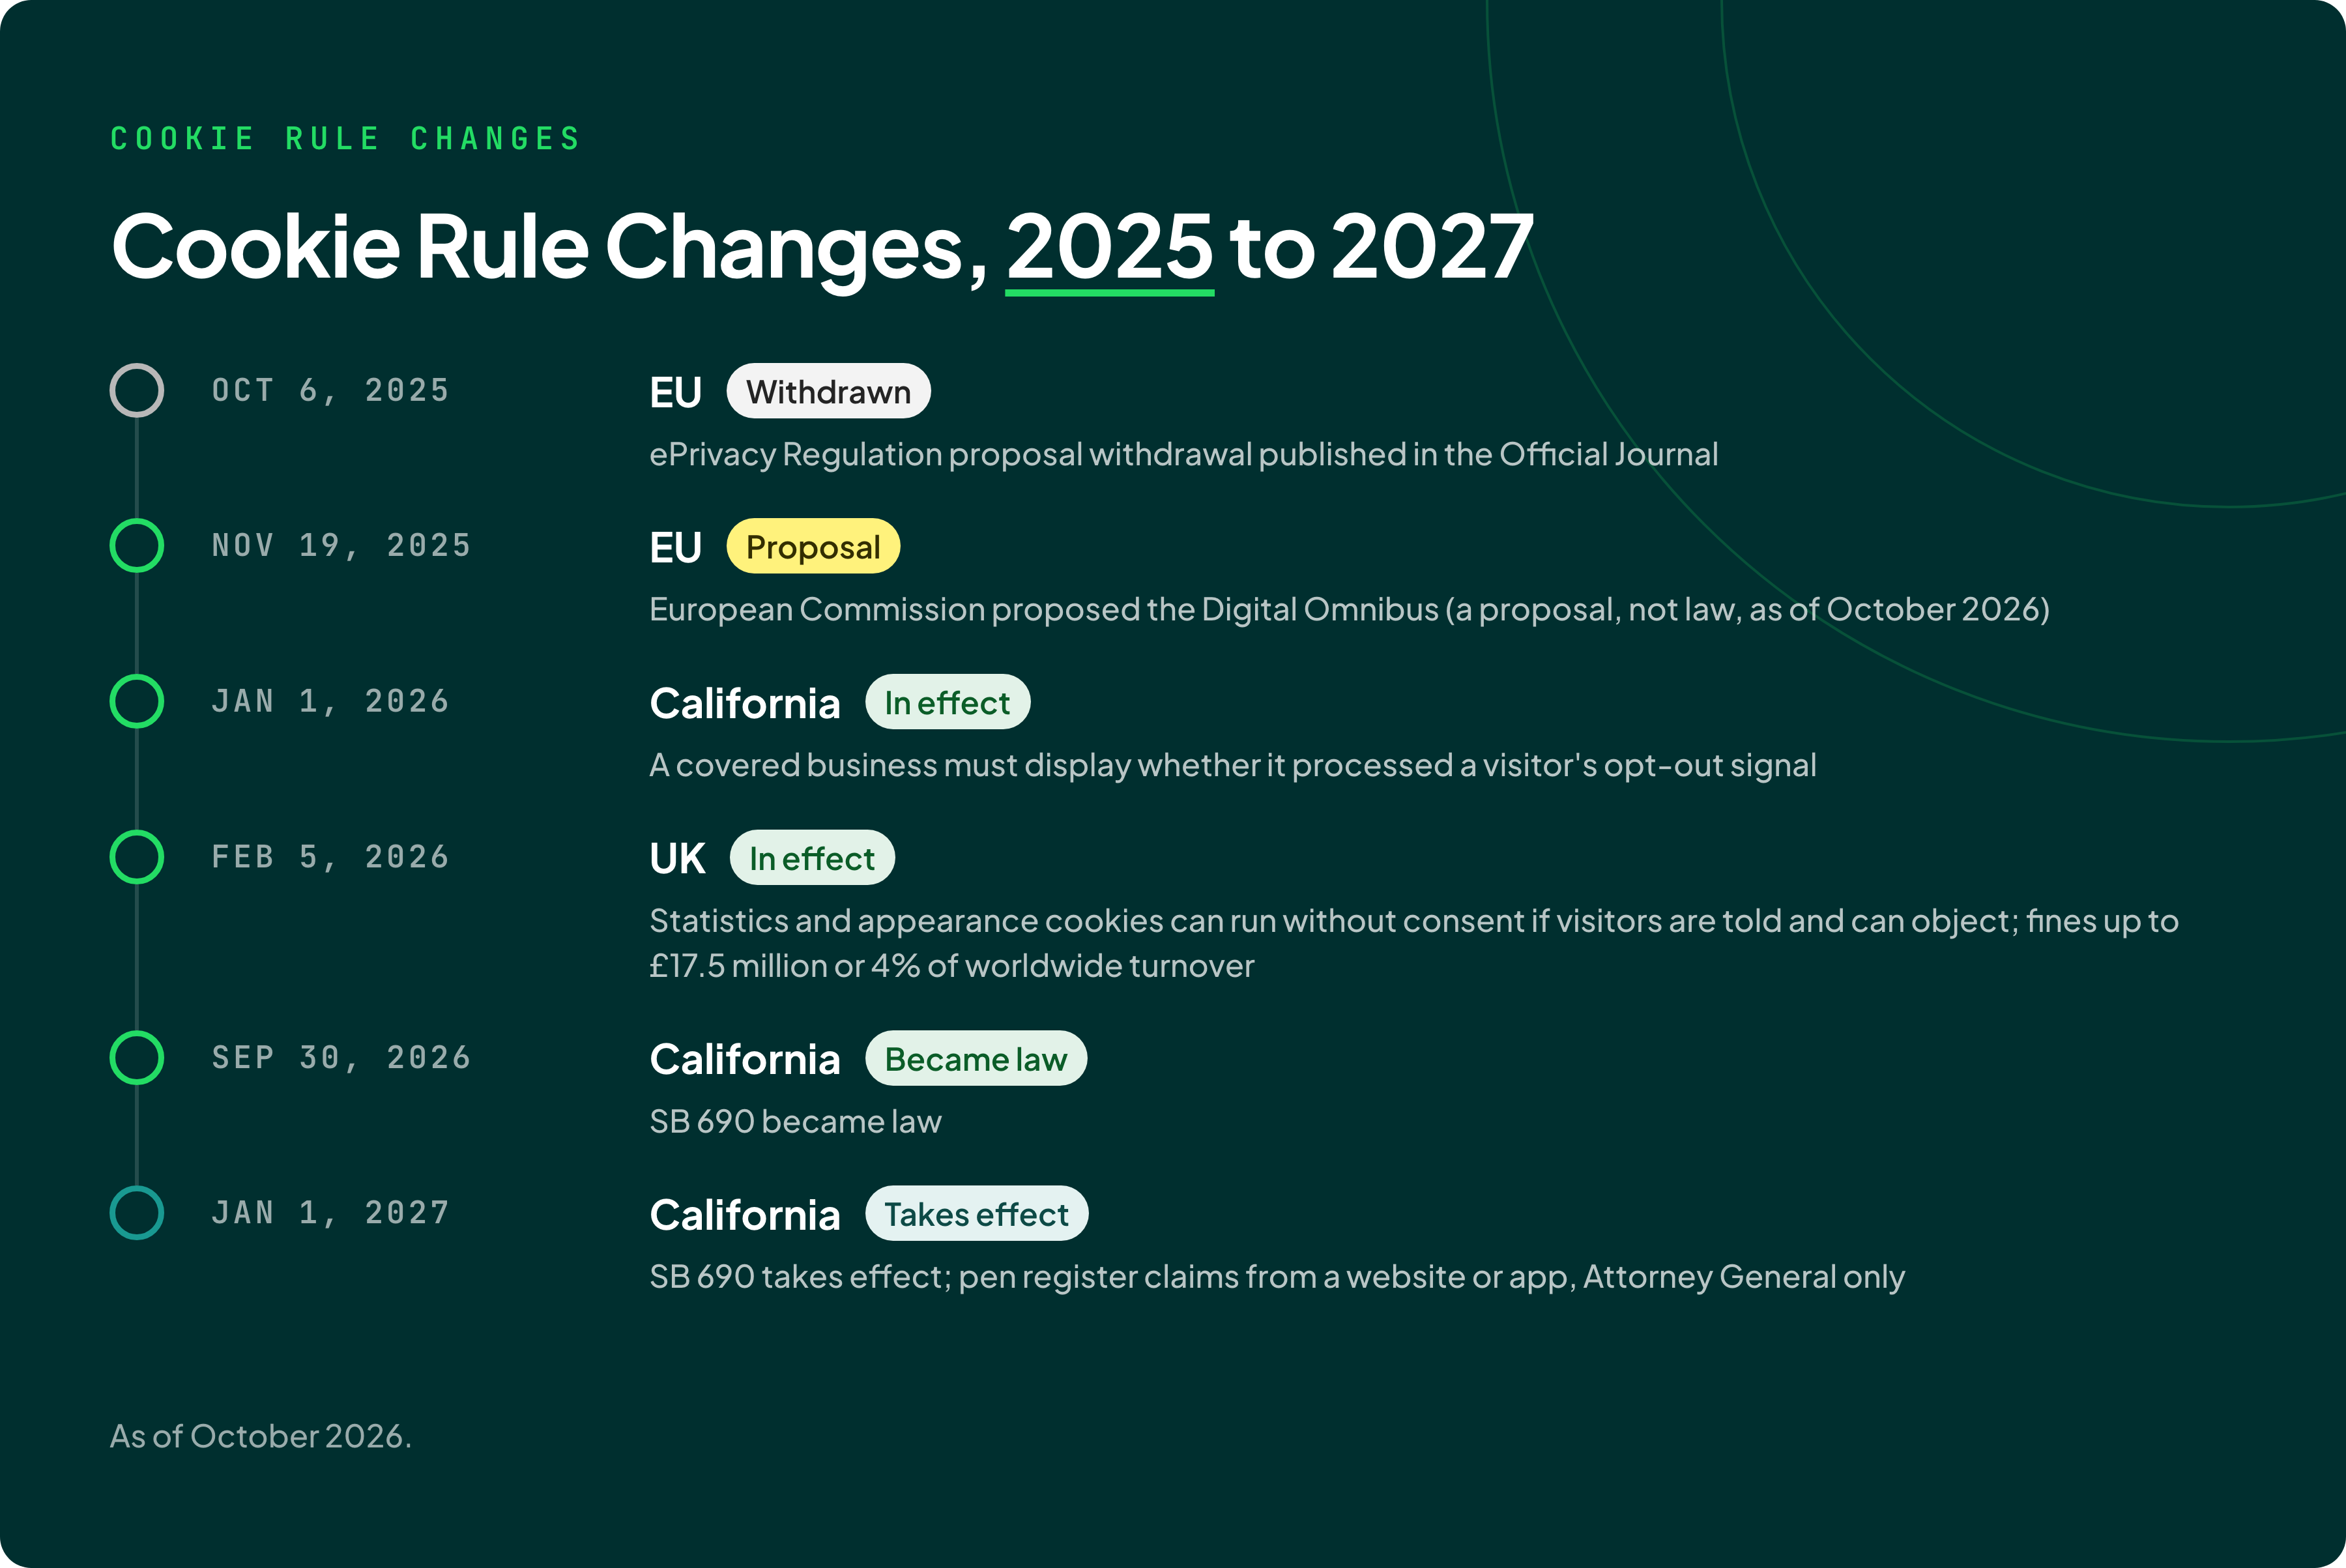
The UK and California both changed their cookie rules in 2026. Since February 5, UK law has let statistics (analytics) and appearance cookies run without consent if visitors are told and can object. UK cookie fines can now reach £17.5 million or 4% of worldwide turnover. Since January 1, 2026, businesses in California must show whether they honored a browser's opt-out signal.
A cookie banner is the most visible part of consent management, the wider work of collecting, recording, and honoring people's choices about their data.
Does a website need a cookie banner?
A website needs a cookie banner in the EU and the UK when it stores or reads information on visitors' devices that no exemption covers. In the U.S., California's CCPA works through opt-out links and browser signals for covered businesses. Three things decide it: what the site stores or reads, which laws reach its visitors, and what each tracker does.
In the EU, consent comes before a site stores or reads information on a device, whether or not that information is personal data. The ePrivacy Directive exempts two cases: storage used only to transmit a communication, and storage strictly necessary for a service the visitor explicitly asked for.
The EU's Digital Omnibus would rewrite the EU cookie rule too, but as of October 2026 it's a proposal, not law yet.
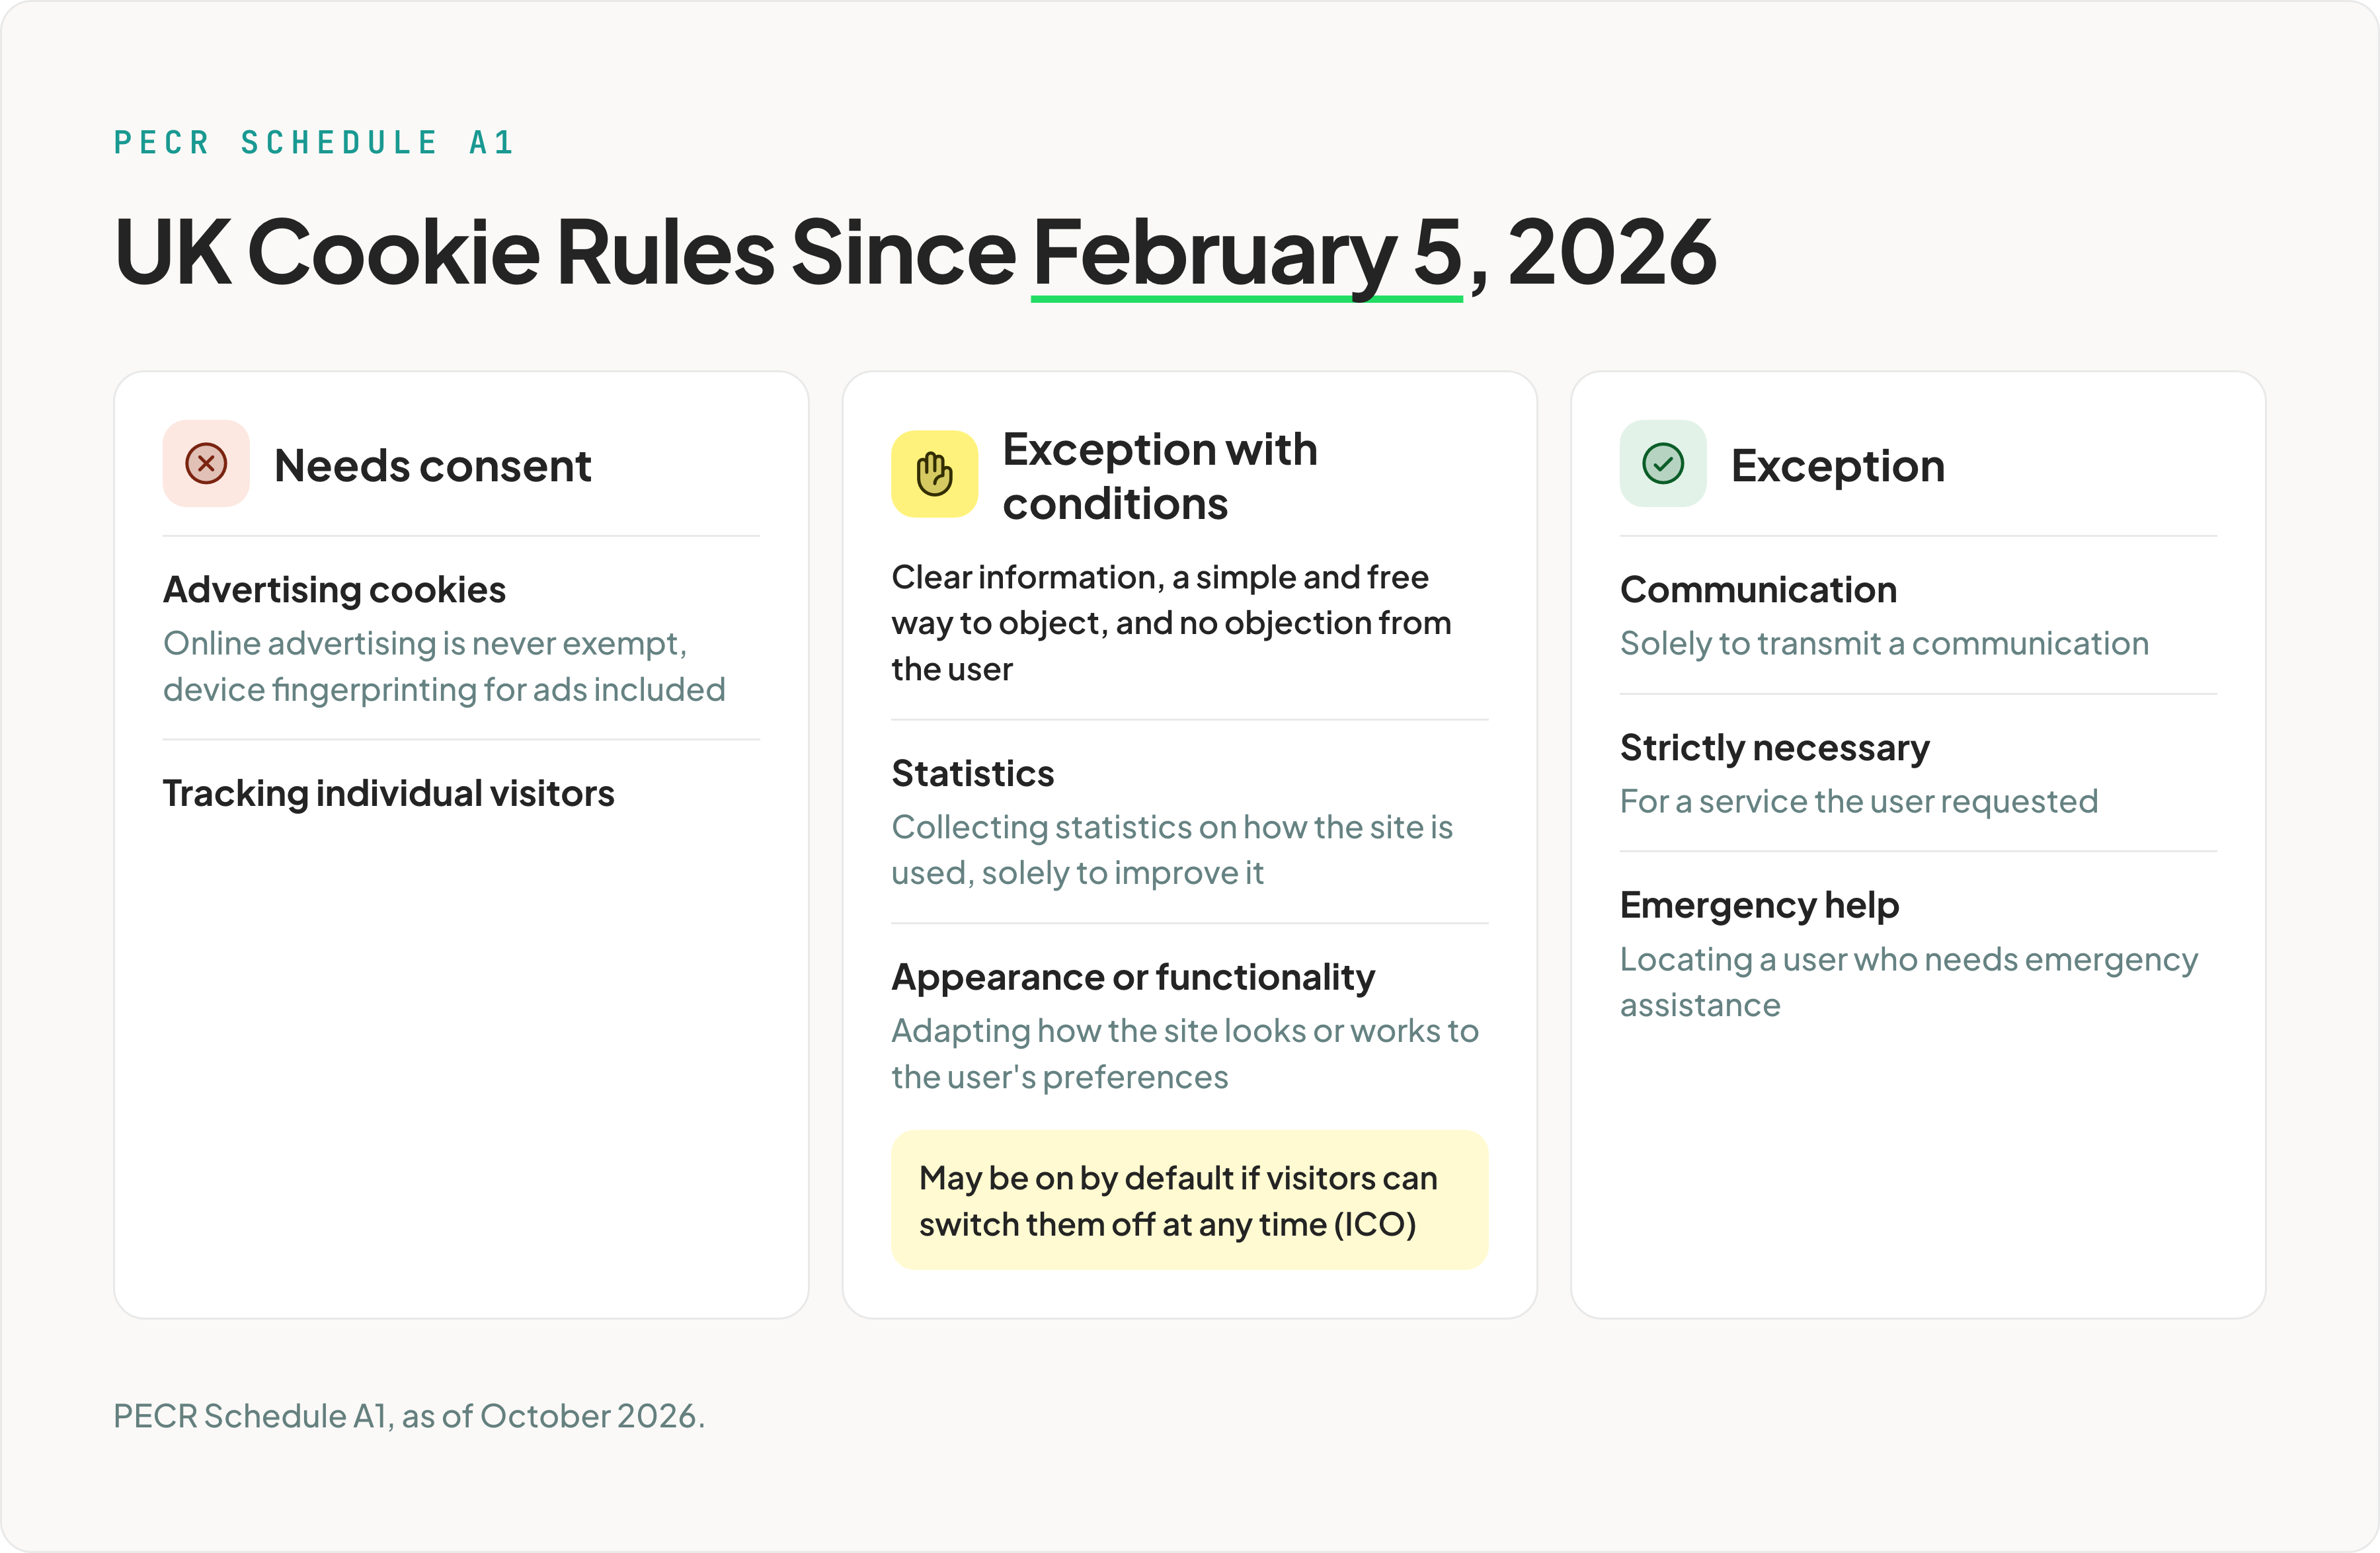
Since February 5, 2026, UK law allows storing or accessing information on a device only with consent or under one of five exceptions: communication, strictly necessary storage, statistics, appearance or functionality, and emergency help.
In the U.S., wiretap law gives sites a separate reason to ask first. California's Invasion of Privacy Act requires the consent of all parties to a communication and has no business-size threshold.
In Canada, consent for tracking comes from PIPEDA and Quebec's Law 25, not from the anti-spam law. Australia's Privacy Act has no cookie-specific consent requirement at all. Working out which exemption applies starts with sorting a site's cookies by purpose, as the cookie categories guide explains.
Cookie banner requirements by country
Cookie banner requirements vary by country. Opt-in rules such as the EU's keep tracking off until the visitor agrees explicitly. Opt-out rules such as California's let it run until the visitor objects. Canada's federal law and the laws of Brazil and Australia tie the answer to sensitivity, legal basis, or notice rather than to a cookie-specific rule.
| Jurisdiction | Law and guidance | Model | Reject option | What the banner or link must do | Exemptions | Maximum penalty |
|---|---|---|---|---|---|---|
| EU | ePrivacy Article 5(3) as each country adopts it, with the GDPR definition of consent | Opt-in | A refuse option on any layer with an accept button, for most EDPB taskforce authorities; France rejects second-layer-only refusal | Clear information on purposes, then consent before anything non-exempt is stored or read | Transmitting a communication; storage strictly necessary for a service the visitor requested | Set by each country; France: up to €10M or 2% of worldwide turnover for a breach of Article 82; GDPR breaches: €20M or 4% |
| UK | PECR regulation 6 and Schedule A1 since February 5, 2026, plus ICO guidance | Opt-in; objection-based for statistics and appearance cookies | Refusing as easy as accepting | Clear information and consent before non-exempt storage; a free way to object to statistics and appearance cookies | Communication, strictly necessary, statistics, appearance or functionality, emergency help | £17.5M or 4% of worldwide turnover under section 157 of the DPA 2018, for breaches from February 5, 2026 |
| California | CCPA and CCPA regulations | Opt-out of sale and sharing; opt-in for known under-16s | Where consent is sought, the privacy-protective choice can't be harder to reach | A Do Not Sell or Share link or one alternative link; GPC honored and, since January 1, 2026, shown as processed | Applies only to businesses over the CCPA thresholds | $2,663 per violation and $7,988 if intentional, under the 2025 adjustment; next change January 1, 2027 |
| Other U.S. states | 18 more comprehensive laws in effect, such as Virginia's and Colorado's | Opt-out; consent for sensitive data in most states | The right to opt out of targeted ads and sale (Iowa: sale only) | Opt-outs honored; in some states a universal opt-out signal too, as the GPC guide lists | Thresholds vary, such as Connecticut's 35,000 consumers since July 1, 2026 | Set by each state law |
| Canada (federal) | PIPEDA and OPC guidance | Consent in a form set by sensitivity; opt-out accepted for behavioural ads under conditions | An easy opt-out for behavioural ads, ideally at or before collection | Behavioural ads explained at or before collection, not buried in a privacy policy | Consent exceptions listed in the Act | No administrative fines today; offence fines up to $100,000 don't cover consent failures |
| Quebec | Law 25, sections 8.1 and 14, plus CAI guidelines | Tracking that can identify, locate, or profile stays off until the person turns it on | Giving consent must be as easy as not giving it | Notice of the technology and how to turn it on; a request for each purpose in clear, simple language | Section 8.1 applies to functions that identify, locate, or profile | Up to $10M or 2% of worldwide turnover; penal fines up to $25M or 4% |
| Brazil | LGPD and the ANPD cookie guide | Consent is one of ten legal bases | The ANPD recommends a reject-all button on both layers | Clear information on purposes and retention; free, easy withdrawal | Consent isn't the right basis for strictly necessary cookies, per the ANPD | 2% of revenue in Brazil, capped at R$50M per infraction |
| Australia | Privacy Act and OAIC guidance | Notice, with no cookie consent rule; consent for sensitive information | A simple opt-out from direct marketing, ad targeting included | A collection notice at or before the time of collection | Most small businesses with turnover of A$3M or less | Up to A$50M, three times the benefit, or 30% of adjusted turnover, a tier set in 2022 |
The penalty column shows legal ceilings, not typical fines. Cookie banner fines show what regulators have actually imposed over the years.
GDPR cookie consent requirements in the EU
GDPR cookie consent rules come from the ePrivacy Directive, which borrows the GDPR's definition of consent. Its Article 5(3) allows storing or reading information on a device only with consent, given after clear and comprehensive information about the purposes. Each member state writes the rule into national law, as France did in Article 82 of its data protection act.
Under the GDPR definition, valid consent is freely given, specific, informed, and unambiguous. It takes a statement or a clear affirmative action, so silence, pre-ticked boxes, and inactivity don't count. Consent isn't free if refusing or withdrawing it leaves the visitor disadvantaged such as a poor website experience. Withdrawing must be as easy as giving it.
The European Data Protection Board (EDPB) guidelines say a cookie wall, which makes access to a site conditional on accepting cookies, is against the spirit of the law. France's CNIL assesses them case by case, while Italy's Garante treats one as unlawful unless the site offers an equivalent alternative without consent.
The EU's top court applied the consent rules to cookies in Planet49, saying that a pre-checked box visitors must untick isn't valid consent. Visitors must also be told how long cookies operate and whether third parties can access them.
Legitimate interest can't replace consent. The EDPB's cookie banner taskforce says that basis can't be used to place or read cookies under Article 5(3).
Article 5(3) also reaches beyond cookies. The EDPB's technical scope guidelines cover tracking pixels and tracking links, even when storage is only temporary.
The guidelines also cover unique identifiers collected through client-side code, and information computed on the device and sent to a server. Tracking by IP address alone can fall under the rule when the address comes from the visitor's device, though not every case does.
Breaches of Article 5(3) are fined under national law, because the ePrivacy Directive leaves penalties to each member state. In France, the CNIL can fine up to €10 million or 2% of worldwide annual turnover for a cookie breach under its data protection act.
EU cookie banner visual requirements
The EDPB's taskforce says banners without a refuse option are an infringement of its guidelines. Each country in the EU has its own requirements since the EDPB doesn't enforce a specific rule rather publishes broad advice which member countries can follow.
The EDPB says a refuse option shown only as a link inside a paragraph, or outside the banner without enough visual support, doesn't lead to valid consent. A reject button designed around dark patterns is also misleading.
France's CNIL expects a refuse-all button at the same level as accept-all, or another way to refuse as easily. It rejects refusal offered only on a second layer.
Italy's Garante gives the banner's X a legal meaning. Closing the banner with it keeps the default settings, so browsing continues with technical cookies only.
What the EU's Digital Omnibus proposal would change
The Digital Omnibus would move EU cookie rules for personal data into the GDPR. The European Commission proposed it on November 19, 2025, with a new GDPR Article 88a that would switch off ePrivacy Article 5(3) for those cases. As proposed, the Omnibus would:
- add consent exemptions for first-party aggregated audience measurement for the site's own use, and for security
- require refusal by a single click or an equivalent
- stop a site from asking again for the same purpose for at least six months after a refusal
- make sites accept consent and refusal sent as automated, machine-readable signals, 24 months after the law enters into force
EU lawmakers haven't agreed on the Omnibus. As of October 11, 2026, the European Parliament's joint ITRE and LIBE committees hadn't voted, according to the Legislative Train. The Council of member-state governments had no negotiating mandate after a June 26 vote was cancelled. The item went to an October 11 Coreper meeting of member-state ambassadors, with no published outcome that day.
The older ePrivacy Regulation proposal is gone: its withdrawal was published in the Official Journal on October 6, 2025.
UK cookie banner requirements after the Data (Use and Access) Act
UK cookie banner requirements changed on February 5, 2026, the start date set by the commencement regulations. That day, section 112 of the Data (Use and Access) Act replaced regulation 6 of the Privacy and Electronic Communications Regulations (PECR).
The new regulation 6 bans storing or accessing information on a user's device unless the user consents or an exception applies. It also covers collecting information a device emits on its own, which includes fingerprinting. Consent under PECR's Schedule A1 means the user gets clear and comprehensive information before a choice is made.
Schedule A1 lists five exceptions for cookies firing before consent. The ICO, the UK's data protection regulator, confirms there are no others:
- Communication: storage or access solely to transmit a communication.
- Strictly necessary: storage or access strictly necessary for a service the user requested, such as security, fraud prevention, fault detection, automatic sign-in, or remembering what the user selected or entered.
- Statistics: collecting statistics on how the site is used, solely to improve it, with the data shared only to help with those improvements.
- Appearance or functionality: adapting how the site looks or works to the user's preferences, or otherwise enhancing it.
- Emergency help: locating a user who has asked for or needs emergency assistance.
The statistics and appearance exceptions carry conditions: clear information, a simple and free way to object, and no objection from the user. The ICO says these cookies may be on by default if visitors can switch them off at any time. It adds that browser settings alone aren't a reliable objection signal.
Advertising cookies still need consent in the UK. The ICO says online advertising is never exempt, device fingerprinting for ads included, and the statistics exception doesn't cover tracking individual visitors.
The ICO's final guidance, published April 29, 2026, says refusing must be as easy as accepting. Its examples give accept all and reject all equal prominence. Continuing to use a site isn't consent, pre-ticked boxes aren't consent, and non-exempt technologies mustn't be pre-enabled.
Withdrawing must be as easy as giving consent. After a refusal, the ICO's general guideline is to wait about six months before asking again, unless the purposes change.
UK cookie fines now match GDPR levels. The Act's Schedule 13 moved PECR enforcement under the Data Protection Act 2018, so a cookie breach carries the higher maximum in section 157. That's £17.5 million or 4% of worldwide annual turnover, whichever is higher. It applies to breaches from February 5, 2026 onwards.
CCPA cookie banner requirements in California
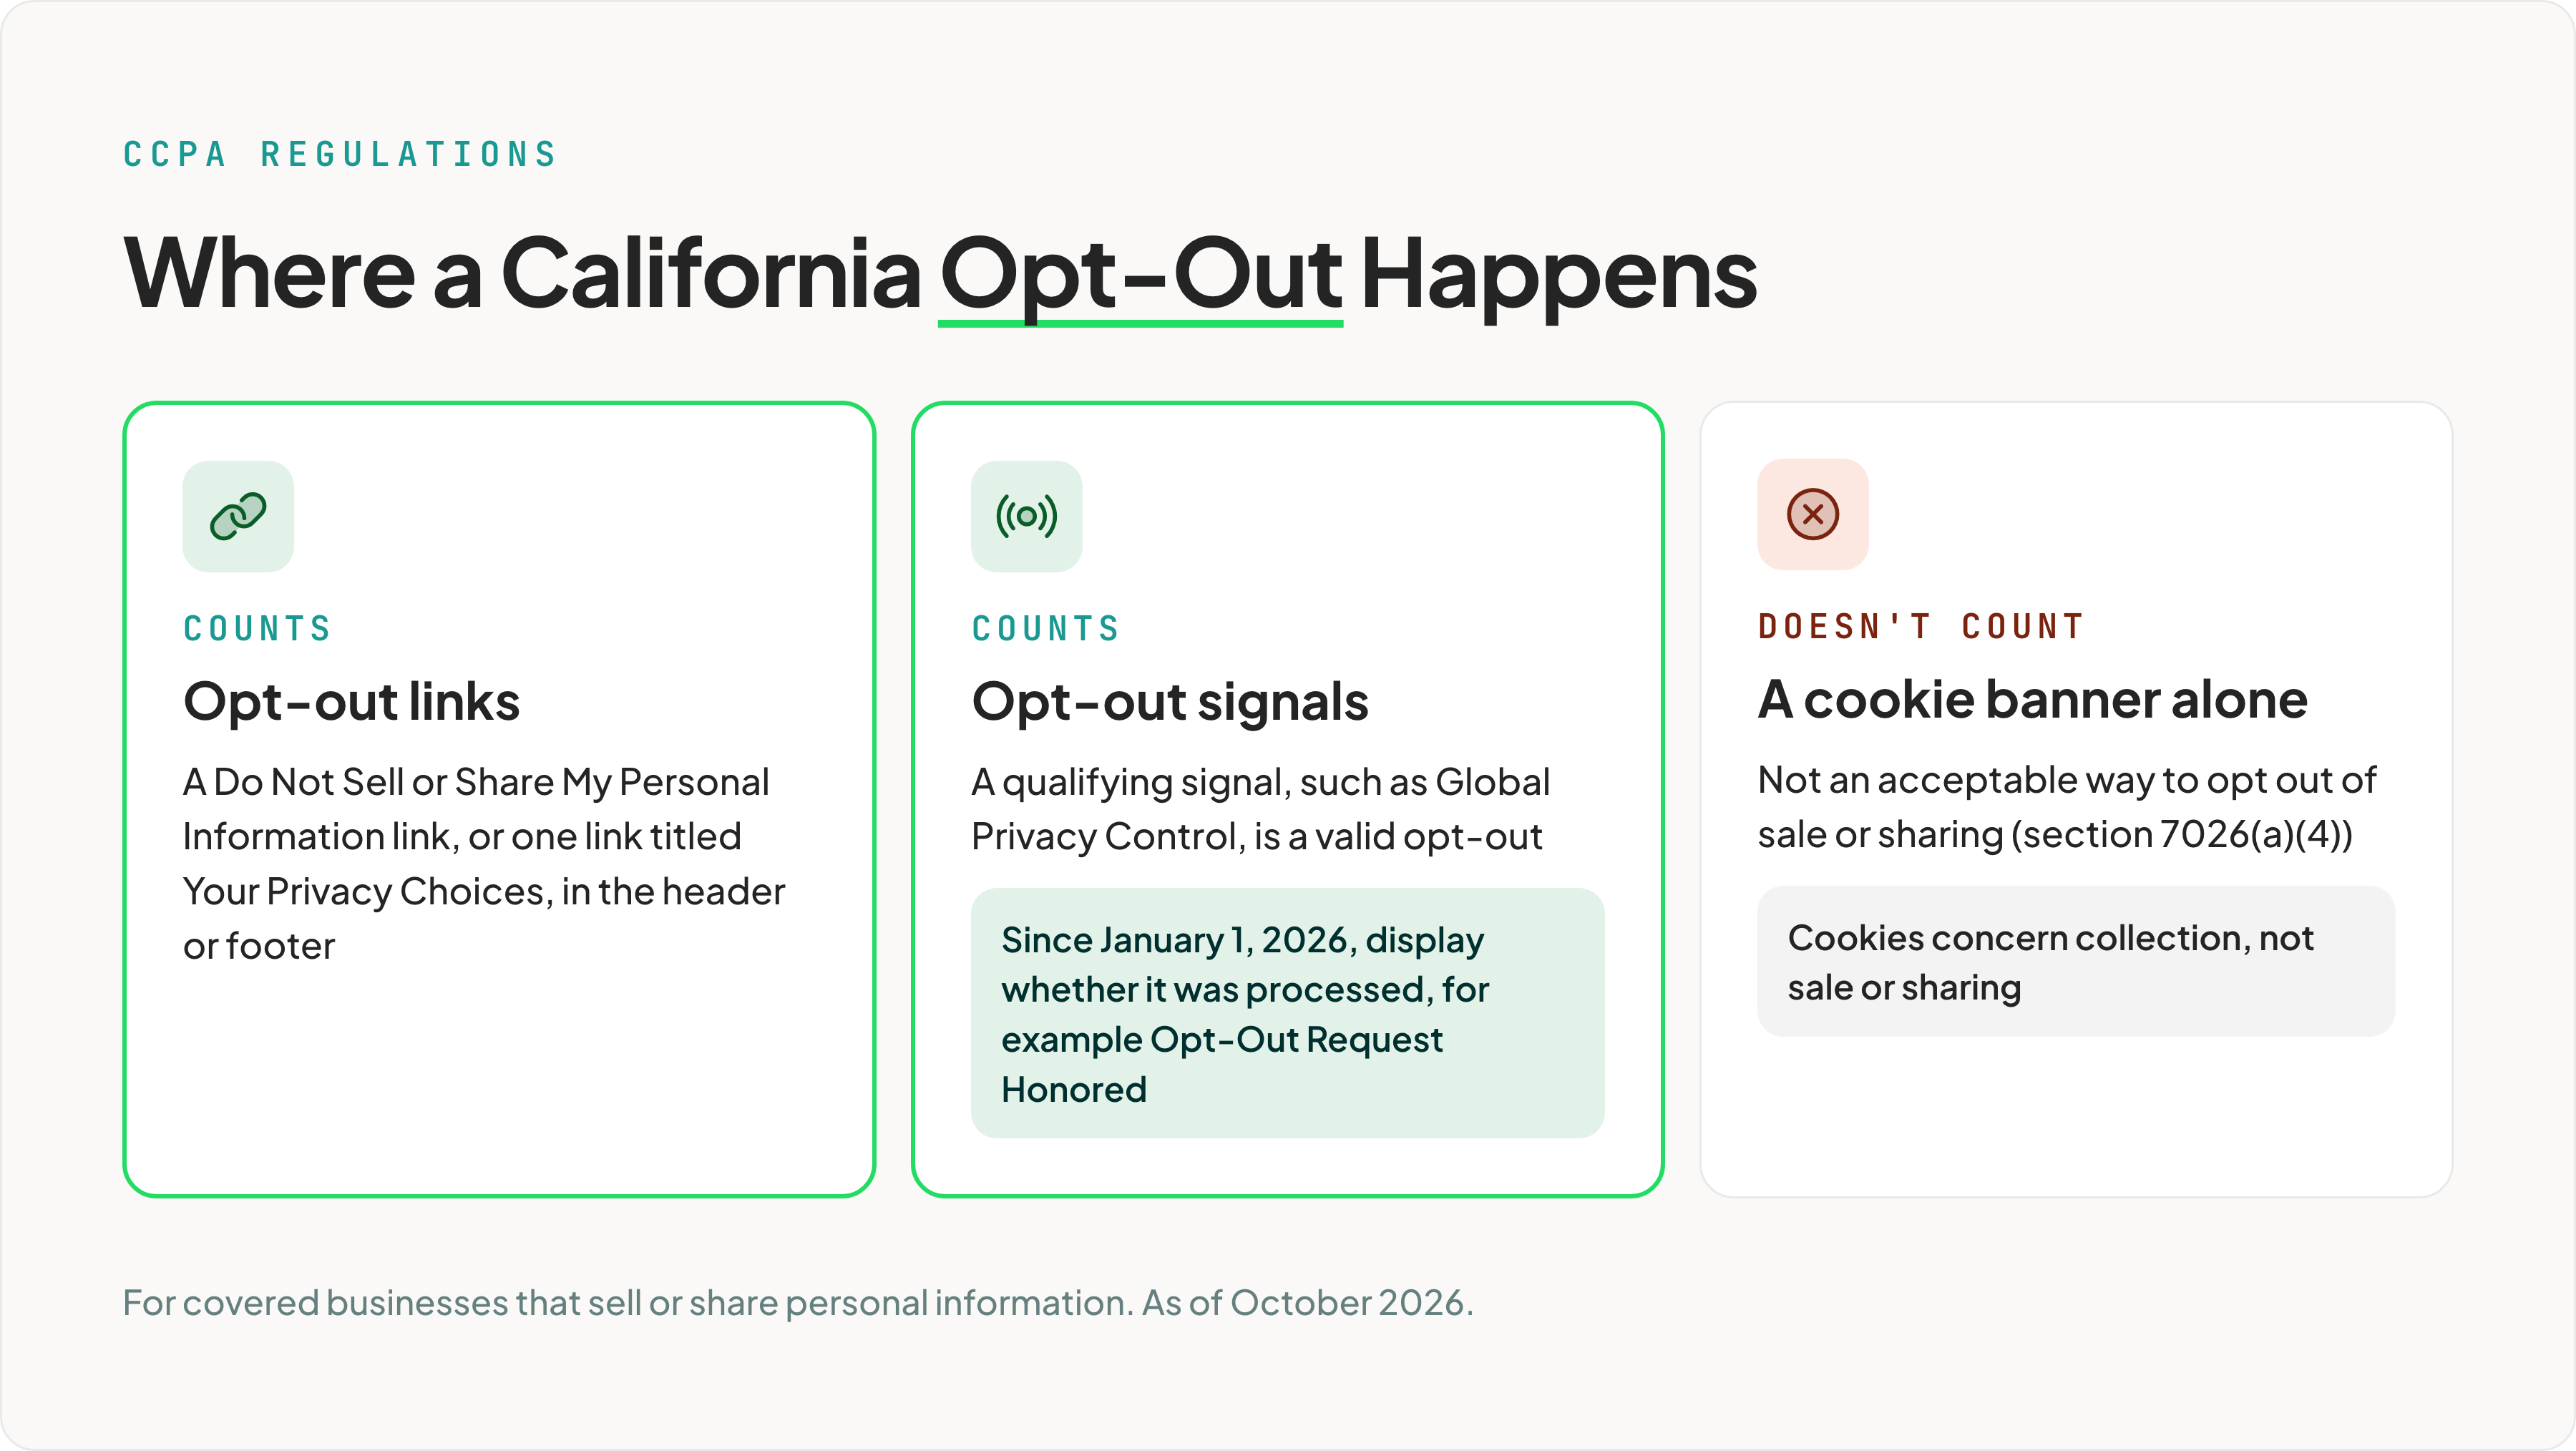
A CCPA cookie banner isn't required by name: the CCPA statute never uses the words cookie banner. It compels businesses that sell or share personal information to let people opt out through links on the site and through browser signals such as Global Privacy Control.
CCPA's definition of personal information includes online identifiers and IP addresses. It also says a unique identifier includes cookies, beacons, and pixel tags. Selling data means giving personal information to a third party for money or other valuable consideration. Sharing data means giving it to a third party for cross-contextual behavioral advertising.
Since cookie identifiers count as personal information, a business that collects them online gives a notice at collection. That can be a conspicuous link on the homepage and on every page that collects data, pointing straight to the relevant section of the privacy policy.
A CCPA business that sells or shares personal information must also post a Do Not Sell or Share My Personal Information link on its homepage. If it uses sensitive data beyond permitted purposes, it needs a Limit the Use of My Sensitive Personal Information link. The regulations require the first link to be conspicuous, included either in the header or footer.
Under section 7026(a)(4) of California's regulations, a cookie banner or cookie controls alone isn't an acceptable way to opt out of sale or sharing. For example, if a resident consents to share data that consent cannot also be used to sell it to a third party.
The Attorney General's Sling TV settlement for $530,000, in October 2025, used this justification.
Browser opt-out signals are the second route businesses must honor in the CCPA. Under section 7025, a business that sells or shares personal information must treat a qualifying signal, such as Global Privacy Control, as a valid opt-out mechanism.
After receiving an opt-out, businesses must stop selling or sharing that person's data as soon as possible, and within a maximum of 15 business days.
Three CPPA orders since 2025 describe banner and opt-out failures:
- American Honda, March 2025: the CPPA fined Honda $632,500 after finding that accepting all took one click while opting out took at least two, and it ordered a Reject All button.
- Todd Snyder, May 2025: the CPPA fined the clothing retailer $345,178. For 40 days, its Cookie Preferences Center link opened a banner that vanished at once, so opt-outs, GPC signals included, went unprocessed.
- PlayOn Sports, February 2026: the CPPA fined it $1,100,000. The order describes notice banners that could only be closed by clicking Agree, opt-outs routed to industry ad groups instead of its own method, and no processing of opt-out signals.
CCPA fines are set per violation. As of 2026, the inflation-adjusted maximums are $2,663 per violation and $7,988 per intentional violation or one involving known minors. They've applied since January 1, 2025. The statute re-adjusts them every odd-numbered year, so the next change is due January 1, 2027.
For the law as a whole, see Enzuzo's CCPA guide.
How CIPA wiretap claims affect California cookie banners
CIPA wiretap claims run on consent capture and storage. Section 631 of the California Invasion of Privacy Act makes it unlawful to read or learn the contents of a communication in transit without the consent of all parties.
Section 638.51 bars using a pen register, a process that records dialing, routing, addressing, or signaling information, without a court order. A person affected can sue for $5,000 per violation or three times actual damages, whichever is greater.
In short, if your California cookie banner does not capture and store consent properly, you may run the risk of a CIPA lawsuit.
Are cookie banners required in other U.S. states?
Other U.S. state privacy laws give people the right to opt out of targeted advertising and the sale of their data, and most require consent before a business processes sensitive data.
| What the law requires | States |
|---|---|
| Opt-out of targeted advertising and sale | All 19 in effect except Iowa, whose rights list gives an opt-out of sale only |
| Consent before processing sensitive data | Virginia, Colorado, Connecticut, Texas, Oregon, Montana, Delaware, Nebraska, New Hampshire, Tennessee, Minnesota, Indiana, Kentucky, Rhode Island; New Jersey under rules its Attorney General proposed in June 2025 |
| Sensitive data without an opt-in | Iowa and Utah (notice and a chance to opt out); California (a right to limit its use); Maryland (sale banned, processing only when strictly necessary) |
| Must honor a universal opt-out signal | California, Colorado, Connecticut, Delaware, Minnesota, Montana, New Hampshire, Oregon, with dates in the GPC guide |
| Signal only through an authorized agent | Texas and Nebraska; Louisiana from January 1, 2027 |
| Link or signal, at the business's choice | Maryland |
| No signal clause | Virginia, Utah, Iowa, Tennessee, Indiana, Kentucky, Rhode Island |
| Starting later | Louisiana and Oklahoma on January 1, 2027; Alabama on May 1, 2027; Vermont on January 1, 2028, with a signal requirement |
Canada: PIPEDA and Quebec Law 25 cookie rules
Canada's federal privacy law, PIPEDA, has no cookie-specific rule. It requires a person's knowledge and consent to collect, use, or disclose personal information, unless an exception applies.
Consent under section 6.1 is valid only if the people a site is aimed at could reasonably understand the nature, purpose, and consequences of what they agree to. PIPEDA expects express consent for information likely to be sensitive and treats implied consent as generally appropriate for less sensitive information. People can withdraw consent at any time, subject to legal or contractual limits and reasonable notice.
Canada's privacy commissioners say in their meaningful consent guidelines that express consent is generally required when information is sensitive or a use falls outside reasonable expectations. People must get a real choice for anything beyond what a product or service needs.
The Office of the Privacy Commissioner (OPC) gets specific about trackers in its advertising guidelines. They treat data gathered for targeted ads as personal information in most cases, and accept opt-out consent for it only under conditions. The guidelines say:
- People are told about the advertising, and the parties involved, at or before collection, through tools such as banners or layered notices, not buried in a privacy policy.
- The opt-out is easy, takes effect immediately, and persists.
- The data stays non-sensitive as far as practicable and is destroyed or de-identified as soon as possible.
- Tracking people can't decline, such as zombie cookies, super cookies, and device fingerprinting, isn't used for behavioural ads.
Canada's anti-spam law, CASL, treats a person as having expressly consented to cookies, HTML code, and JavaScript when their conduct makes that reasonable. It governs installing software on computers, not collecting personal information, so PIPEDA and Quebec law still decide whether tracking needs consent.
PIPEDA has no administrative fines today. Its fines, up to $100,000, cover only specific offences such as obstructing the Commissioner or failing to report breaches, not consent failures.
How Quebec's Law 25 treats tracking cookies
Under Quebec's Law 25, tracking that can identify, locate, or profile a person must stay off until consent is received.
Section 8.1 requires a business collecting personal information to first inform visitors before capturing consent choices.
Quebec's privacy regulator publishes consent guidelines. It requires tech products with privacy settings to default to the highest level of confidentiality, but it expressly excludes browser cookie settings.
Consent in Quebec must be clear, free, and informed, and given for specific purposes, under section 14. It must be requested for each purpose in clear and simple language, and a written request must stand apart from other information. Consent that misses these conditions has no effect. Express consent is required only for sensitive personal information.
Under the CAI's Guidelines 2023-1, published October 31, 2023, giving consent must be as easy as not giving it. Highlighting accept over refuse through colour, font size, extra clicks, or misleading wording can leave consent without effect. And a pre-ticked box counts as implied consent, not express consent.
Sections 8.1, 9.1, and 14 took effect on September 22, 2023. Quebec's regulator can impose administrative penalties of up to $10 million or 2% of worldwide turnover. Penal fines for businesses run from $15,000 to $25 million, or 4% of worldwide turnover if greater.
Cookie banner rules in Brazil and Australia
Brazil's regulator recommends a reject-all button and consent-based cookies off by default, while Australia's Privacy Act has no cookie consent rule at all.
Brazil's data protection law, the LGPD, defines consent as a free, informed, and unequivocal expression of agreement for a specific purpose, and makes it one of ten legal bases. People can revoke it at any time through a free and easy procedure, and processing based on flawed consent is prohibited.
The LGPD has no cookie article. Brazil's regulator, now officially the National Data Protection Agency (ANPD), covers cookies in a 2022 guide published under its earlier name. The guide recommends:
- an easy-to-see button to reject all non-necessary cookies on both the first and second layers
- cookies that rely on consent switched off by default
- no pre-selected boxes, and no treating continued browsing as consent
The guide names a banner with a single I agree button and no way to manage choices as a practice to avoid. Consent isn't the right basis for strictly necessary cookies, it says, but it's the more appropriate basis for advertising cookies. LGPD fines can reach 2% of a company's revenue in Brazil, capped at R$50 million per infraction.
Businesses covered by Australia's Privacy Act must tell people about a collection at or before the time it happens. They need consent for sensitive information and must offer an easy opt-out from direct marketing. Most small businesses with annual turnover of A$3 million or less are outside the Act.
The tracking pixels guidance from the Office of the Australian Information Commissioner (OAIC) is the closest Australian equivalent to cookie guidance. It says an IP address collected by a pixel can identify someone when matched with other information. Using pixels to target ads triggers the direct-marketing opt-out, and sensitive data sent through pixels generally needs express opt-in consent.
What a compliant cookie banner looks like
A compliant cookie banner in the EU, the UK, and Quebec blocks non-essential cookies until the visitor chooses. It makes refusing as easy as accepting and explains each purpose first. In California, the opt-out link and signal handling carry the legal weight, since a banner alone isn't an acceptable opt-out there.
| Requirement | EU | UK | California | Quebec |
|---|---|---|---|---|
| Cookies that need consent wait for a choice | Required: consent comes first under Article 5(3) | Required: non-exempt technologies mustn't be pre-enabled | Not required for ordinary ad cookies; opt-in for known under-16s | Tracking functions off by default until the person turns them on |
| Refusing as easy as accepting | A refuse option on any layer with an accept button, for most authorities in the EDPB taskforce | Refusing as easy as accepting | Where consent is sought, the privacy-protective path can't be harder | Consenting as easy as not consenting |
| Accept and reject get equal weight | France: two buttons at the same level and in the same format; an unreadable reject button is manifestly misleading | ICO good-practice examples show equal prominence | A bigger or brighter yes button isn't symmetrical | Highlighting accept over refuse can void consent |
| Silence, pre-ticked boxes, and scrolling aren't consent | Planet49 rules out pre-checked boxes; scrolling never counts | Continuing to use a site and pre-ticked boxes aren't consent | Closing or navigating away from a consent pop-up isn't consent | A pre-ticked box is implied consent; turning tracking on takes a positive act |
| Purposes explained before the choice | Clear information on purposes, how long cookies run, and third-party access | Clear and comprehensive information | A notice at collection linked where data is collected | Each purpose in clear, simple language |
| Withdrawing as easy as agreeing | Withdrawal as easy as consent | Withdrawal with the same ease | Opt-out at any time | Equal clicks to consent or refuse in the CAI's withdrawal example |
| Opt-out signals such as GPC | Not required; the Digital Omnibus proposes signals | Consent may be signalled through browser settings; the ICO says not to rely on them alone for objections | Must be honored and, since January 1, 2026, shown as processed | Not required |
| Do Not Sell or Share link, or the alternative opt-out link | Not required | Not required | Required for covered businesses that sell or share personal information | Not required |
The EU and Brazil both put the burden of proof on the site. Under the GDPR, a site relying on consent must be able to prove it was given. Brazil's LGPD puts the burden of proving lawful consent on the controller, the party that decides how the data is processed.
Regulator guidance in Europe sets how long a cookie refusal should stand, with each wording it differently. France's CNIL treats keeping a visitor's choice for six months as good practice, not a legal maximum.
California says a business must wait at least 12 months before re-requesting consent.
How Enzuzo's cookie banner handles these rules
Enzuzo's cookie banner can apply a different rule in each region. Starting on the Growth plan, Enzuzo can set the banner to opt-in, opt-out, or hidden by region. EU visitors can then see an opt-in banner while visitors from U.S. states see an opt-out one.
The banner can show a Decline button next to Accept on the first layer, and Enzuzo recommends keeping it on. For California visitors, Enzuzo recommends opt-in banners because of CIPA claims. On Pro and Enterprise plans, Enzuzo can detect a visitor's Global Privacy Control signal and opt them out once GPC support is turned on.
Visitors can reopen Enzuzo's cookie manager from a link placed anywhere on the site.
The cookie banner generator shows the banner's options and how to start.
Frequently asked questions
Is a cookie banner required in the UK?
A cookie banner is required in the UK when a site uses cookies outside PECR's five exceptions, such as advertising cookies, which always need consent. Since February 5, 2026, statistics and appearance cookies can run without consent if the site gives clear information and a simple, free way to object.
Does the CCPA require a cookie banner?
The CCPA doesn't require a cookie banner by name. It requires covered businesses that sell or share personal information to offer a Do Not Sell or Share link, or a single alternative opt-out link. They must also honor signals such as Global Privacy Control. California's regulations say a cookie banner alone isn't an acceptable way to opt out.
Does a cookie banner need a Reject All button?
Whether a Reject All button is required depends on the regulator. Most EDPB taskforce authorities treat a banner with no refuse option on any layer with an accept button as an infringement. France's CNIL expects refusal at the same level as acceptance. ICO examples show equal buttons, California requires symmetry when consent is sought, and Brazil's ANPD recommends one.
Is continuing to browse a site valid cookie consent?
Continuing to browse a site isn't valid cookie consent in the EU or the UK. The EDPB says scrolling or swiping never counts, and France's CNIL says continuing to browse isn't a clear positive act. The ICO says continuing to use a site isn't consent. In California, closing or navigating away from a consent pop-up isn't consent either.
What happens if a cookie banner doesn't meet the rules?
Breaking cookie banner rules can lead to regulator fines, and each law sets its own ceiling. France's CNIL can fine up to €10 million or 2% of worldwide turnover for a cookie breach, and UK fines reach £17.5 million or 4%. California's maximums are $2,663 per violation and $7,988 if intentional, and Quebec's reach $10 million or 2%.
Do analytics cookies need cookie consent?
Analytics cookies generally need consent in the EU, though France's CNIL exempts audience-measurement cookies that meet its conditions. Since February 5, 2026, UK sites can run statistics cookies without consent if visitors get clear information and a free way to object, but not to track individuals. Brazil's ANPD says legitimate interest may cover some audience measurement.
Osman Husain
Osman is the content lead at Enzuzo. He has a background in data privacy management via a two-year role at ExpressVPN and extensive freelance work with cybersecurity and blockchain companies. Osman also holds an MBA from the Toronto Metropolitan University.
LinkedIn →More related blogs
Your next read