Privacy Impact Assessment (PIA) in Canada: A PIPEDA Guide
Osman Husain
Last verified: October 2026.
A privacy impact assessment (PIA) is a check that identifies the risks a new project poses to people's privacy and records how the business will reduce them before it goes ahead.
PIPEDA doesn't require one by name. The Office of the Privacy Commissioner of Canada (OPC) still expects one for new projects involving personal information. Quebec's Law 25 does require one for information system projects, transfers out of Quebec and some research uses.
In the OPC's 2023-24 business survey, 37% of Canadian businesses said they had policies or procedures to assess privacy risks, including for new products, services or technologies. The share was 33% in 2022 and 38% in 2019. Businesses under PIPEDA, Canada's federal privacy law for the private sector, decide for themselves whether a project gets a formal privacy review; Quebec's Law 25 removes that choice for certain projects.
What is a privacy impact assessment?
A privacy impact assessment is a formal privacy review of one project, which the OPC's Self-Assessment Tool defines as "the identification and analysis of relevant risks to privacy." Quebec's privacy regulator, the Commission d'accès à l'information (CAI), splits the work into three parts in its PIA guide: a check against the law and its principles, a risk analysis, and a plan to reduce the risks.
A finished PIA report brings the CAI's three parts together with a map of the data flows, and the OPC's federal guide adds a formal approval step. A PIA is also a different tool from a security threat and risk assessment: the OPC's 2012 accountability guidance lists the two side by side.
Does PIPEDA require a privacy impact assessment?
PIPEDA doesn't require a privacy impact assessment, although the OPC recommends one. A search of the full Act, Schedule 1 included, finds no specific reference to an impact assessment.
What PIPEDA does require is accountability, the principle that the OPC ties PIAs to.
Under Schedule 1, clause 4.1.4, an organization must "implement policies and practices to give effect to the principles." The OPC's Self-Assessment Tool lists one such policy: a requirement to do PIAs "before new products, services or information systems are introduced."
The OPC's Getting Accountability Right guidance, issued in 2012 with the Alberta and BC commissioners, says assessments "should be required throughout the organization for all new projects involving personal information."
The OPC has also required PIAs as a remedy in specific investigations. After the Tim Hortons app investigation in 2022, the company agreed to build a privacy program that would require a PIA for any new app or app practice. In the TikTok findings in 2025, TikTok committed to giving the offices a PIA for each new age-assurance measure.
The OPC has confirmed that no general duty exists. In an April 2023 submission on Bill C-27, it asked Parliament to make PIAs mandatory for high-risk initiatives.
PIPEDA has no filing step either: sending completed PIAs to the Treasury Board Secretariat (TBS) and the OPC is a rule in the TBS Directive on Privacy Practices. Federal PIAs have been a policy requirement since 2002, and that policy binds government institutions, not businesses. Skipping a PIA isn't a PIPEDA offence, and PIPEDA's penalties cover what the Act does punish.
When should a business run a PIA?
A business should run a PIA when it starts a new project involving personal information, or any new collection, use or disclosure of it. These are the same triggers for a fresh PIA in the OPC's 2012 accountability guidance. Its footnote 6 counts changes too: "A new project may be modifying existing systems, components and processes."
The PIA's depth depends on the project it's assigned to. The OPC's federal guide is written for government institutions, but its risk factors work as a model for businesses, too:
- sensitive personal information, or a large amount of it
- many affected people, or vulnerable groups
- profiling or automated decisions about people
- systemic monitoring
- matching or combining data sets
- collection without notice or consent
- reuse for a new purpose, or sharing outside the organization
Where is a privacy impact assessment legally required in Canada?
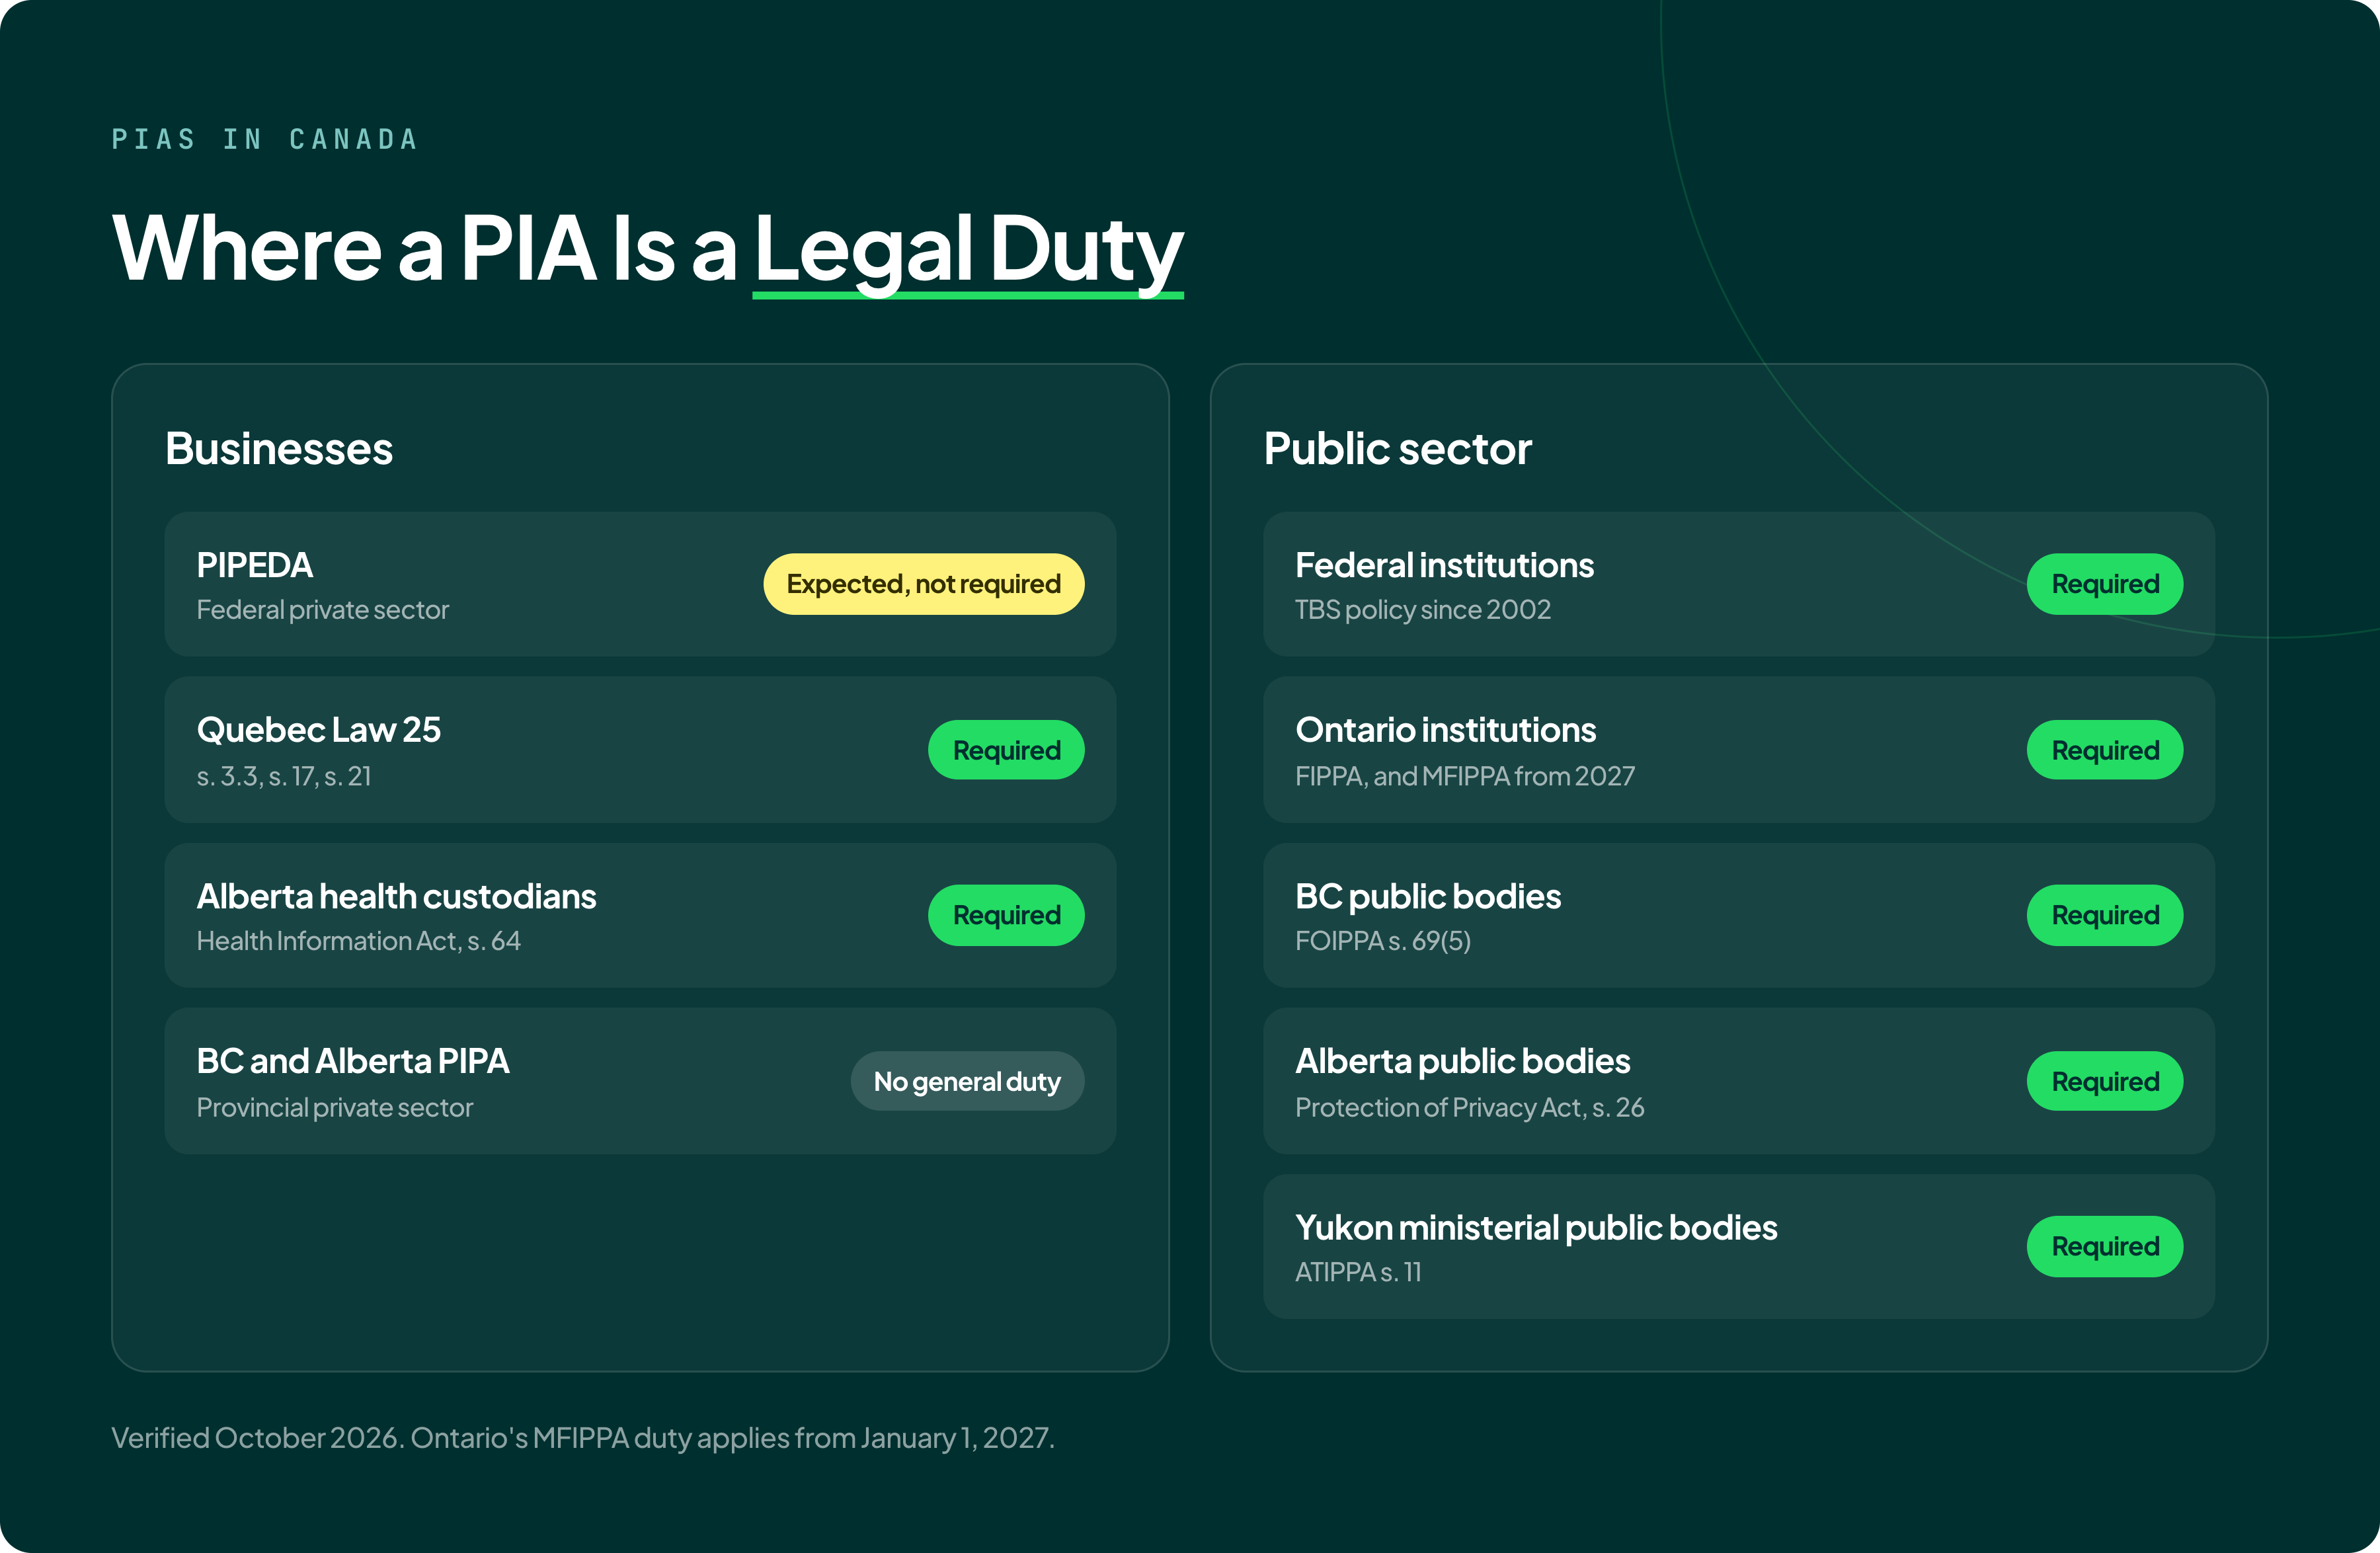
A privacy impact assessment is legally required in Canada for Quebec businesses under Law 25, for Alberta health custodians, and for public bodies in several jurisdictions. Businesses under PIPEDA alone have no such duty.
| Who must run a PIA | Legal source | When it's required | Status |
|---|---|---|---|
| Quebec businesses | Law 25: s. 3.3, s. 17 and s. 21 | A new or overhauled information system handling personal information (s. 3.3); a transfer outside Quebec (s. 17); identifiable information released to a researcher without consent (s. 21) | s. 3.3 and s. 17 since Sept 22, 2023; s. 21 since Sept 22, 2022 |
| Alberta health custodians | Health Information Act, s. 64 | A new or changed administrative practice or information system for identifying health information; the PIA goes to the Commissioner | In force |
| Federal government institutions | TBS Directive on Privacy Practices, Appendix C (policy, not statute) | New programs using personal information for administrative purposes, and substantial changes; PIAs go to TBS and the OPC | Policy requirement since 2002; current directive since Oct 9, 2024 |
| Ontario provincial and municipal institutions | FIPPA s. 38(3) and MFIPPA s. 28(3) | A written assessment before collecting personal information | FIPPA since July 1, 2025; MFIPPA from Jan 1, 2027 |
| BC public bodies | FOIPPA s. 69(5) and s. 69(5.3) | As the minister directs; ministries submit the PIA to the minister during development under s. 69(5.1) | In force |
| Alberta public bodies | Protection of Privacy Act, s. 26 | Circumstances the regulations prescribe | In force since June 11, 2025 |
| Yukon ministerial public bodies | ATIPPA s. 11, per the Yukon government's PIA template | A new program or activity, specialized service, data-linking activity or information management service, or a significant change to one | In force |
| No general duty | BC PIPA, Alberta PIPA and Ontario's PHIPA | Neither PIPA requires a PIA; PHIPA has no general duty for custodians, only narrow ones for health information network providers under O. Reg. 329/04 and certain electronic health record and digital health identifier activities | Not applicable |
Under s. 3.3, each Quebec PIA must be proportionate to the information's sensitivity, purposes, quantity, distribution and storage medium. For a systems project, the enterprise must also consult its privacy officer "from the outset of the project."
For the s. 17 transfer assessment, see PIPEDA cross-border transfers; and the guide to Quebec Law 25 for more on Quebec's take.
How to conduct a privacy impact assessment: 9 steps
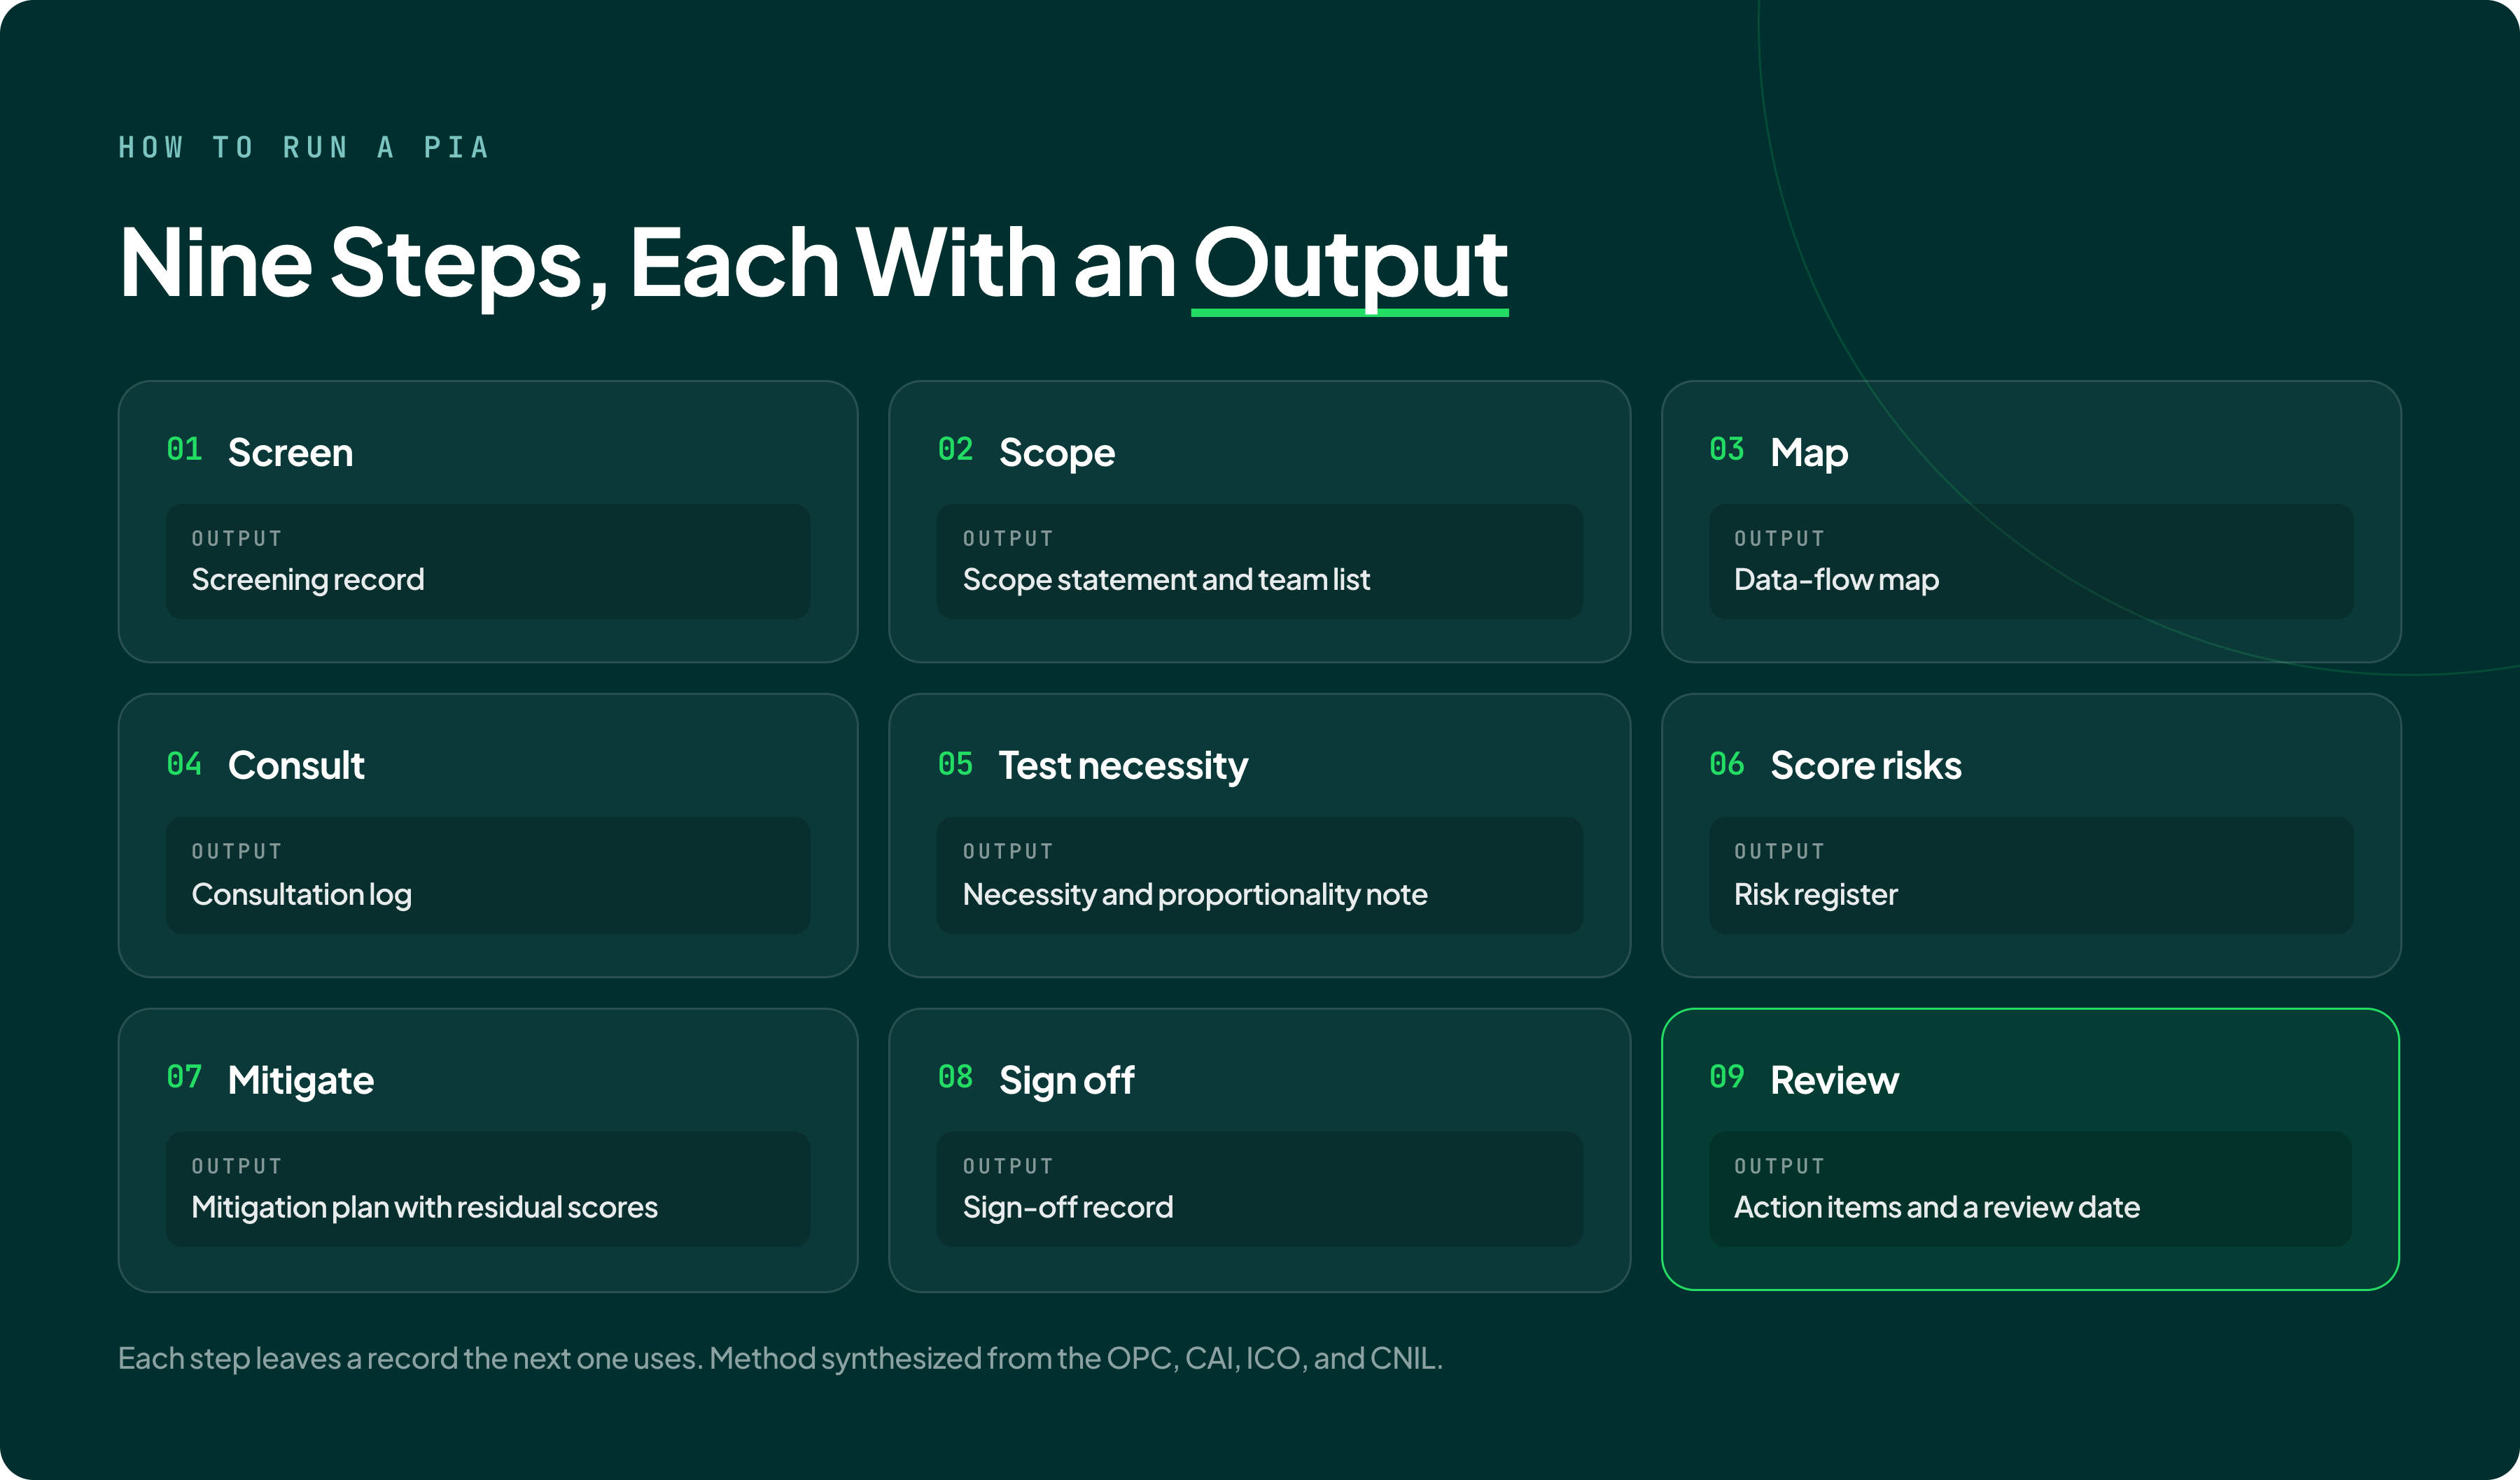
A privacy impact assessment runs in nine steps: screen, scope, map the data, consult, test necessity, score the risks, mitigate, sign off, and review. The sequence is Enzuzo's synthesis of methods from the OPC, Quebec's CAI, the UK Information Commissioner's Office (ICO) and France's CNIL, and each step leaves a record the next one uses.
How long those records run depends on the project: the OPC's federal guide, used as a method model for businesses, ties a PIA's length to the project's scale, complexity and risk. In its 2023 submission, the OPC also warned that requiring PIAs for every activity could put an excessive burden on small and medium-sized enterprises.
If you're the person running the assessment, take the steps in order:
- Screen the project and record the decision. Check it against the triggers and risk features above and, for a Quebec enterprise, Law 25's three legal triggers. Record the answer and the reasons, even when it's no. Output: a screening record.
- Scope it and assemble the team. Decide what the assessment covers, from a single feature to a whole program. Bring in the privacy officer from the start, plus the people who'll build and run the processing. Output: a scope statement and a team list.
- Describe the processing and map the data flows. Trace each piece of personal information from collection to deletion, including every hand-off to another system or an outside vendor. The business's existing data inventory is the starting point. Output: a data-flow map.
- Consult stakeholders. Ask the teams who'll run the processing what could go wrong and, where practical, hear from the people whose information is involved. Note who raised what and what changed. Output: a consultation log.
- Test necessity and proportionality. Check that the project needs each piece of personal information and that no less intrusive option would do. Enzuzo's method borrows the yardstick in PIPEDA s. 5(3), which allows collection, use and disclosure only for purposes "a reasonable person would consider are appropriate in the circumstances." Output: a necessity and proportionality note.
- Score the risks by likelihood and severity. List what could go wrong for the people involved, such as a breach, an unexpected use or a decision based on bad data. Rate each risk low to high for likelihood and for severity. Output: a risk register.
- Mitigate and re-score the residual risk. Pick a fix for each high-scoring risk, such as collecting less, shorter retention, tighter access, a consent step or a stronger vendor contract. Then re-score each risk with its fix in place. Output: a mitigation plan with residual scores.
- Decide, sign off and document. A named decision-maker accepts the residual risk, asks for more changes, or stops the project. The signed PIA records that decision and who made it, with the date. Output: a sign-off record.
- Feed actions into the project plan, then monitor and review. Give each mitigation an owner and a deadline in the project plan, so it ships with the product instead of staying on paper. The OPC's 2012 guidance asks organizations to treat PIAs as "evergreen documents," so set a review date and reopen the PIA when the project changes. Output: action items in the project plan and a review date.
How does a PIPEDA PIA compare with a GDPR DPIA or a California risk assessment?
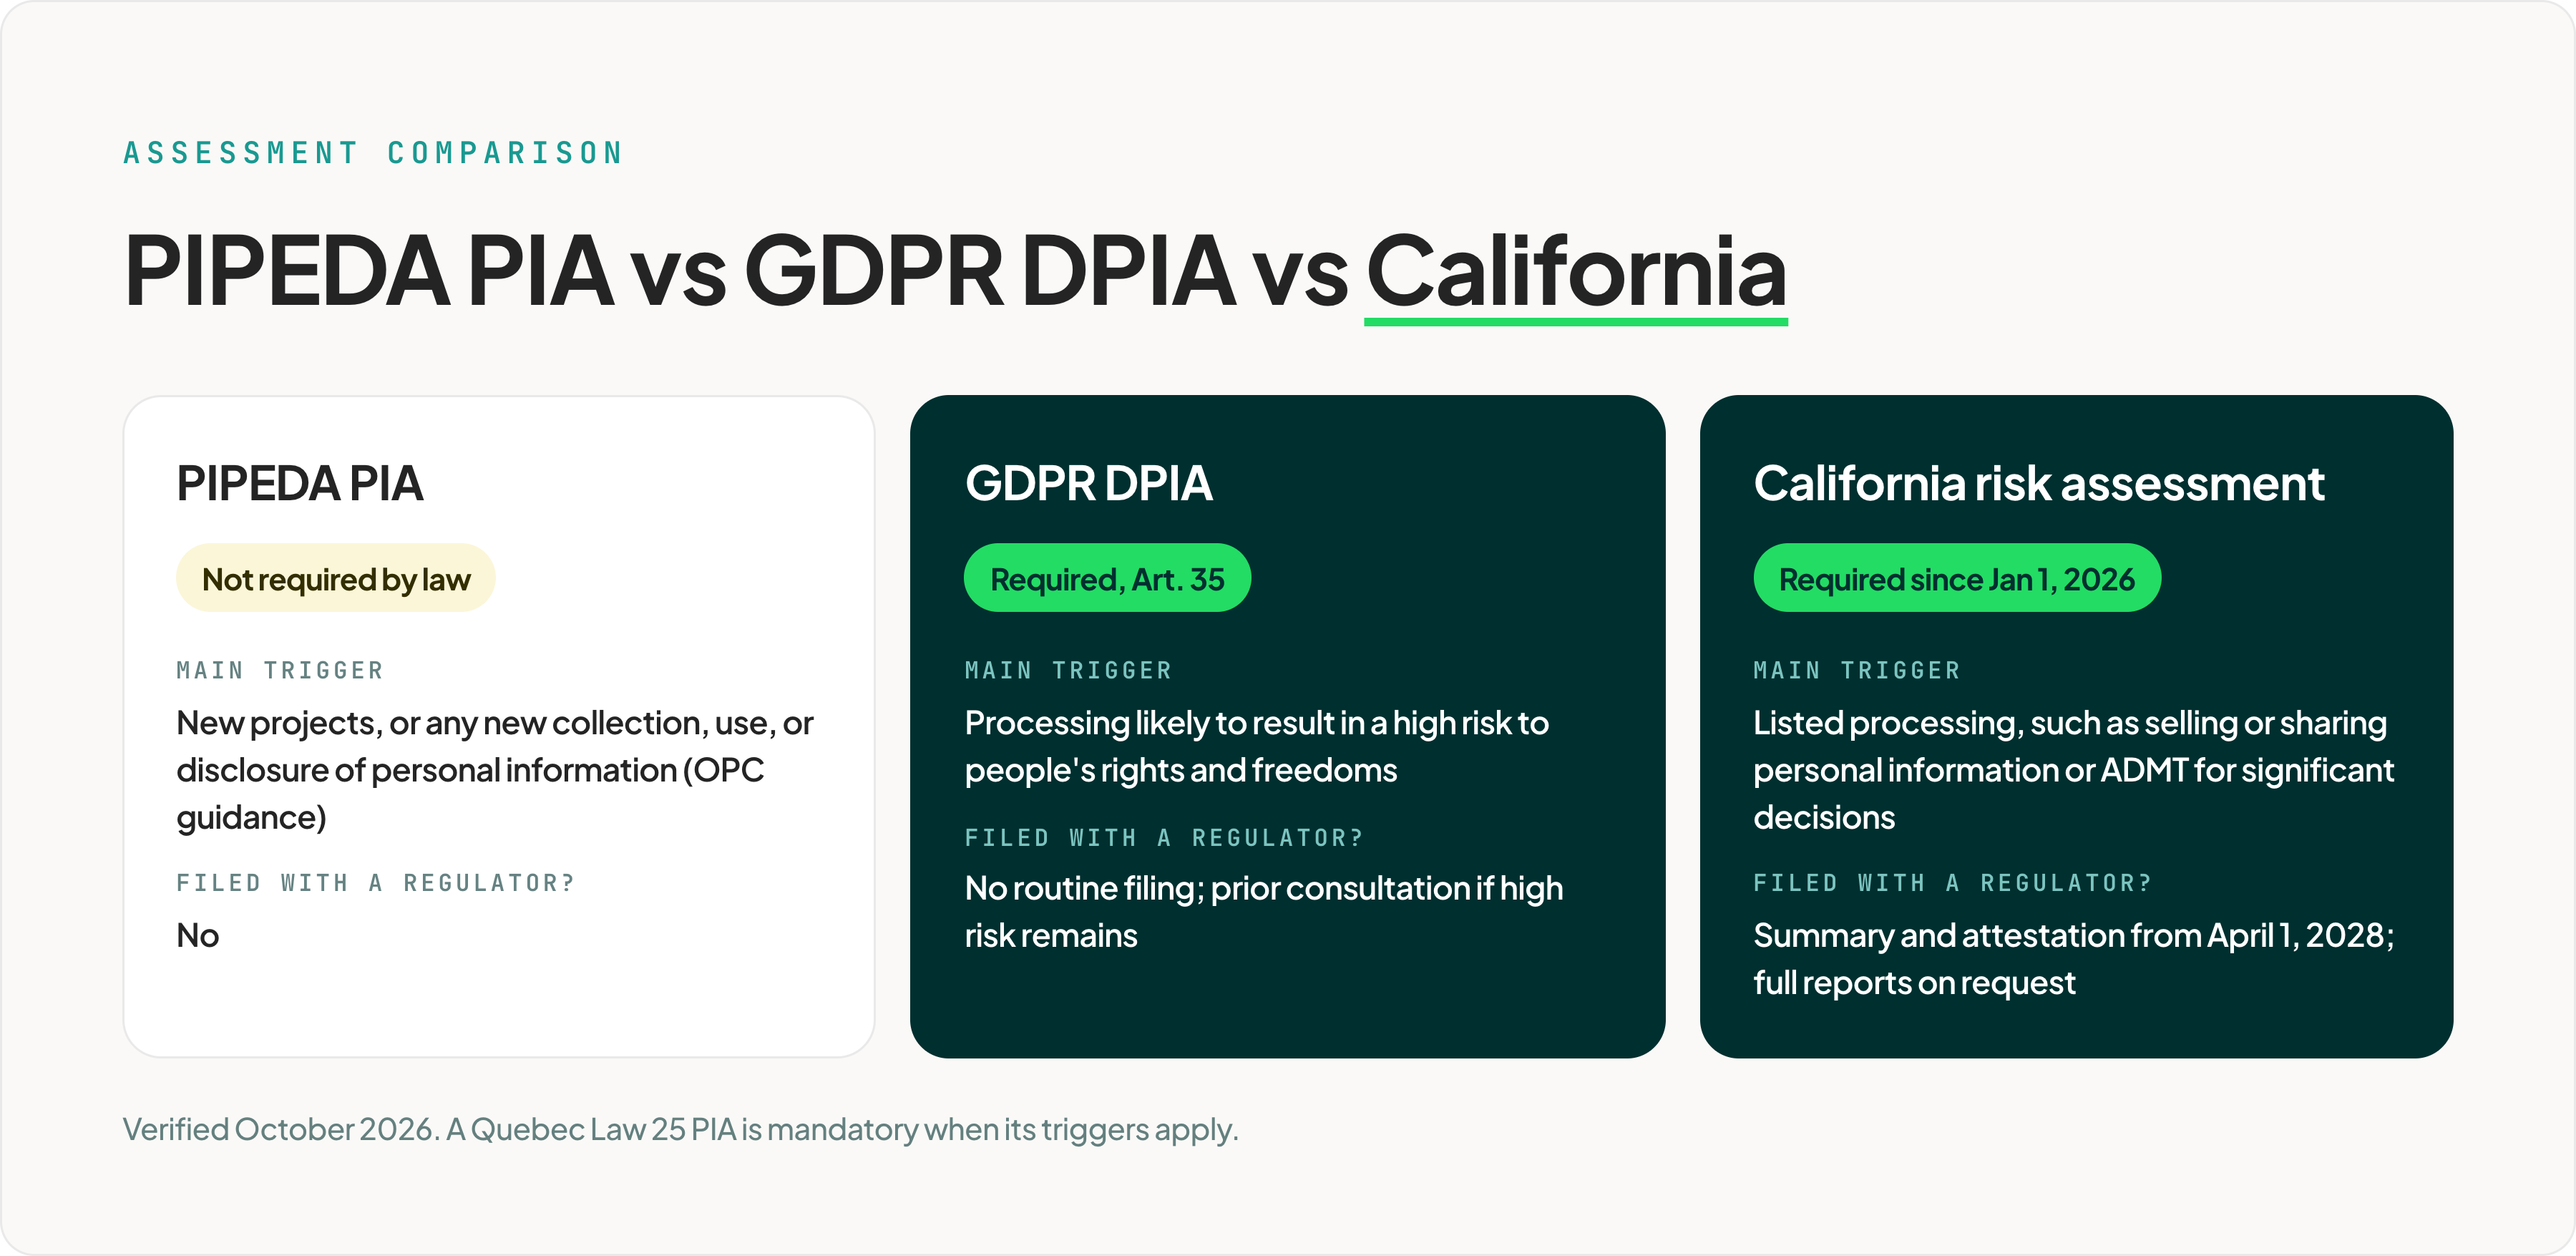
A PIPEDA PIA is expected practice rather than a legal duty, while a Quebec Law 25 PIA, the GDPR's data protection impact assessment (DPIA) and California's risk assessment are mandatory when their triggers apply. California's regulations call their version a risk assessment, never a PIA.
| Assessment | Required by law? | Main trigger | Filed with a regulator? |
|---|---|---|---|
| PIPEDA PIA | No: the Act never mentions one | New projects, or any new collection, use or disclosure of personal information, under the OPC's 2012 guidance | No |
| Quebec Law 25 PIA | Yes, under s. 3.3, s. 17 and s. 21 | A new or overhauled information system, a transfer out of Quebec, or a research release without consent | None required by s. 3.3, s. 17 or s. 21 |
| GDPR DPIA | Yes, under Art. 35 | Processing "likely to result in a high risk" to people's rights and freedoms | No routine filing; prior consultation under Art. 36 only if high risk remains after mitigation |
| California risk assessment | Yes, since Jan 1, 2026, under the CCPA regulations | Listed processing, such as selling or sharing personal information, or using automated decisionmaking technology for significant decisions | Summary information and an executive attestation, first due April 1, 2028; full reports only on request |
Will Bill C-36 make PIAs mandatory?
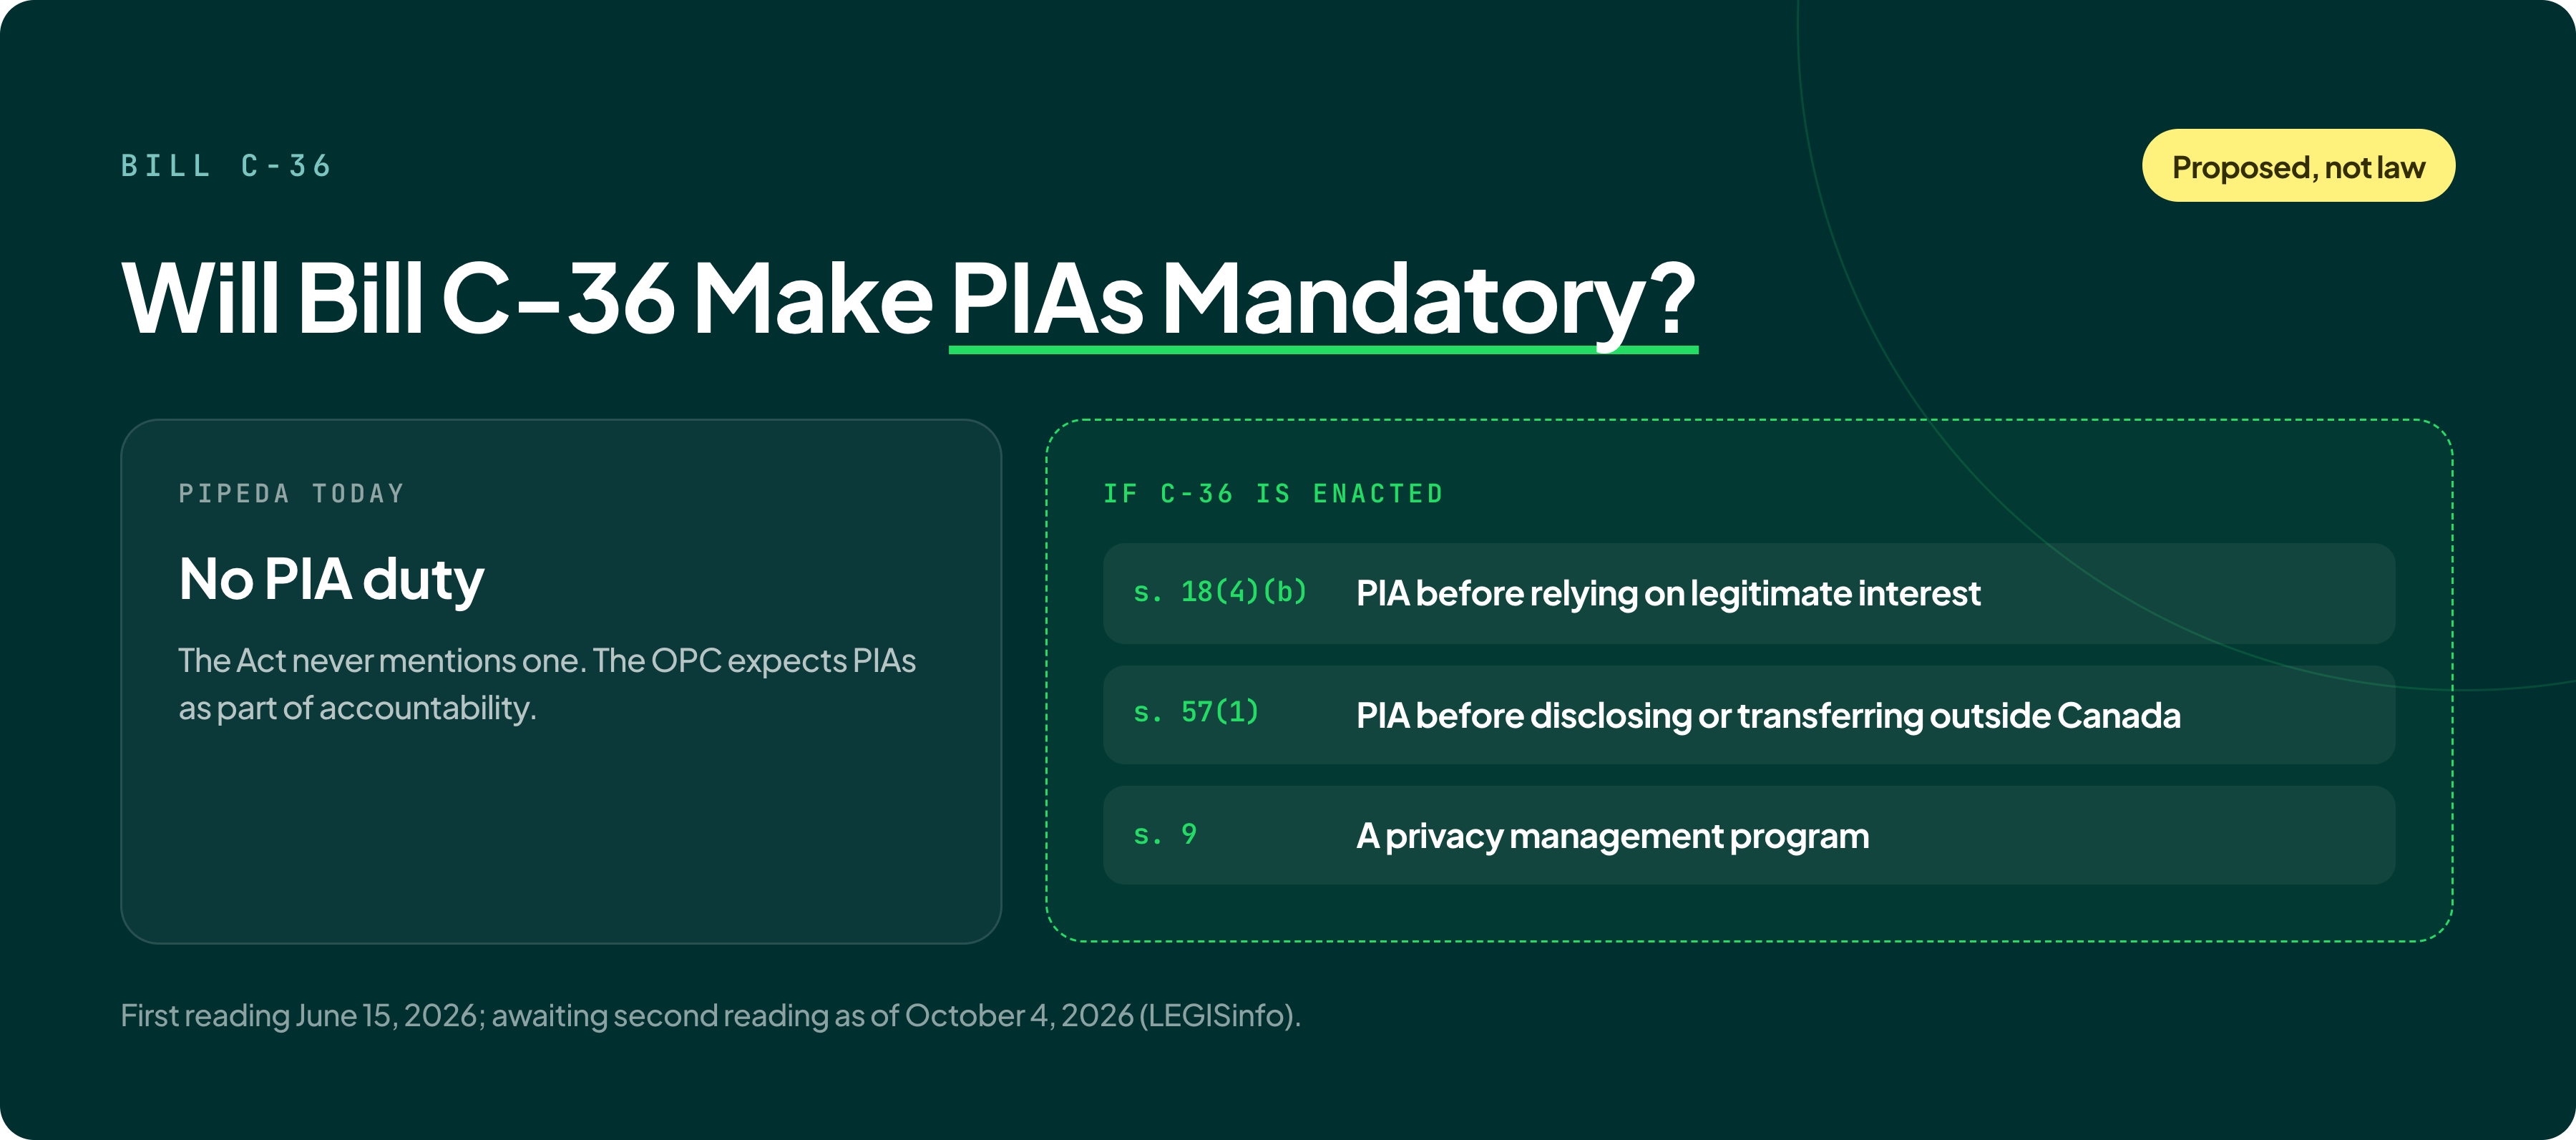
Bill C-36 would require a PIA before an organization relies on legitimate interest and before it discloses or transfers personal information outside Canada, but only if the bill becomes law. The Protecting Privacy and Consumer Data Act was introduced and read a first time on June 15, 2026, and LEGISinfo shows it awaiting second reading as of October 4, 2026.
Under s. 18(4)(b), the legitimate-interest PIA would come before an organization relies on that proposed exception to consent, available when its interest outweighs any reasonably foreseeable adverse effect. Under s. 57(1), the cross-border PIA, the federal counterpart to Quebec's s. 17, would come with mitigation such as contractual protections.
Every organization would also need a privacy management program under s. 9, which would make PIPEDA's accountability principle a standalone duty. What either PIA would have to contain is left to regulations that don't exist yet. For the bill's penalties and its new regulator, see PIPEDA penalties.
Where can a business get a free privacy impact assessment template?
Free privacy impact assessment templates come from privacy regulators: Quebec's CAI, the UK's ICO, the European Data Protection Board (EDPB) and France's CNIL each publish one.
- Quebec's CAI publishes its guide (version 3.1, April 2024) and a report template, both in French only; the law firm BLG publishes an unofficial English translation. The CAI says its guide isn't mandatory, since the law doesn't set a method.
- The UK ICO offers a sample DPIA template built around its UK GDPR process.
- The EDPB's DPIA template is version 1.0, released for consultation in 2026. It's voluntary and not yet final.
- The CNIL publishes PIA guides and free, open-source PIA software.
- Ontario's IPC wrote Planning for Success and its worksheets for public institutions under FIPPA and MFIPPA.
- The OPC's PIPEDA Self-Assessment Tool, for medium and large organizations, isn't a template but shows where PIAs fit in an accountability program.
How does Enzuzo help with a privacy impact assessment?
Enzuzo's consent management platform supplies evidence for a PIA rather than running one. Its consent records support step 3, by showing what website visitors agreed to, and step 7, when the chosen mitigation is a consent step. Enzuzo's data request form handles the access requests a PIA may plan for.
Enzuzo doesn't offer a dedicated PIA tool or data mapping. If you're responsible for an upcoming launch, step 1 is the test: check it against the triggers above and write down the answer.
Frequently asked questions
Is a PIA mandatory in Canada?
A PIA is mandatory in Canada only where a specific law or policy says so, such as Quebec's Law 25 for certain business projects, Alberta's Health Information Act for health custodians, and several public-sector laws. PIPEDA isn't one of them, although the OPC expects PIAs as part of good accountability.
Is there a fine for not doing a PIA under PIPEDA?
There's no fine for skipping a PIA under PIPEDA, because the Act never requires one. The exposure is indirect: an OPC investigation that finds weak accountability can end in a recommendation to adopt PIAs. PIPEDA penalties explains what the Act can fine.
Do businesses have to file a PIA with the OPC?
Businesses don't file PIAs with the OPC, because PIPEDA has no filing or approval step. Federal government institutions do have that duty: Treasury Board policy has them send completed PIAs to the Treasury Board Secretariat and the OPC. A business can still be asked for one after an investigation, as TikTok was in 2025.
How often should a PIA be updated?
A PIA should be updated whenever the project changes how it handles personal information, because the OPC treats a modified system as a new project. Quebec's CAI makes keeping the assessment up to date one of the steps in its PIA guide.
Does a small business need a PIA?
A small business under PIPEDA has no legal duty to run a PIA, but it can still screen each new project and record the result. A low-risk project may need only that screening record; a risky launch calls for a short assessment. In 2023 the OPC asked Parliament to require PIAs for high-risk initiatives rather than for everything, noting that a blanket requirement could overburden smaller businesses.
Osman Husain
Osman is the content lead at Enzuzo. He has a background in data privacy management via a two-year role at ExpressVPN and extensive freelance work with cybersecurity and blockchain companies. Osman also holds an MBA from the Toronto Metropolitan University.
LinkedIn →More related blogs
Your next read