Osman Husain
Complying with the California Consumer Privacy Act (CCPA) means a covered business discloses what personal information it collects, honors consumers' privacy requests, and keeps that data secure. The California Privacy Rights Act (CPRA) amended the CCPA, and most of its changes took effect on January 1, 2023.
A CCPA compliance checklist is therefore also a CPRA compliance checklist, too.
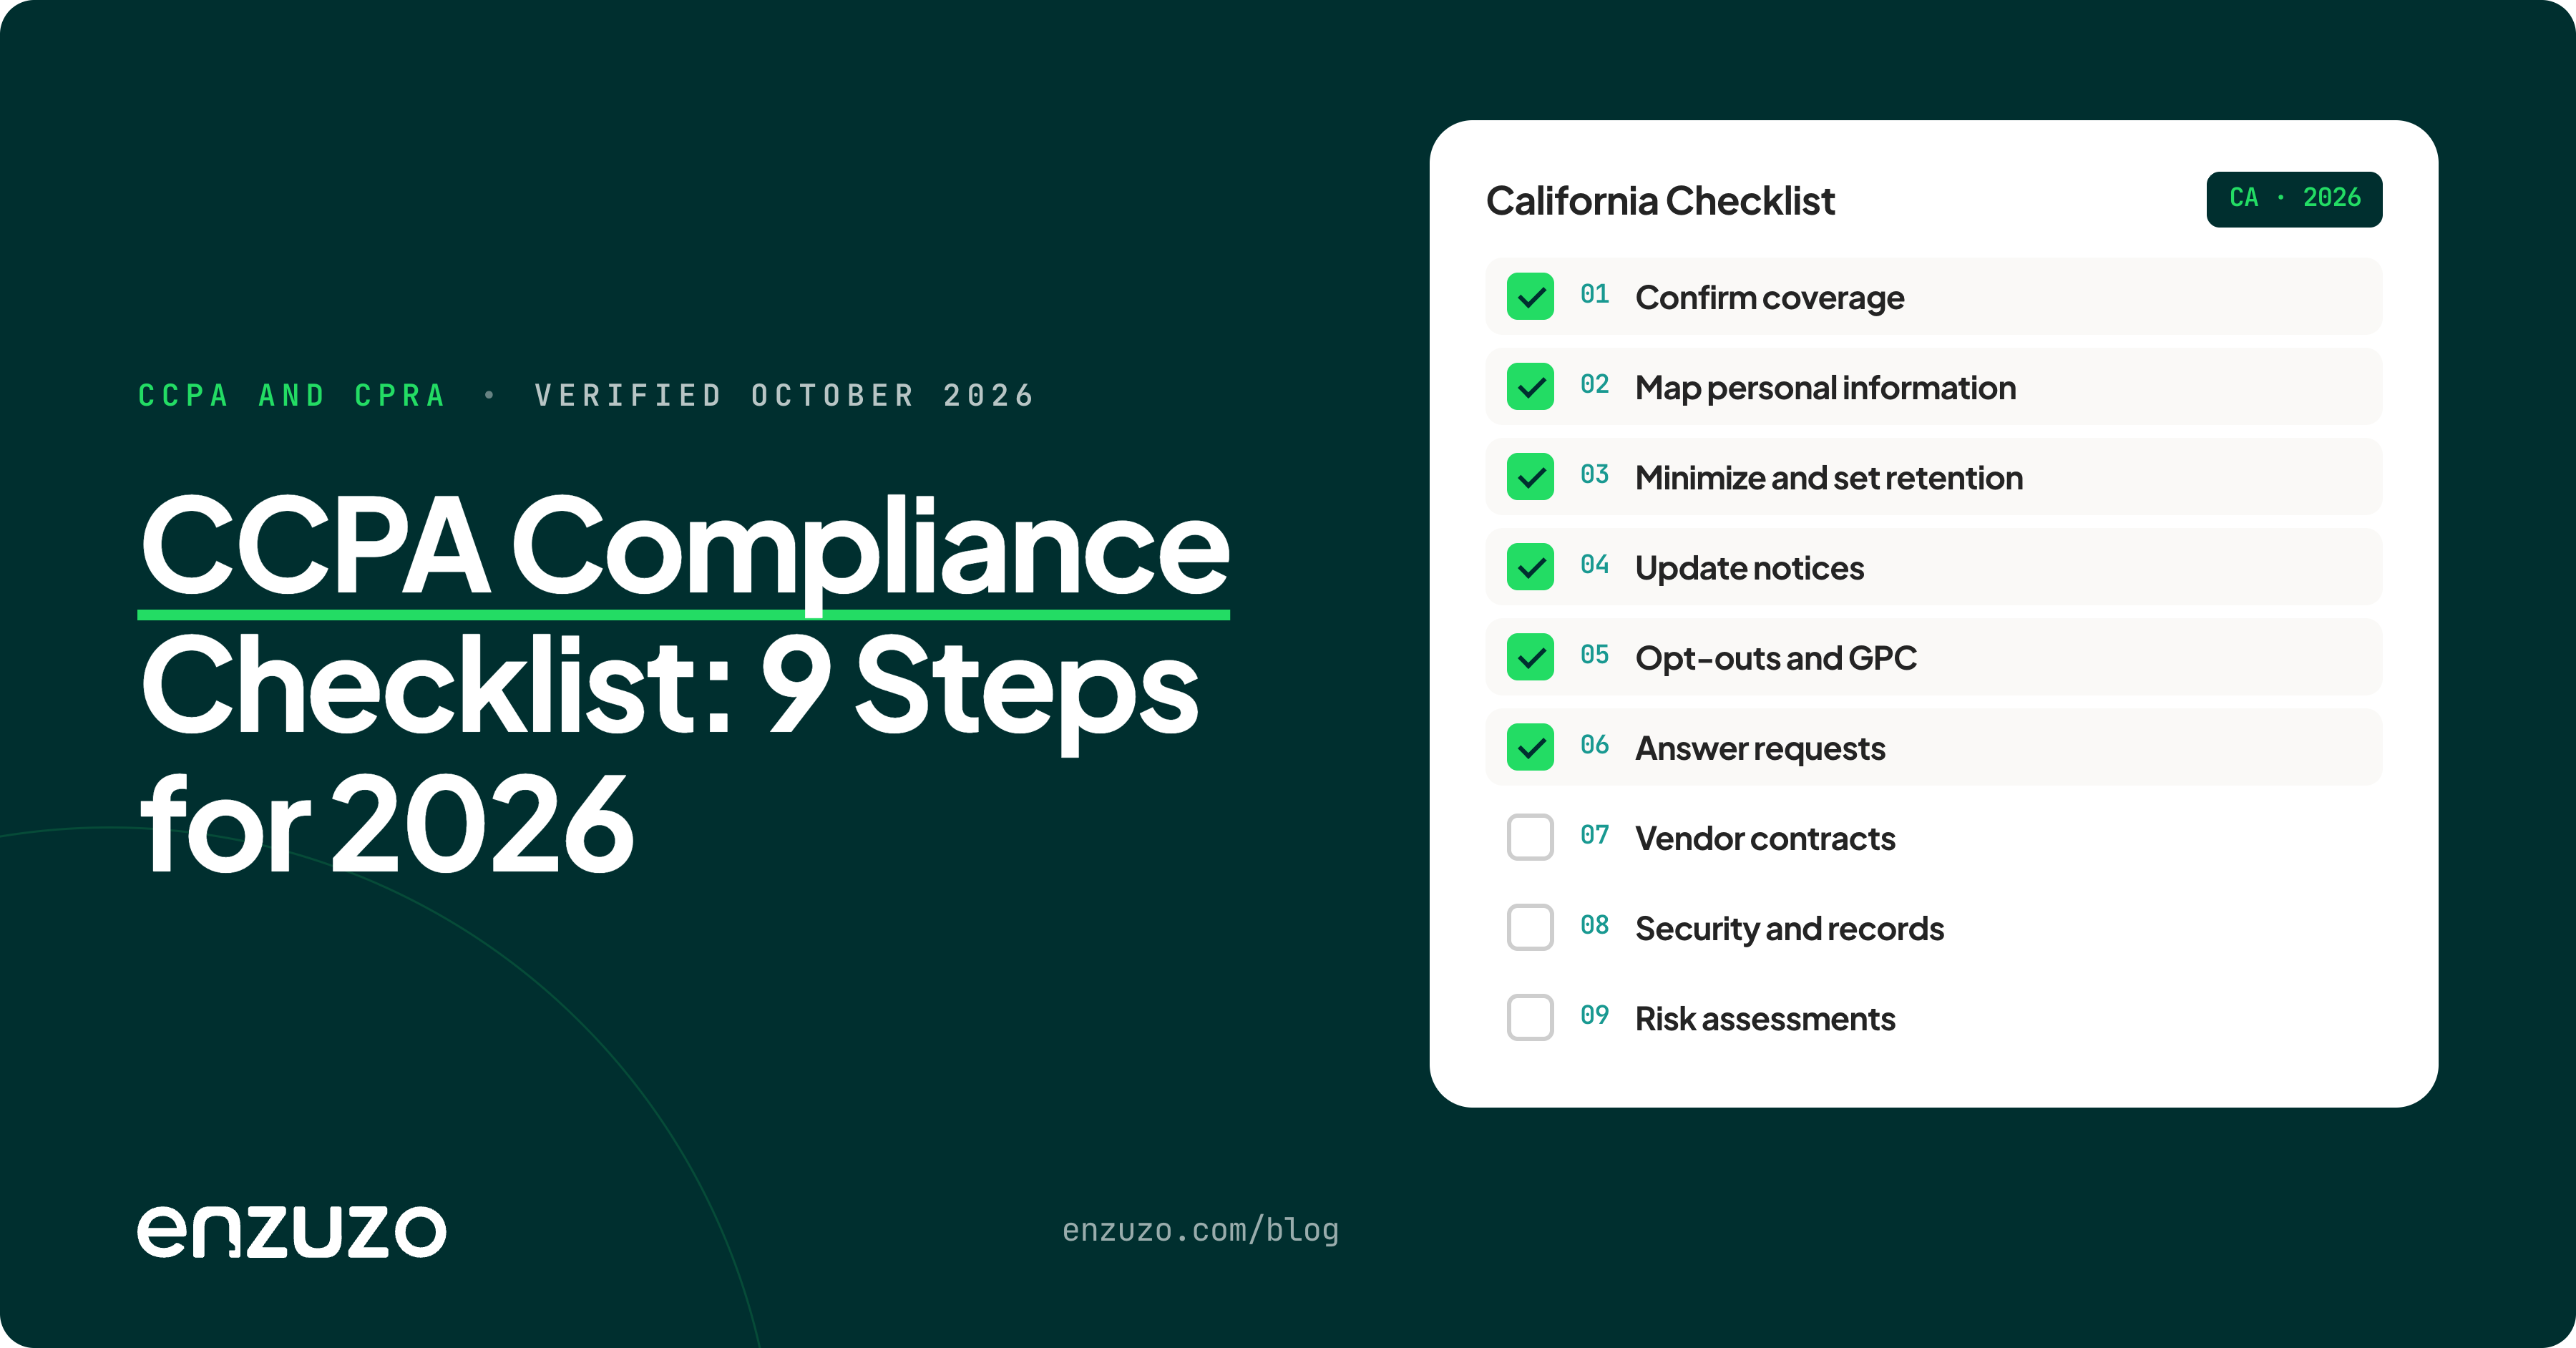
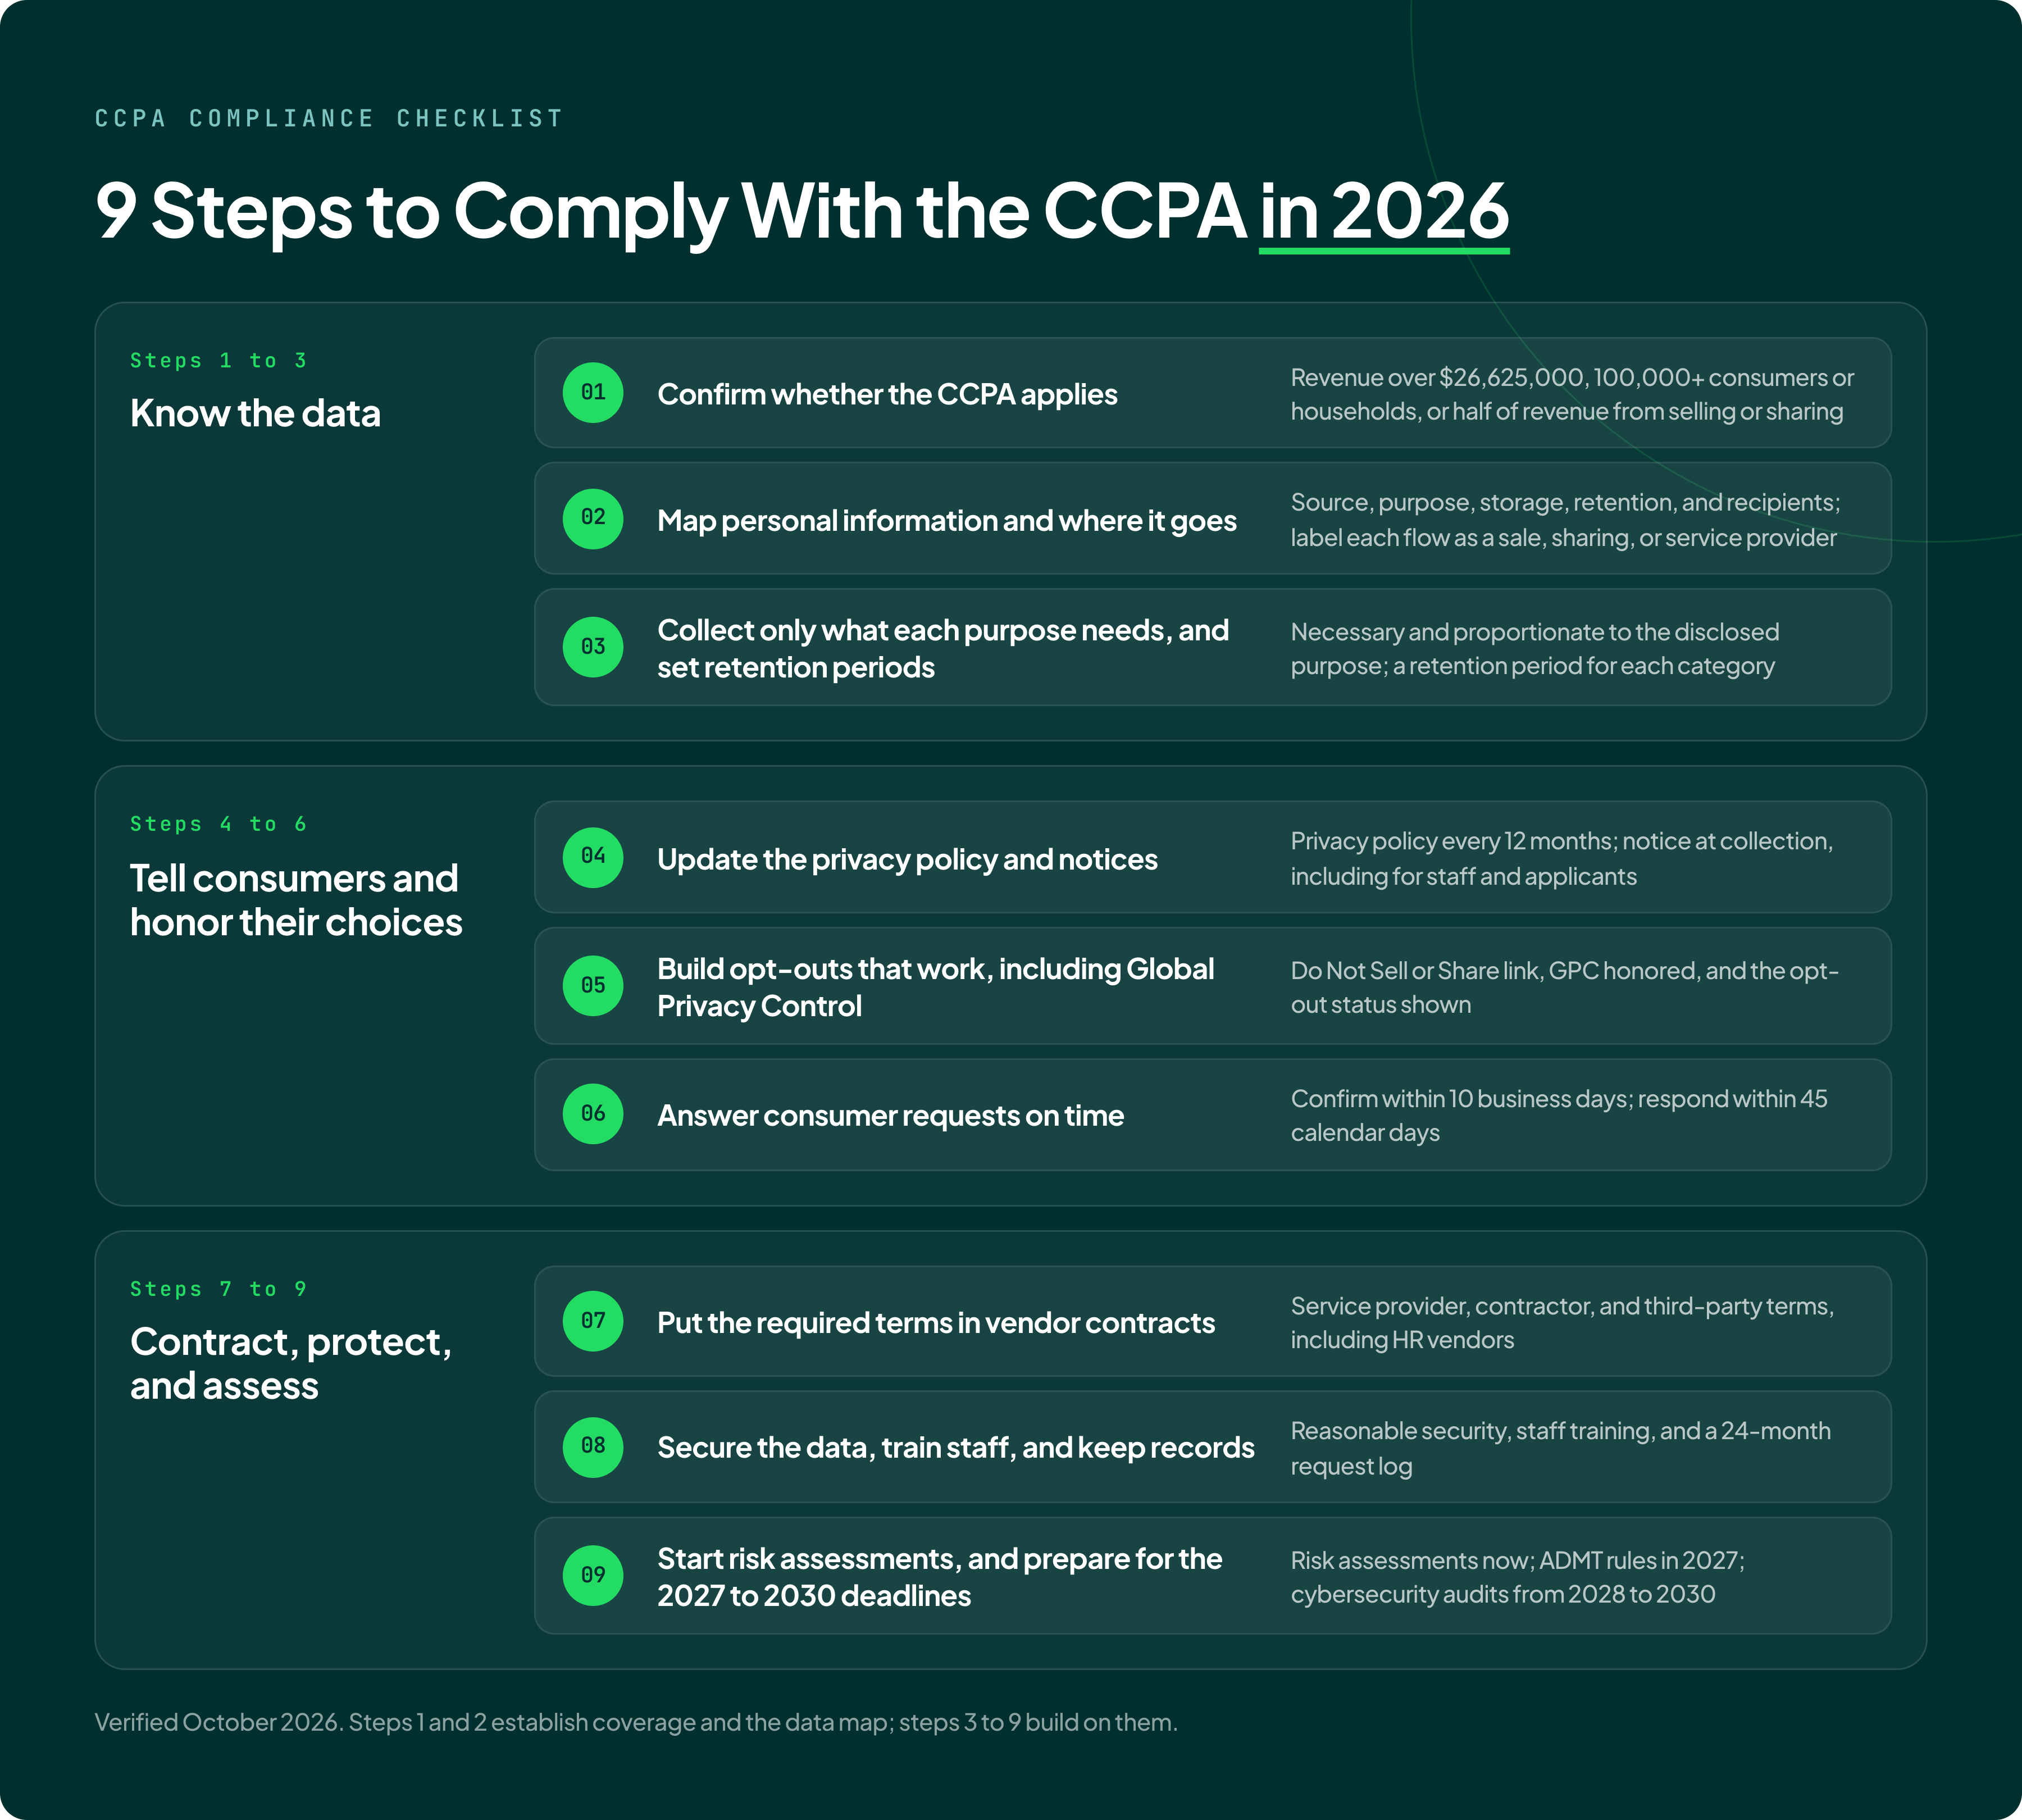
The CCPA compliance checklist, in nine steps:
- Confirm whether the CCPA applies.
- Map personal information and where it goes.
- Collect only what each purpose needs, and set retention periods.
- Update the privacy policy and notices.
- Build opt-outs that work, including Global Privacy Control.
- Answer consumer requests on time.
- Put the required terms in vendor contracts.
- Secure the data, train staff, and keep records.
- Start risk assessments, and prepare for the 2027 to 2030 deadlines.
Most of the CCPA's 2027 to 2030 deadlines come from new regulations that took effect on January 1, 2026 from the California Privacy Protection Agency, now referred to as CalPrivacy.
Since January 1, 2026, the CCPA's new regulations have required any business that sells or shares personal information to show visitors it honored their opt-out signal. The same business needs a written risk assessment before it starts any new data handling programs.
The 2026 duties build on the CCPA's original 2020 rules and the CPRA's 2023 amendments. Read more about what changed in CPRA vs CCPA .
How to comply with the CCPA: a 9-step checklist
To comply with the CCPA, a business first needs to establish a few things: whether the law covers it, what personal information it holds, and where that data goes.
Steps 1 and 2 determine coverage, and steps 3 to 9 turns that into data limits, notices, opt-outs, request handling, vendor contracts, security, and risk assessments.
1. Confirm whether the CCPA applies
The CCPA covers a for-profit business that collects California consumers' personal information, decides why and how it's processed, does business in California, and meets any one of three thresholds in Civil Code § 1798.140(d):
- Annual gross revenue above $26,625,000 in the preceding calendar year, the inflation-adjusted figure in effect since January 1, 2025.
- Buying, selling, or sharing the personal information of 100,000 or more California consumers in a year.
- Earning 50% or more of annual revenue from selling or sharing personal information.
The revenue test has no data minimum, so a company with $30 million in revenue and a few hundred California customers is liable. Empoyee headcount doesn't matter, and the business doesn't need an office in California, either.
A company under the revenue threshold can still meet the 100,000 threshold through its website. The count includes every consumer whose data its advertising tags share, customers or not. That route brings a busy site under the CCPA at any revenue level. An affiliate is also covered if it controls, or is controlled by, a CCPA-liable business; shares common branding with it; and receives that business's consumer data.
Government agencies and nonprofits generally fall outside the CCPA, because its definition of a business covers for-profit entities.
Some data is exempt even when the business is covered. Examples are protected health information regulated by HIPAA and financial data regulated by the Gramm-Leach-Bliley Act. Those exemptions mostly attach to the data, not the company, so a bank's or a clinic's website tracking can still fall under the CCPA.
Data about employees, job applicants, independent contractors, and business contacts was largely exempt until January 1, 2023, when the CCPA's temporary exemptions expired. HR records and B2B sales leads now carry the same duties as customer data.
Data brokers carry a second set of duties on top of the CCPA's, under California's Delete Act. A data broker registers with CalPrivacy and processes deletion requests from CalPrivacy's Delete Request and Opt-out Platform at least every 45 days. Amendment AB 883 shortens that cycle to 30 days on January 1, 2027.
CalPrivacy's applicability questionnaire walks through the CCPA coverage test in two pages.
2. Map personal information and where it goes
A data map is the working record behind most CCPA duties, even though the statute never requires one by name. For each category of personal information a business collects, it notes the source, purpose, storage location, retention period, and recipients. Every later step reads from that map: the privacy policy describes it, the opt-outs act on it, and consumer requests search it.
A CCPA data map lists the website's tags and pixels next to databases and spreadsheets, because cookie IDs, device identifiers, and IP addresses all count as personal information under the CCPA.
Each flow of data to an outside company needs a label, because the label decides which duties apply:
- Sale: a disclosure for money or anything else of value.
- Sharing: a disclosure for cross-context behavioral advertising, whether or not money changes hands. That term means ads targeted using a person's activity on websites, apps, or services other than the one they're using, including a company's other distinctly branded sites. Advertising pixels that send visitor data to an ad platform for targeting usually count as sharing. A vendor that runs that kind of advertising can't be a service provider for it, under 11 CCR § 7050(b).
- Service provider or contractor: a vendor that processes data on the business's behalf under a contract with the terms in step 7.
Sensitive personal information gets its own column on the map. Civil Code § 1798.140(ae) lists:
- Social Security, driver's license, state ID, and passport numbers
- account logins and financial account or card numbers, combined with the password or code that unlocks them
- precise geolocation, meaning data that can place someone within a circle with a radius of 1,850 feet
- racial or ethnic origin, citizenship or immigration status, religious or philosophical beliefs, and union membership
- the contents of mail, email, and text messages, unless the business is the intended recipient
- genetic data, neural data, and biometric data used to identify someone
- health, sex life, and sexual orientation information
The 2026 regulations add one more category: personal information of consumers the business knows are younger than 16, under 11 CCR § 7001(bbb)(4). CalPrivacy's 2026 guidance says that data may be subject to the consumer's right to limit how sensitive data is used.
For adults, sensitive data stays on an opt-out model in California: a bill to ban selling or sharing it outright, AB 1542, was vetoed in September 2026. Many other state privacy laws, such as Virginia's, require opt-in consent before processing sensitive data.
3. Collect only what each purpose needs, and set retention periods
The CCPA limits the personal information a business collects, uses, keeps, and shares to what's reasonably necessary and proportionate for the original purpose, or for a compatible purpose the business disclosed.
Under 11 CCR § 7002, that test turns on three factors: the minimum data the purpose needs, the possible harm to consumers, and the safeguards in place.
If a purpose is one the consumer wouldn't reasonably expect, and it isn't compatible with any purpose they would expect, the business needs the consumer's consent first. The consumer can generally withdraw that consent at any time. Even with consent, the data must still be reasonably necessary and proportionate to the purpose.
Run the data map from step 2 against the test; it flags every field that serves no disclosed purpose, and those are the fields to drop.
The CCPA's necessity limit also covers retention: a business can't keep personal information past what each disclosed purpose reasonably requires. Its notice at collection states how long it keeps each category, or the criteria that set the period.
Keeping data past its purpose was part of General Motors' $12.75 million settlement, announced in May 2026. The Attorney General said GM kept drivers' location and driving data long after OnStar needed it. GM then sold that data to two data companies, Verisk and LexisNexis.
The settlement is the largest CCPA penalty so far and the Attorney General's first data-minimization case.
4. Update the privacy policy and notices
Every covered business needs a privacy policy, linked from its homepage with the word privacy in the link text and updated at least every 12 months. Under 11 CCR § 7011, the policy covers:
- the categories of personal information collected in the past 12 months, their sources, and why they're collected
- the categories sold or shared and the types of third parties that received them, or a statement that the business doesn't sell or share
- the categories disclosed to service providers or contractors, and why
- whether the business knowingly sells or shares data of consumers under 16
- whether it uses sensitive personal information beyond the permitted purposes
- consumers' rights, such as the right not to face retaliation, and how to use them, including through an authorized agent
- how the business verifies requests and how it processes opt-out preference signals
- a privacy contact and the date of the last update
A mobile app has to link the policy from its app store page and from inside the app's settings menu.
The notice at collection is a shorter disclosure than the privacy policy, shown at or before the moment data is collected, such as beside a signup form. Under 11 CCR § 7012, it lists the categories collected (sensitive ones included), the purposes, whether each category is sold or shared, and how long each is kept.
The notice also links to the privacy policy and, for a business that sells or shares, to the opt-out. It can itself be a link into the privacy policy, but only if that link lands on the right section, not the top of the page.
A business that hasn't given the notice at or before collection can't collect the data at all. Adding a new category of data or an incompatible purpose takes an updated notice first.
When a third party such as an ad network collects data on a site through its pixel, both the site and the ad network owe a notice. One combined notice can serve both.
Employees and job applicants get a notice at collection too. Tractor Supply's $1.35 million fine, the largest administrative fine CalPrivacy has issued, included failing to give job applicants the required notice.
Loyalty programs and equal treatment. A business can't deny goods or services, charge a different price, or offer lower quality because a consumer used a CCPA right, under Civil Code § 1798.125. It also can't retaliate against employees, job applicants, or contractors who use theirs.
Loyalty programs and discounts tied to personal information are still allowed as financial incentives when they meet these conditions, under Civil Code § 1798.125(b) and 11 CCR §§ 7004, 7016, and 7080:
- the consumer opts in first and can withdraw at any time
- a notice of financial incentive comes before sign-up
- the business documents a good-faith estimate of what the consumer's data is worth, and can't offer the incentive without one
- the join option isn't preselected or shown more prominently than the option to decline
- after a consumer says no, the business waits 12 months before asking again
Plain language. Every notice has to use plain language and be readable on a phone, under 11 CCR § 7003. It also has to be accessible to people with disabilities, following a standard such as the Web Content Accessibility Guidelines (WCAG) 2.1.
5. Build opt-outs that work, including Global Privacy Control
Under the CCPA, a business that sells or shares personal information has to let consumers opt out. California regulators judge whether that opt-out works in practice, not only whether a link exists.
Broken opt-outs are the most common CCPA violation in California's enforcement so far. The Attorney General and CalPrivacy had announced 14 CCPA enforcement actions as of early October 2026. Thirteen of those actions involved an opt-out that was missing, didn't work, or added more friction than the law allows. Sephora, Disney, and Ford were among the 13.
[VISUAL: FLOW]
the opt-out path in four beats: signal or link received, opt-out applied to browser, device, and linked profiles, "Opt-Out Request Honored" shown, selling and sharing stopped within 15 business days
Alt: How a CCPA opt-out works, from the Global Privacy Control signal to the opt-out status message.
Full spec: see draft
The links. A business that sells or shares needs a Do Not Sell or Share My Personal Information link, under Civil Code § 1798.135. The link goes in the header or footer of the homepage and of any page that collects personal information, under 11 CCR § 7013(c). It either opts the visitor out right away or leads straight to the opt-out form.
A business can skip the link if it processes opt-out signals in a frictionless way, with no pop-up, fee, or change to the visitor's experience. It also has to meet the other conditions in 11 CCR § 7025(g). A business that doesn't sell or share posts no opt-out link, but its privacy policy has to say so.
A business that uses or discloses sensitive personal information beyond the permitted purposes has to add a Limit the Use of My Sensitive Personal Information link. The permitted purposes in 11 CCR § 7027(m) include:
- providing the goods or services an average consumer expects
- security, fraud prevention, and physical safety
- short-term uses, such as contextual ads that build no profile
- services performed for the business
- product quality and safety
- collecting or using sensitive data without inferring characteristics about the consumer
A business whose uses of sensitive data all fit that list says so in its privacy policy and needs no Limit link. A request to limit gets the same handling as an opt-out: no identity check, compliance within 15 business days, and a way for the consumer to confirm it went through.
A business that needs both links can use one combined link instead, which the regulations call the Alternative Opt-out Link. It's titled Your Privacy Choices or Your California Privacy Choices and carries the official opt-out icon.
Opt-out preference signals. California requires a business that sells or shares personal information to honor browser signals such as Global Privacy Control. Under 11 CCR § 7025 and the Attorney General's GPC guidance, the signal counts as a valid request to opt out of sale and sharing.
A signal-based opt-out applies to the browser or device and to any profile linked to it, including ad profiles that carry no name. Posting the opt-out links doesn't excuse a business from honoring the signal.
A Global Privacy Control signal overrides a visitor's earlier Accept All choice on the same site. When a visitor who clicked Accept All later arrives with GPC turned on, the business processes the signal as an opt-out of sale and sharing.
The business may point out the conflict and offer a chance to consent, under 11 CCR § 7025(c)(3). Once a known consumer has sent the signal, a later visit without it isn't an opt-in.
Showing the opt-out status. Since January 1, 2026, a business that sells or shares personal information has to show on its website whether it processed a visitor's opt-out signal, under 11 CCR § 7025(c)(6). The regulation's own example of that message is Opt-Out Request Honored.
The 2023 version of the rule only allowed the display; the 2026 version requires it. Consumers also need a way to confirm that an opt-out went through.
No friction. Opting out can't require an account, identity verification, or more information than the request needs, under 11 CCR § 7026. A business that offers opt-outs by category also offers one option to opt out of everything.
Cookie banners. A cookie banner alone doesn't count as a CCPA opt-out method under 11 CCR § 7026(a)(4), because cookies concern collecting personal information, while the opt-out covers selling and sharing it.
Timing. After an opt-out request arrives, a business has to stop selling and sharing that consumer's personal information as soon as it can. The limit is 15 business days, under 11 CCR § 7026(f). The business then notifies any third party that received the data between the request and the cutoff.
After an opt-out, a business waits at least 12 months before asking the consumer to opt back in, under 11 CCR § 7026(k), unless the regulations allow an earlier request.
Symmetry in choice. The CCPA's regulations bar any design where the more privacy-protective choice takes more steps, or is harder to pick, than the less protective one. Under 11 CCR § 7004, these designs fail the symmetry and no-confusion rules:
- a banner that offers only Accept All and More Information
- a yes button that's bigger or brighter than the no button
- a fake countdown clock or other false urgency beside the choice
- treating a closed pop-up as consent
The symmetry and no-confusion rules apply to every CCPA request and consent method. Agreement obtained through a dark pattern, meaning a design that substantially subverts or impairs a person's choice, isn't consent at all, under Civil Code § 1798.140.
A design with that effect is still a dark pattern when the business didn't intend it but knows about it and doesn't fix it, under 11 CCR § 7004(c).
Consumers under 16. A business that knows a consumer is under 16 can't sell or share their data without opt-in consent, under Civil Code § 1798.120(c). Consumers aged 13 to 15 give that consent themselves; for children under 13, a parent or guardian does. Willfully disregarding a consumer's age counts as knowing it.
For a child under 13, the business needs a documented way to confirm that the person consenting is the parent or guardian, under 11 CCR § 7070. That's on top of any parental consent the federal Children's Online Privacy Protection Act requires.
Apps and devices. The opt-out notice has to reach consumers the same way the data is collected. At least one opt-out method also has to match how the business mainly interacts with them, under 11 CCR §§ 7013(e)(3) and 7026(a). Sling TV and Jam City were penalized for having no opt-out inside their apps.
Testing. Businesses have to test that their request methods work, under 11 CCR § 7004. Loading the site in a browser with GPC turned on shows whether advertising tags stop and whether the Opt-Out Request Honored message appears.
At an August 2026 board meeting, CalPrivacy staff said existing rules already call for detecting GPC before any cookies or tracking that sell or share data load. Staff recommended adding an example saying so to the regulations.
6. Answer consumer requests on time
The CCPA gives a business 45 calendar days to respond when a consumer asks it to disclose, delete, or correct their personal information. Consumers can ask what the business has collected about them, including a portable copy. They can also ask it to delete the data it collected from them, or to correct it.
Request methods. A business has to offer at least two ways to submit these requests, one of them a toll-free number, under Civil Code § 1798.130. A business that isn't online-only and has a website must also accept requests through the site, such as with a webform.
A business that operates only online and deals with consumers directly can offer an email address instead of a phone line. SB 923, signed in September 2026, ends that email-only option on January 1, 2027: from then on, online-only businesses must offer an online method, such as a webform, alongside the email address.
Deadlines. A business has to confirm receipt of a request to know, delete, or correct within 10 business days, under 11 CCR § 7021. The 45-day clock starts when the request arrives and keeps running however long verification takes. The business can extend once by another 45 days if it tells the consumer why within the first 45.
Responses are free. A business can charge a reasonable fee, or refuse to act, when it can show a request is manifestly unfounded or excessive, such as a string of repeat requests. It also doesn't have to answer more than two requests to know from the same consumer in a 12-month period.
A business can't make someone create an account to submit a request, though it can ask existing account holders to use theirs.
Verification. Requests to know, delete, or correct need a reasonable, documented method for confirming the requester's identity against details the business already holds. Account holders can be verified through their existing login, under 11 CCR § 7061.
For someone without an account, 11 CCR § 7062 sets a reasonable degree of certainty for a request about categories of data, which may mean matching two data points. A request for specific pieces needs a reasonably high degree of certainty, which may mean matching three data points plus a declaration signed under penalty of perjury.
Complete answers. A response to a request to know includes data held by the business's service providers and contractors. On request, it also covers data older than 12 months, back to January 1, 2022, unless that proves impossible or takes disproportionate effort.
A response never includes Social Security, government ID, financial account, health insurance, or medical ID numbers. It also leaves out passwords, security questions and answers, and biometric data. The business says it holds that type of data instead, under 11 CCR § 7024(d). A business that turns a request down, in whole or part, explains why within the response period.
Deletion. A business that deletes a consumer's data must pass the request to its service providers and contractors. It must also notify any third parties it sold or shared the data with. Notifying third parties can be skipped only when it proves impossible or takes disproportionate effort, which the business then explains in detail.
Deleting can mean erasing the data, deidentifying it to the CCPA's standard so it can't reasonably be linked back to the person, or aggregating it, under 11 CCR § 7022. Data on backup systems can wait until the backup is restored or next used.
A business can keep what it reasonably needs for one of eight purposes in Civil Code § 1798.105(d), such as completing a transaction, security, fixing errors, or meeting a legal obligation. It deletes the rest and tells the consumer what it kept and why.
A business that sells or shares data and turns down a deletion request has to ask whether the consumer wants to opt out of that sale or sharing, under 11 CCR § 7022(g). That question isn't needed if the consumer already opted out. A business that lets consumers delete selected data also has to offer one option to delete everything.
From January 1, 2027, SB 923 extends deletion to personal information the business got about the consumer from other sources. It also lets the business keep a minimal record so deleted data stays deleted.
Correction. A business weighs everything it knows about contested data, including documents the consumer sends, under 11 CCR § 7023. It can refuse on accuracy grounds only when the data is more likely than not accurate. It corrects its own systems, makes sure a later data refresh doesn't overwrite the fix, and tells its service providers and contractors to correct their copies.
Verification for a correction relies on details other than the ones being corrected.
Authorized agents. A consumer can use an agent to make a request. The business can ask for the consumer's signed permission, but it can't demand a power of attorney.
7. Put the required terms in vendor contracts
Every vendor that receives personal information needs a written contract with terms the CCPA spells out, under Civil Code § 1798.100(d) and 11 CCR § 7051. For a service provider or contractor, the contract:
- names the specific business purposes, not a general reference to the whole agreement
- bars selling or sharing the data, and using it outside those purposes or outside the direct business relationship
- requires CCPA compliance and the same level of privacy protection the business owes
- gives the business the right to check compliance, and to stop and fix unauthorized use
- requires the vendor to say when it can no longer comply, and to help with consumer requests
- for a contractor, includes its certification that it understands and will follow these limits, under Civil Code § 1798.140(j)
- may also require the vendor to help with the business's risk assessments and cybersecurity audits, which 11 CCR § 7050(h) already obliges service providers and contractors to do
HR, payroll, and recruiting vendors need the same terms as marketing vendors.
Third parties that buy or receive shared data need their own contract naming the limited purposes, under 11 CCR § 7053. A service-provider contract also decides how the CCPA treats the vendor. Under 11 CCR § 7050(e), a vendor without a compliant contract isn't a service provider at all. Sending it data may then count as a sale or sharing, which triggers the opt-out right.
Missing contract terms featured in the cases against Honda, Healthline, and Tractor Supply. Under 11 CCR § 7051(c), a business that never checks how its vendors use the data can lose the defense that it had no reason to suspect misuse, even with a signed contract.
8. Secure the data, train staff, and keep records
The CCPA requires reasonable security suited to the kind of personal information a business holds. The law doesn't list the controls.
The cybersecurity audit rules in 11 CCR § 7123 do name what an audit assesses. The list includes phishing-resistant multi-factor authentication, encryption at rest and in transit, access controls, vulnerability scans, logging, vendor oversight, and incident response. That list works as a benchmark even for businesses the audit rule doesn't reach.
Security is also the one CCPA duty consumers can sue over directly, under Civil Code § 1798.150. The right applies only when one of these is stolen or disclosed without authorization because security fell short. The first three come from Civil Code § 1798.81.5 and count only when unencrypted and unredacted; the fourth comes from § 1798.150 itself:
- a person's name combined with a government ID number, such as a Social Security or driver's license number
- a person's name combined with a financial account number and its access code
- a person's name combined with medical, health insurance, biometric, or genetic data
- an email address with the password or security answer that unlocks the account
A leak of cookie IDs or browsing data alone doesn't trigger that right. Each affected consumer can recover $107 to $799 per incident at the 2025 adjusted amounts, or actual damages if higher. Before suing for those statutory damages, a consumer has to give the business 30 days' written notice and a chance to fix the violation. Adding reasonable security after a breach doesn't count as fixing that breach.
A breach also triggers a separate duty under California's breach-notification law, which isn't part of the CCPA. That law requires a business that owns or licenses computerized personal information, as the law defines it, to notify affected California residents. Since January 1, 2026, the notice has been due within 30 calendar days of discovering or learning of the breach.
A delay is allowed only for law enforcement's needs or for the time needed to find the breach's scope and restore the system. When more than 500 California residents get a notice, a sample copy goes to the Attorney General within 15 calendar days of notifying them.
Staff training. Everyone who handles consumers' privacy questions at a covered business has to know the CCPA's requirements and how to direct people to their rights, under 11 CCR § 7100.
A business that buys, receives, sells, or shares the personal information of 10 million or more consumers a year must also keep a written training policy, under 11 CCR § 7100(b). It must publish its request statistics by July 1 each year, under 11 CCR § 7102.
Request records. A business has to keep records of consumer requests for at least 24 months, under 11 CCR § 7101. A simple log works if it records the date and type of each request, how it came in, the date and nature of the response, and the reason for any denial.
9. Start risk assessments, and prepare for the 2027 to 2030 deadlines
The CCPA regulations in force since January 1, 2026 added three duties with dates that run into 2030: risk assessments, rules for automated decision-making technology (ADMT), and cybersecurity audits. California's Office of Administrative Law approved the regulations in September 2025.
Risk assessments. A business needs a written risk assessment before it starts high-risk processing, under 11 CCR § 7150. Selling or sharing personal information counts as high-risk processing, so any business whose website shares data through targeted-advertising tags needs one. Processing sensitive personal information and using ADMT for significant decisions count too.
Processing that started before January 1, 2026 and continues needs a completed CCPA risk assessment by December 31, 2027, under 11 CCR § 7155(b). By April 1, 2028, the business must file a summary with CalPrivacy under 11 CCR § 7157, along with an executive's attestation signed under penalty of perjury.
Automated decision-making. ADMT is technology that replaces, or substantially replaces, human decision-making. A significant decision is one about financial or lending services, housing, education, employment or pay, or healthcare, and advertising isn't one. A business that uses ADMT for a significant decision owes consumers a pre-use notice, a way to opt out, and access to information about how the decision was made.
Businesses using ADMT for significant decisions before January 1, 2027 must comply by that date, under 11 CCR § 7200(b), and uses that start later comply from the start. The opt-out has exceptions for decisions the consumer can appeal to a human reviewer with authority to overturn them, and for some hiring, admission, and work-allocation uses.
Cybersecurity audits. An independent cybersecurity audit is required of two groups, under 11 CCR § 7120:
- businesses that earn half or more of their revenue from selling or sharing personal information
- businesses over the revenue threshold that, in the prior year, processed the personal information of 250,000 or more consumers or households, or the sensitive personal information of 50,000 or more consumers
The first audit and its certification are due April 1, 2028 for businesses with more than $100 million in 2026 revenue. Businesses with $50 million to $100 million in 2027 revenue follow on April 1, 2029. Businesses with less than $50 million in 2028 revenue follow on April 1, 2030. After that, audits repeat every year for as long as the business meets § 7120, under 11 CCR § 7121.
Other January 1, 2027 changes. SB 923's expanded deletion right and its webform rule for online-only businesses take effect. Businesses that make web browsers must include a setting consumers can turn on to send an opt-out signal, under Civil Code § 1798.136. The revenue threshold, fines, and breach damages also adjust for inflation, with new figures posted by January 15, 2027.
Rules still in the works. In August 2026, CalPrivacy's board directed staff to prepare CCPA rules that would name Global Privacy Control as an opt-out signal outright. The same rules would require businesses that publish request statistics to report how many opt-outs arrived through signals such as GPC. They would also replace the 10-million-consumer cutoff for publishing statistics with a broader significant-risk standard.
No draft text had been published as of October 2026, and CalPrivacy posts proposals on its regulations page.
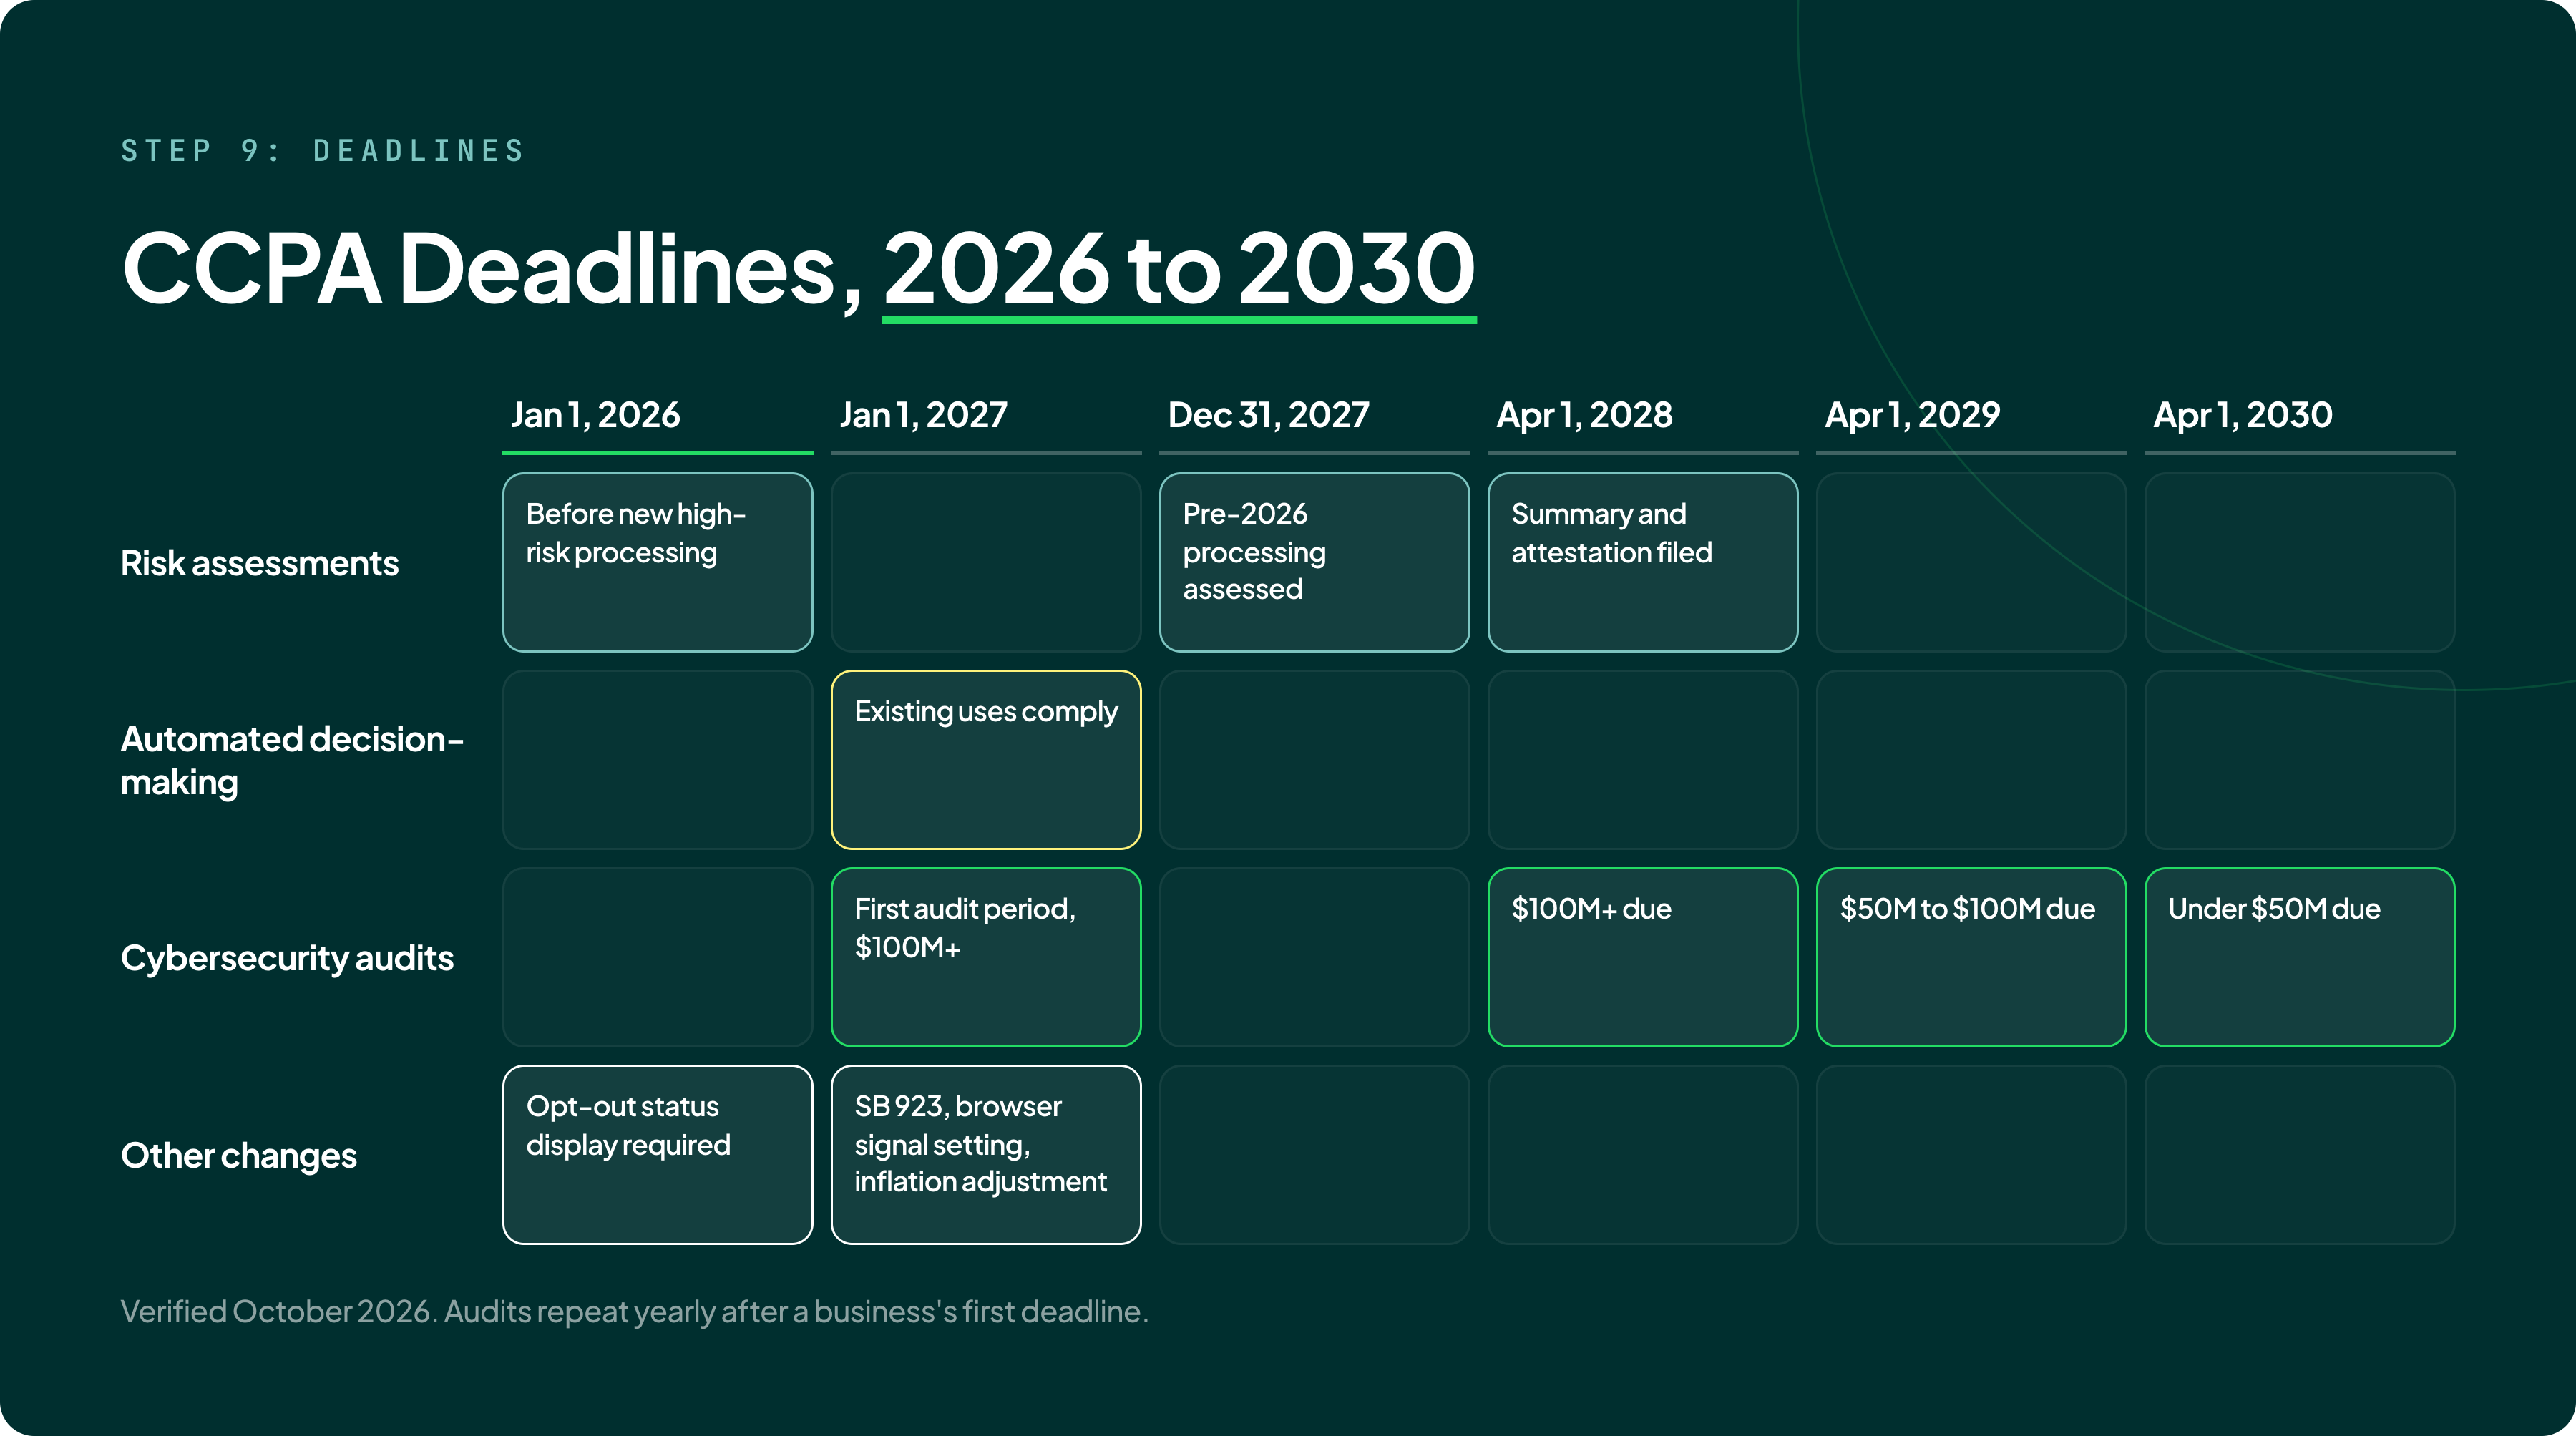
CCPA requirements and deadlines
The CCPA requires every covered business to publish privacy notices, answer consumer requests on time, keep request records, and protect personal information with reasonable security. Businesses that sell or share personal information also owe working opt-outs.
The 2026 regulations add risk assessments, automated decision-making rules, and cybersecurity audits, which phase in through 2030 and apply only to businesses doing the processing they cover. SB 923's deletion and webform changes reach covered businesses from January 1, 2027.
| Requirement | Who it applies to | When or how long | Rule |
|---|---|---|---|
| Privacy policy, updated every 12 months | All covered businesses | In force | Civ. Code § 1798.130; 11 CCR § 7011 |
| Notice at collection, with retention periods | Businesses that control the collection of personal information from consumers | In force | 11 CCR § 7012 |
| Collect, use, and keep only what each purpose needs | All covered businesses | In force | Civ. Code § 1798.100; 11 CCR § 7002 |
| Equal treatment for consumers who use their rights | All covered businesses | In force | Civ. Code § 1798.125 |
| Opt-in, notice, and a documented data value for financial incentives | Businesses that offer loyalty programs or other financial incentives | In force | 11 CCR §§ 7016, 7080 |
| Do Not Sell or Share link, the single Alternative Opt-out Link, or frictionless opt-out signal processing | Businesses that sell or share personal information | In force | Civ. Code § 1798.135; 11 CCR §§ 7013, 7025(g) |
| Honor Global Privacy Control and other opt-out signals | Businesses that sell or share personal information | In force | 11 CCR § 7025(b) |
| Show whether an opt-out signal was honored | Businesses that sell or share, on their websites | Since January 1, 2026 | 11 CCR § 7025(c)(6) |
| Stop selling or sharing after an opt-out | Businesses that sell or share personal information | Within 15 business days | 11 CCR § 7026(f) |
| Limit the Use of My Sensitive Personal Information link | Businesses that use or disclose sensitive personal information beyond permitted purposes | In force | 11 CCR § 7014 |
| Stop non-permitted uses of sensitive data after a limit request | Businesses that use or disclose sensitive personal information beyond permitted purposes | Within 15 business days | 11 CCR § 7027(g) |
| Opt-in before selling or sharing under-16 data | Businesses that know a consumer is under 16 | In force | Civ. Code § 1798.120(c) |
| Symmetrical choices and no dark patterns | All covered businesses | In force | 11 CCR § 7004 |
| Answer requests to know, delete, and correct | All covered businesses | Confirm within 10 business days; respond within 45 calendar days | 11 CCR § 7021 |
| Vendor contracts with the required terms | Businesses that disclose personal information to vendors or third parties | In force | 11 CCR §§ 7051, 7053 |
| Reasonable security for personal information | All covered businesses | In force | Civ. Code § 1798.100 |
| Breach notice to affected residents (California's breach law, separate from the CCPA) | Businesses that own or license computerized personal information | Within 30 calendar days of discovery; sample to the Attorney General within 15 days when over 500 residents are notified | Civ. Code § 1798.82 |
| Staff training on CCPA requirements | All covered businesses | In force | 11 CCR § 7100 |
| Records of consumer requests | All covered businesses | Kept for 24 months | 11 CCR § 7101 |
| Published request statistics and a written training policy | Businesses that buy, receive, sell, or share data of 10 million or more consumers a year | Statistics by July 1 each year | 11 CCR §§ 7100(b), 7102 |
| Risk assessment before new high-risk processing | Businesses doing high-risk processing, such as selling or sharing data | Since January 1, 2026 | 11 CCR § 7150 |
| Risk assessment for processing begun before 2026 | Businesses doing high-risk processing, such as selling or sharing data | By December 31, 2027 | 11 CCR § 7155(b) |
| Risk-assessment summary and attestation to CalPrivacy | Businesses doing high-risk processing, such as selling or sharing data | By April 1, 2028, then by April 1 after each year with new or updated assessments | 11 CCR § 7157 |
| ADMT pre-use notice, opt-out, and access | Businesses using ADMT for significant decisions | By January 1, 2027 for existing uses | 11 CCR § 7200(b) |
| Online request method, alongside email | Online-only businesses that deal with consumers directly | From January 1, 2027 | SB 923 |
| Deletion of data obtained from other sources | All covered businesses | From January 1, 2027 | SB 923 |
| Cybersecurity audit and certification | Businesses earning half or more of their revenue from selling or sharing, and businesses over the revenue threshold that process high data volumes | April 1, 2028, 2029, or 2030 by revenue, then yearly | 11 CCR § 7121 |
Is CCPA compliance a one-time project?
No, CCPA compliance isn't a one-time project, because several of its duties repeat on fixed cycles:
- Privacy policy: updated at least every 12 months.
- Opt-out and request methods: tested to confirm they work, which in practice means after any change to the site's tags, banner, or consent tool.
- Vendors: checked often enough to show the business had no reason to suspect misuse; 11 CCR § 7051(a)(6) gives audits at least once every 12 months as an example.
- Thresholds and dollar figures: rechecked every odd-numbered year, next on January 1, 2027.
- Risk assessments: reviewed at least every three years and updated within 45 days of a material change, under 11 CCR § 7155. A summary goes to CalPrivacy by April 1 after each year with new or updated assessments, starting 2028.
- Request records: kept for a rolling 24 months.
- Cybersecurity audits: repeated every year once a business's first deadline arrives.
When deciding whether to investigate, CalPrivacy may weigh how long a rule has been in effect and a business's good-faith efforts to comply, under 11 CCR § 7301(b).
How does CCPA compliance differ for ecommerce, SaaS, apps, and employers?
Each business model has its own weak spot under the CCPA: advertising pixels for online stores, service-provider status for SaaS companies, in-app opt-outs for apps, and staff and applicant data for any employer.
Ecommerce. Advertising pixels usually mean an online store shares personal information, so the opt-out, Global Privacy Control, and a risk assessment all apply. Loyalty programs and member discounts are financial incentives that need opt-in and a notice.
SaaS. A SaaS company's role changes with the data: data it processes for business customers can make it a service provider, if its contracts carry the CCPA's contract terms. Its own website, sign-ups, and marketing make it a covered business once it meets a threshold. As a service provider, it also has to cooperate with its customers' risk assessments and cybersecurity audits, under 11 CCR § 7050(h).
Apps, streaming, and connected devices. The opt-out has to work inside the app or on the device. When a business links a consumer's devices and services, such as through an account, the opt-out has to carry across all of them.
Employers. Job applicants and staff get a notice at collection and the same rights as customers. Monitoring that draws automated inferences about workers needs a risk assessment.
Is the CCPA opt-in or opt-out?
The CCPA is mainly an opt-out law: a business that gives the required notices can sell or share most personal information until a consumer opts out. Consent comes first in these situations:
- selling or sharing data of a consumer the business knows is under 16
- using personal information for a purpose the consumer wouldn't expect and that isn't compatible with any purpose they would expect
- enrolling a consumer in a financial incentive, such as a loyalty discount
- selling or sharing again after an opt-out, which takes a two-step opt-in under 11 CCR § 7028
- selling or sharing data collected while no opt-out notice was posted
- using sensitive personal information beyond the permitted purposes after a consumer has limited it, under 11 CCR § 7028
- using sensitive data collected while no limit notice was posted, beyond the permitted purposes, under 11 CCR § 7014(h)
Consent under the CCPA means a freely given, specific, informed, and unambiguous choice for a narrowly defined purpose, under Civil Code § 1798.140(h). Accepting broad terms of use doesn't count, and neither does hovering over, muting, pausing, or closing content.
How Enzuzo helps with CCPA opt-outs and consumer requests
Enzuzo helps with two CCPA steps: the opt-out, where most California enforcement actions so far have found violations, and consumer request handling.
Enzuzo's consent management platform lets a business add an opt-out page in minutes, where visitors can opt out or request their personal information. It also records and stores each visitor's consent preferences. On Pro and Enterprise plans, Enzuzo can detect a visitor's Global Privacy Control signal and automatically opt them out of non-essential services and cookies once GPC support is turned on.
Enzuzo's data request form is included on every plan. Consumers use it to ask for a copy of their personal information, ask for deletion, or ask that their data not be sold or shared. A business that uses the form manages and completes each request in one place.
Enzuzo doesn't write risk assessments, run cybersecurity audits, or negotiate vendor contracts; that work stays with the business's own team or its counsel.
To see the opt-out and request flows on a live site, book a demo with a CCPA compliance expert.
Frequently asked questions
Is a CPRA compliance checklist different from a CCPA compliance checklist?
No, a CPRA compliance checklist and a CCPA compliance checklist are the same list, because the CPRA amended the CCPA instead of creating a separate law. California voters approved the CPRA in November 2020. It created the California Privacy Protection Agency that year. The CPRA's business duties, including the sharing opt-out and the rights to limit and correct, took effect on January 1, 2023.
Does the CCPA apply to small businesses?
A small business is covered by the CCPA if it meets any of three thresholds, and headcount isn't one. Under $26,625,000 in revenue, a business is covered if it buys, sells, or shares data on 100,000 or more California consumers or households a year, which a busy site's ad tags can reach. So is a business earning half its revenue or more from selling or sharing data.
Does the CCPA require a cookie banner?
The CCPA doesn't require a consent banner before cookies load, because California uses an opt-out model for most visitors. A business that sells or shares data through cookies still needs a working opt-out that honors Global Privacy Control. A cookie banner alone doesn't count as that opt-out, and any banner that asks for consent has to make declining as easy as accepting.
Do businesses have to honor Global Privacy Control in California?
Yes, a business that sells or shares personal information has to honor Global Privacy Control in California, because the CCPA's regulations treat the signal as a valid opt-out of sale and sharing. Since January 1, 2026, that business also has to show on its website whether it processed the signal, and the regulation's example message is Opt-Out Request Honored. Both rules are in 11 CCR § 7025.
Can a business verify someone's identity before honoring an opt-out?
No, a business can't require identity verification, an account, or extra information to process an opt-out of sale or sharing, under 11 CCR § 7026. It can deny a request it believes, in good faith and on reasonable, documented grounds, is fraudulent, or one from an agent who can't show the consumer's signed permission. Honda, Ford, Todd Snyder, and LocateSmarter were penalized partly for verification steps on opt-outs.
Does the CCPA cover employee and B2B data?
Yes, the CCPA has fully covered data about employees, job applicants, independent contractors, and business contacts since January 1, 2023, when the temporary exemptions expired. Those people have the same rights as customers, such as access and deletion, and they're owed a notice at collection. Retaliating against an employee or applicant for using those rights is prohibited.
How long does a business have to respond to a CCPA request?
A business has 45 calendar days to respond to a request to know, delete, or correct, counted from the day it receives the request. It has to confirm receipt within 10 business days, and it can extend once by 45 more days with notice and a reason. Opt-out requests run on a shorter clock than requests to know: selling or sharing stops within 15 business days at most.
What happens if a business misses a CCPA request deadline?
A missed 45-day deadline is a CCPA violation. CalPrivacy or the Attorney General can penalize it at up to $2,663 per violation, or $7,988 if intentional, at the current adjusted amounts. Consumers can't sue over it themselves, because the CCPA lets consumers sue only over certain data breaches. A business that won't act on a request still has to tell the consumer why.
Does a business need a CCPA risk assessment?
A business needs a CCPA risk assessment if it sells or shares personal information, processes sensitive personal information beyond narrow payroll and HR uses, or uses automated decision-making for significant decisions, among other triggers. New processing needs one before it starts. Processing that began before 2026 must be assessed by December 31, 2027, and a summary with a signed attestation goes to CalPrivacy by April 1, 2028.
Does a business need a CCPA cybersecurity audit?
A CCPA cybersecurity audit is required only of two groups: businesses earning half or more of their revenue from selling or sharing data, and businesses over the CCPA's revenue threshold that handle large data volumes. That means data on 250,000 or more consumers or households in the prior year, or sensitive data on 50,000 or more consumers. First audits are due from April 2028 to April 2030.
Is there an official CCPA certification or checklist?
No, the CCPA has no certification that shows a business is compliant, and CalPrivacy publishes no official compliance checklist. The certifications the law mentions are filings a business makes about its own work. Examples are an executive's yearly cybersecurity audit certification and the risk-assessment attestation, both signed under penalty of perjury. The closest official tools are CalPrivacy's applicability questionnaire and its 2026 update guide.
Does GDPR compliance cover the CCPA?
No, GDPR compliance doesn't cover the CCPA, though a GDPR program helps with data mapping. California adds duties the GDPR doesn't have, such as the Do Not Sell or Share link and a toll-free request line for many businesses. It also requires showing whether a Global Privacy Control signal was honored. A GDPR consent banner still needs a working California opt-out, as GDPR vs CCPA explains.
What are the penalties for violating the CCPA?
CCPA fines run up to $2,663 per violation, or $7,988 for intentional violations and violations involving minors, at the current adjusted amounts. For CalPrivacy fines, that tier covers consumers a business knows are under 16. CalPrivacy and the Attorney General both enforce the law, and neither has to allow time to fix a violation first. The largest CCPA penalty so far is General Motors' $12.75 million settlement.
What changes in the CCPA on January 1, 2027?
On January 1, 2027, the CCPA's automated decision-making rules start applying to existing uses, and SB 923's deletion and webform changes take effect. Browser makers must also offer an opt-out signal setting. The same day, the dollar thresholds and fines get their next inflation adjustment. The first cybersecurity audit period also begins, for businesses with more than $100 million in 2026 revenue.
Osman Husain
Osman is the content lead at Enzuzo. He has a background in data privacy management via a two-year role at ExpressVPN and extensive freelance work with cybersecurity and blockchain companies. Osman also holds an MBA from the Toronto Metropolitan University.
LinkedIn →More related blogs
Your next read